Abandoned Popcorn Time App Vulnerability Exposed Millions
Security researchers have remotely disabled a vulnerable updater within the abandoned Time4Popcorn app, successfully closing a critical security flaw that threatened millions of computer users with remote code execution attacks.
 Radwan AbdulhadiEditor and technology writer
Overview of the Critical Vulnerability
Security researchers recently intervened to remotely disable a vulnerable updater embedded within the abandoned Time4Popcorn application, a well-known fork of the Popcorn Time BitTorrent client. According to details shared in Eye Securit notes , this emergency action effectively closed a major security flaw that could have easily allowed malicious actors to execute arbitrary code with elevated privileges on millions of computers globally.
The vulnerability itself, tracked officially as CVE-2026-30612, specifically impacted the Windows and macOS application updaters. These clients regularly contacted the project's abandoned domain, popcorntimeupd.xyz, utilizing unencrypted HTTP connections while blindly accepting incoming executables without performing any digital signature verification.
Because of this insecure update design, any third party or attacker capable of controlling the update domain could effortlessly manipulate HTTP traffic. This manipulation would allow them to successfully execute malicious code with SYSTEM privileges on Windows operating systems and root privileges on macOS computers.
Background of the Popcorn Time App
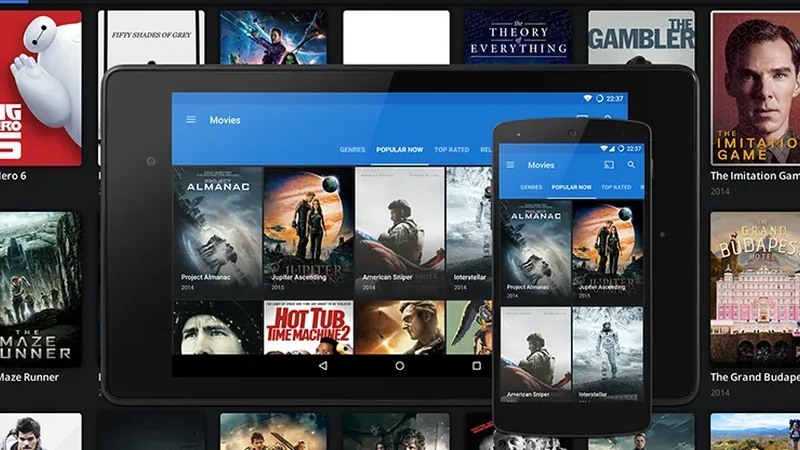
The original Popcorn Time application gained widespread notoriety by featuring a sleek, Netflix-style user interface seamlessly integrated with BitTorrent downloads. This architecture allowed everyday users to consume copyrighted video content directly inside the software interface without needing a separate torrent client.
Although the primary project was eventually abandoned due to recurring legal pressures, it was occasionally resurrected as a legal content-streaming platform. However, numerous independent forks—including Time4Popcorn—rapidly emerged under the popular Popcorn Time brand name, accumulating millions of active users before fading into abandonment.
Discovery and Scale of the Risk
Security researchers at Eye Security uncovered this latent risk after proactively registering the abandoned popcorntimeupd.xyz domain. Upon taking control of the domain, they monitored incoming telemetry and observed connections originating from approximately 3 million Windows clients and 350,000 macOS clients.
These incoming connections were traced across residential Internet Service Providers (ISPs) as well as corporate, government, and military computer networks. Interestingly, traffic patterns suggested that none of the users were actively operating the software at the time, indicating that the application had simply been installed in the past and subsequently forgotten.
Highlighting the gravity of the situation, researchers noted that if malicious actors had seized control of the infrastructure first, the impact across millions of connected machines would have been catastrophic. Additional details can be found by reviewing Eye Securit notes regarding the operation.
Remediation Operation and Transition
Following their initial discovery, the security team registered 14 additional domains associated with the defunct service infrastructure. Between November 2025 and March 2026, the researchers utilized the app's native, vulnerable update mechanism to safely deliver remediation code designed exclusively to stop and disable the updater service.
The deployed remediation payload was intentionally designed to collect zero host data or telemetry and refrained from deleting any local files on user devices, ensuring all mitigation actions remained within a strictly legal and benign context.
During deployment, the research team had to actively modify their payload to bypass local antivirus products that occasionally flagged the remediation script for stopping a running system service. Following successful deployment, researchers recorded 2 million update downloads, and by March 1, total requests directed toward the update domain had plummeted by 98 percent.
Upon the successful completion of this expansive remediation operation, domain ownership was officially handed over to The Shadowserver Foundation, a well-known non-profit security organization.
Remaining Risks and Recommendations
Despite the successful mitigation of the automated update vector on desktop computers, the researchers issued strict warnings that security risks are not fully eliminated for everyone who ever installed the software.
First, Android mobile users remain entirely exposed to potential compromise because deploying updates on the mobile platform requires direct user interaction, preventing researchers from disabling the updater remotely.
Second, the legacy Time4Popcorn application relies heavily on an ancient, severely outdated Chrome browser engine dating back to 2014. This engine completely lacks modern sandbox protections, leaving it vulnerable to alternative exploitation techniques.
Consequently, cybersecurity experts emphasize that the absolute best course of action for anyone who previously downloaded the software is to completely remove and uninstall the application from their systems.
Sources
- BleepingComputerAbandoned Popcorn Time app exposed millions of device to RCE attacks
Continue chronologically
Related stories
Abandoned Popcorn Time Apps Disabled to Prevent Botnet
Researchers remotely shut down a forgotten Popcorn Time updater to prevent hackers from transforming millions of vulnerable devices into a massive botnet army.
Siemens Software Center Vulnerability Exploited in ClickFix Attacks
Siemens reveals active exploitation of a DLL side-loading vulnerability in its Software Center linked to the Romulus ClickFix malware delivery campaign.
GitLab Warns of Max Severity Code Execution Flaw
GitLab has released urgent security patches for a maximum-severity integer overflow vulnerability in its Regular Expression Compiler engine.
Drupal Patches Critical RCE Vulnerabilities and Warns
Drupal has issued patches for two critical remote code execution vulnerabilities affecting supported versions and warned of potential exploits.