Siemens Software Center Vulnerability Exploited in ClickFix Attacks
Siemens has disclosed that a security flaw in its Software Center application has been actively exploited in the wild, becoming integrated into a broader multi-platform attack campaign.
 Radwan AbdulhadiEditor and technology writer
Vulnerability Overview and Disclosure
Siemens revealed that threat actors have exploited a vulnerability in Siemens Software Center as part of a malware campaign. The application is responsible for handling the download, installation, activation, and updating of customer-purchased software, as well as initiating free trials. The security flaw, tracked as CVE-2026-110936, stems from the program failing to properly restrict the locations it searches for dynamic-link library files.
An authenticated local attacker could exploit this behavior by planting a malicious DLL in one of the searched folders, triggering code execution with the same privileges as the Software Center. Siemens disclosed the vulnerability in an official product advisory, which was subsequently updated with details on active exploitation. Detailed information regarding the active exploitation of CVE-2026-110936 in Siemens Software Center can be found in the company's dedicated blog post.
Remediation and Automatic Updates
Siemens assigned the vulnerability a CVSS v4 score of 8.4 upon its initial disclosure. Two days later, the company updated its guidance to inform customers that version 4.0.9.8 successfully resolves the issue. Users who already have the application installed will receive the fix automatically the next time they launch the software.
The company stated that version 3.5.8.7, which was the newest release at the time of discovery, did not adequately validate helper files before loading them. Huntress researcher Jose Oregon has been officially credited with reporting the underlying vulnerability to Siemens. Further details and remediation instructions are available directly through the official Siemens product advisory.
Nature of the Attack and Campaign Links
In the observed attacks, threat actors paired a legitimate, validly signed copy of the Siemens Software Center program with malicious DLL files of their own supply. When the program initiated, it loaded these helper files directly from its own directory. Siemens emphasized that its software was not physically tampered with and that the malicious package was not distributed through official Siemens distribution channels.
“No Siemens system, product or update channel was breached to our knowledge,” the company stated. To assist defenders, Siemens is actively sharing threat intelligence with relevant authorities and Endpoint Detection and Response (EDR) providers. Because the core executable file involved in the attacks is a legitimate, signed Siemens binary, the company recommends that security teams focus on identifying suspicious system behavior and associated folder structures rather than relying solely on traditional file hashes.
Connection to the Romulus ClickFix Campaign
Siemens has formally linked the malicious activity to Romulus, a sophisticated operation utilizing ClickFix deployment tactics. ClickFix attacks typically rely on deceptive user prompts—such as fake CAPTCHA verification warnings—that trick users into manually copying and executing malicious commands on their own workstations. Security researchers have tracked this emerging threat landscape extensively across multiple attack vectors.
Independent analysis published by security firms has shed light on the infrastructure behind these incidents. Research into the Romulus delivery platform revealed that it operates across several servers, including the specific server identified by Siemens as the distribution point for the malicious bundle containing its software. Analysts observed the platform distributing payloads such as LegionLoader and trojanized installers leveraging other vendors' signed applications for side-loading.
Sources
- SecurityWeekSiemens Software Center Vulnerability Exploited in ClickFix Malware Attacks
Continue chronologically
Related stories
CISA Warns of Actively Exploited Plex Flaws in Attacks
CISA warns that hackers are actively exploiting four chained Plex Media Server vulnerabilities, known as Plex2Shell, to breach servers.
Unpatched AhsayCBS Flaws Exploited for Webshells
Threat actors are actively exploiting unpatched critical and medium-severity vulnerabilities in the AhsayCBS backup management platform.
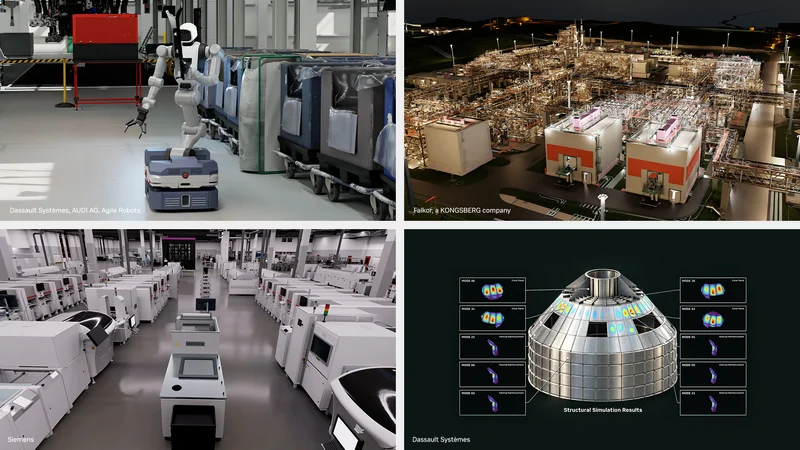
Europe's Industrial Leaders Reinvent Engineering with NVIDIA
Europe's industrial leaders are adopting NVIDIA CUDA-X, Omniverse, Cosmos, and Nemotron models to transform engineering and manufacturing operations.
Unpatched AhsayCBS Flaws Exploited in the Wild
Cybersecurity researchers warn that unpatched vulnerabilities in the AhsayCBS backup solution are being actively exploited in the wild for remote code execution.