GitLab Warns of Max Severity Code Execution Flaw
GitLab has released urgent security patches addressing a maximum-severity remote code execution vulnerability impacting multiple Community Edition and Enterprise Edition versions.
 Radwan AbdulhadiEditor and technology writer
Maximum Severity Vulnerability Identified
GitLab has released security patches for a maximum-severity Regular Expression Compiler flaw that can let remote attackers run arbitrary code on vulnerable servers, as reported by BleepingComputer. This security issue is tracked as CVE-2026-110264 and was discovered by a security researcher using the 'joaxcar' handle through GitLab's HackerOne bug bounty program.
According to the advisory, the vulnerability stems from an integer overflow weakness in GitLab's Regular Expression Compiler, which functions as a background engine that parses and validates regular expressions found in configuration files. Researchers and administrators can review technical details regarding the integer overflow weakness through MITRE's classification.
Affected Versions and Remediation
GitLab has fixed the vulnerability across multiple software iterations. The fixes apply to GitLab Community Edition (CE) and Enterprise Edition (EE) versions 19.5.1, 19.4.3, 19.3.6, 19.2.9, 19.1.9, 19.0.10, and 18.11.13. Platform administrators have been strongly warned to patch their instances immediately.
Detailed information about the specific patch release can be found in official documentation, and further instructions are available where the company said that users should upgrade promptly. GitLab.com is already running the patched version, while GitLab Dedicated tenants running specified internal builds already include these fixes without requiring further direct user action.
Scope and Exposure Online
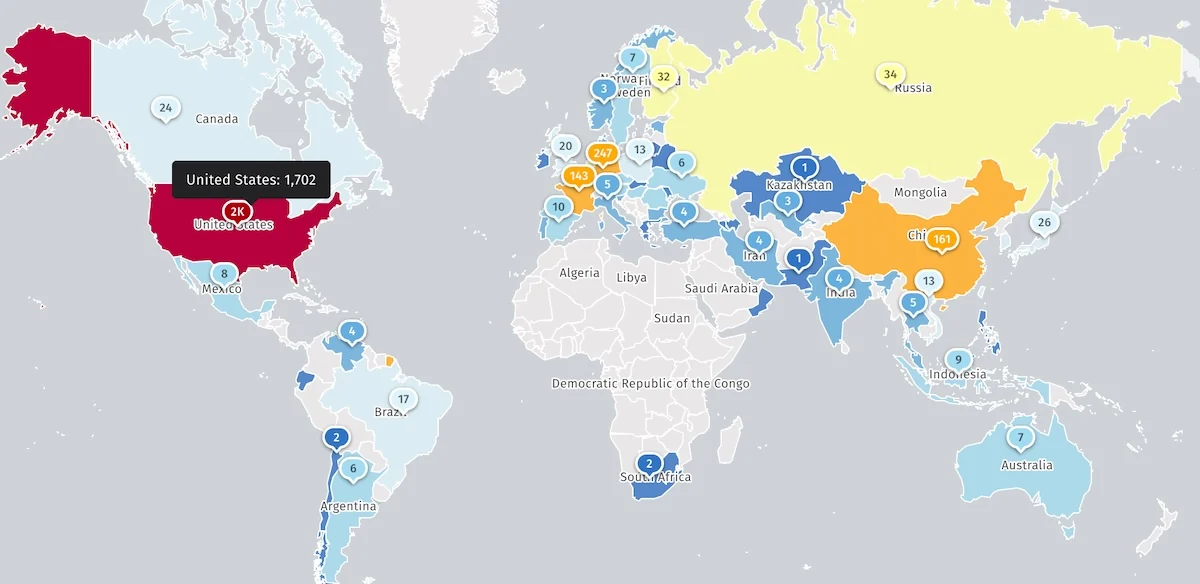
Internet threat watchdog Shadowserver currently tracks over 2,700 GitLab Community Edition instances exposed online. However, the organization notes that current statistics do not provide any definitive information regarding how many of these servers are honeypots or have already been secured against active exploitation attempts.
This security advisory follows recent warnings issued by the platform regarding critical infrastructure components. GitLab previously warned customers ten days ago about another critical remote code execution vulnerability carrying a maximum CVSS score in a related engine.
Broader Security Context
The platform has experienced multiple high-severity security incidents in recent months. Last month, developers fixed another maximum-severity GitLab CE/EE flaw that permitted unauthenticated attackers to read sensitive data, such as credentials and other secrets, directly from vulnerable servers.
Following that disclosure, the U.S. Cybersecurity and Infrastructure Security Agency added the related bug to its catalog of actively exploited flaws and ordered federal agencies to secure their systems within a strict three-day timeframe. Since November 2021, CISA has flagged five separate GitLab security issues used in the wild, including vulnerabilities leveraged in active ransomware attacks.
Sources
- BleepingComputerGitLab warns of new max severity code execution vulnerability
Continue chronologically

Related entity coverage
Related stories
CISA Confirms Active Exploitation of Maximum-Severity GitLab Flaw
CISA confirms active exploitation of a maximum-severity GitLab vulnerability tracked as CVE-2026-97229 and urges administrators to apply patches immediately.

Max-Severity GitLab Flaw Exploited Against Alpine Linux
A max-severity code execution vulnerability in GitLab was targeted in an attack against Alpine Linux's instance just one week after disclosure.
CISA Warns Ransomware Gangs Are Exploiting TeamCity Flaw
CISA alerts federal agencies that ransomware gangs are now actively exploiting a critical JetBrains TeamCity authentication bypass vulnerability.
Alpine Linux Rebuilds GitLab Server After Attack
Alpine Linux rebuilt its GitLab development server and forced password resets following an attempted remote code execution attack.