GitHub Adds AI Scan Metrics to Security Overview
GitHub is expanding its security overview with metrics for AI Scan on pull requests. The public preview is designed to help security teams measure findings, remediation and developer adoption across organizations and enterprises.
 Radwan AbdulhadiEditor and technology writer
AI Scan metrics arrive in security overview
GitHub has added AI Scan metrics to its security overview, giving organization and enterprise administrators a way to observe the impact of AI Scan for pull requests. The company announced the change in the GitHub Changelog, describing a set of reporting tools intended to show how AI-powered security detections are being used across an organization or enterprise.
The new reporting data includes the number of AI Scan findings generated and resolved, along with the remediation rate. Administrators can also identify which repositories generated findings and review trends over a selected reporting period. Together, the metrics provide a broader view of AI Scan activity without requiring security teams to inspect pull requests individually.
A separate view for AI-powered findings
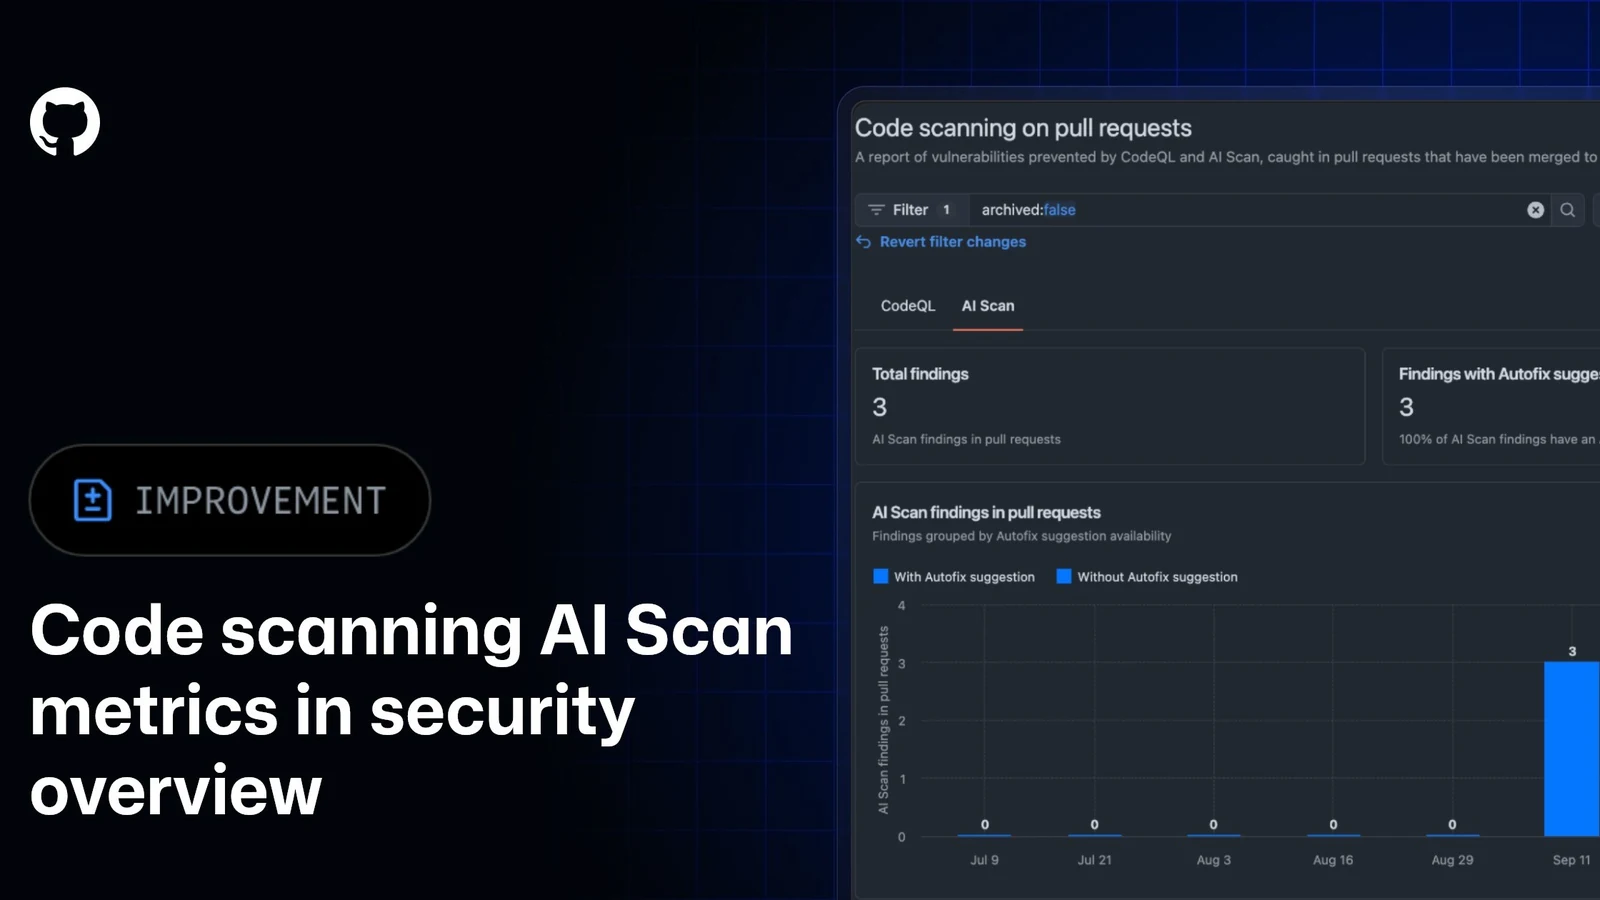
As part of the update, GitHub has renamed the “CodeQL pull requests” page to “Code scanning on pull requests.” The page now separates CodeQL reporting from AI Scan reporting through dedicated tabs, making it possible to review the two sets of metrics independently.
The AI Scan tab displays the total number of findings and distinguishes between findings that include an autofix suggestion and those that do not. Metrics previously shown on the “CodeQL pull requests” page now appear under the CodeQL tab, preserving that reporting area while adding a separate location for AI Scan results.
Tracking remediation and developer response
GitHub’s new metrics also measure how developers respond to AI Scan output. The security overview shows how often developers applied autofix suggestions, allowing administrators to compare generated findings with the fixes that were acted on during the reporting period.
The company says these measurements can help security teams evaluate AI Scan’s effectiveness across their organization or enterprise. They are also intended to show developer response and support decisions about rollout and investment, using aggregate reporting rather than a review of individual pull requests.
Public preview availability
The AI Scan security overview metrics are available in public preview on github.com, including GitHub Enterprise Cloud. Access is limited to customers with GitHub Code Security or GitHub Advanced Security, according to GitHub’s announcement.
GitHub Enterprise Server is not supported for this release. The company has directed users looking for product details to its documentation on [AI Scan for pull requests](https://docs.github.com/code-security/concepts/code-scanning/ai-powered-security-detections) and invited them to join the [AI Scan Community discussion](https://github.com/orgs/community/discussions/201543).
A broader view of code-scanning activity
The update places AI Scan activity alongside existing code-scanning information in a single security overview. By separating AI Scan and CodeQL tabs, GitHub gives administrators distinct reporting surfaces for the two analysis approaches while retaining a shared view of pull-request security activity.
For teams assessing the use of AI Scan, the available measures cover the path from detection to remediation: findings generated, findings resolved, repositories involved, reporting-period trends and autofix adoption. The preview therefore focuses on operational visibility and evaluation rather than introducing a new finding type or changing the underlying pull-request workflow.
Sources
- GitHub ChangelogCode scanning AI Scan metrics in security overview
Continue chronologically
Related entity coverage
Related stories
GitHub expands AI Scan beyond CodeQL default setup
GitHub’s AI Scan for pull requests can now detect security vulnerabilities without CodeQL default setup, in public preview for eligible customers.
AI Scan for Pull Requests Generally Available on GitHub
GitHub announces general availability of AI Scan for pull requests, complementing CodeQL by finding vulnerabilities in additional frameworks and languages.
GitHub Adds AI Scan Enablement Status to Security Overview
Organization and enterprise administrators can now track AI Scan for pull requests enablement status directly in the GitHub security overview coverage view.
GitHub Introduces Dependabot Reachability Analysis Preview
GitHub launches reachability analysis for Dependabot alerts in public preview, helping teams prioritize JavaScript and TypeScript vulnerabilities.