GitHub Introduces Dependabot Reachability Analysis Preview
A new public preview on GitHub brings reachability analysis to Dependabot alerts, offering JavaScript and TypeScript developers deeper context on dependency vulnerabilities without requiring a GitHub Advanced Security license.
 Radwan AbdulhadiEditor and technology writer
Understanding Dependabot Reachability Analysis
Managing security vulnerabilities in software projects can quickly overwhelm development teams as alerts accumulate. Finding a vulnerable package in a dependency tree does not automatically mean that application code actually utilizes the vulnerable components. To help address this challenge, GitHub has announced a public preview for reachability analysis, providing developers with additional context when deciding which vulnerabilities to remediate first. Further details are available from GitHub Changelog in the original source material.
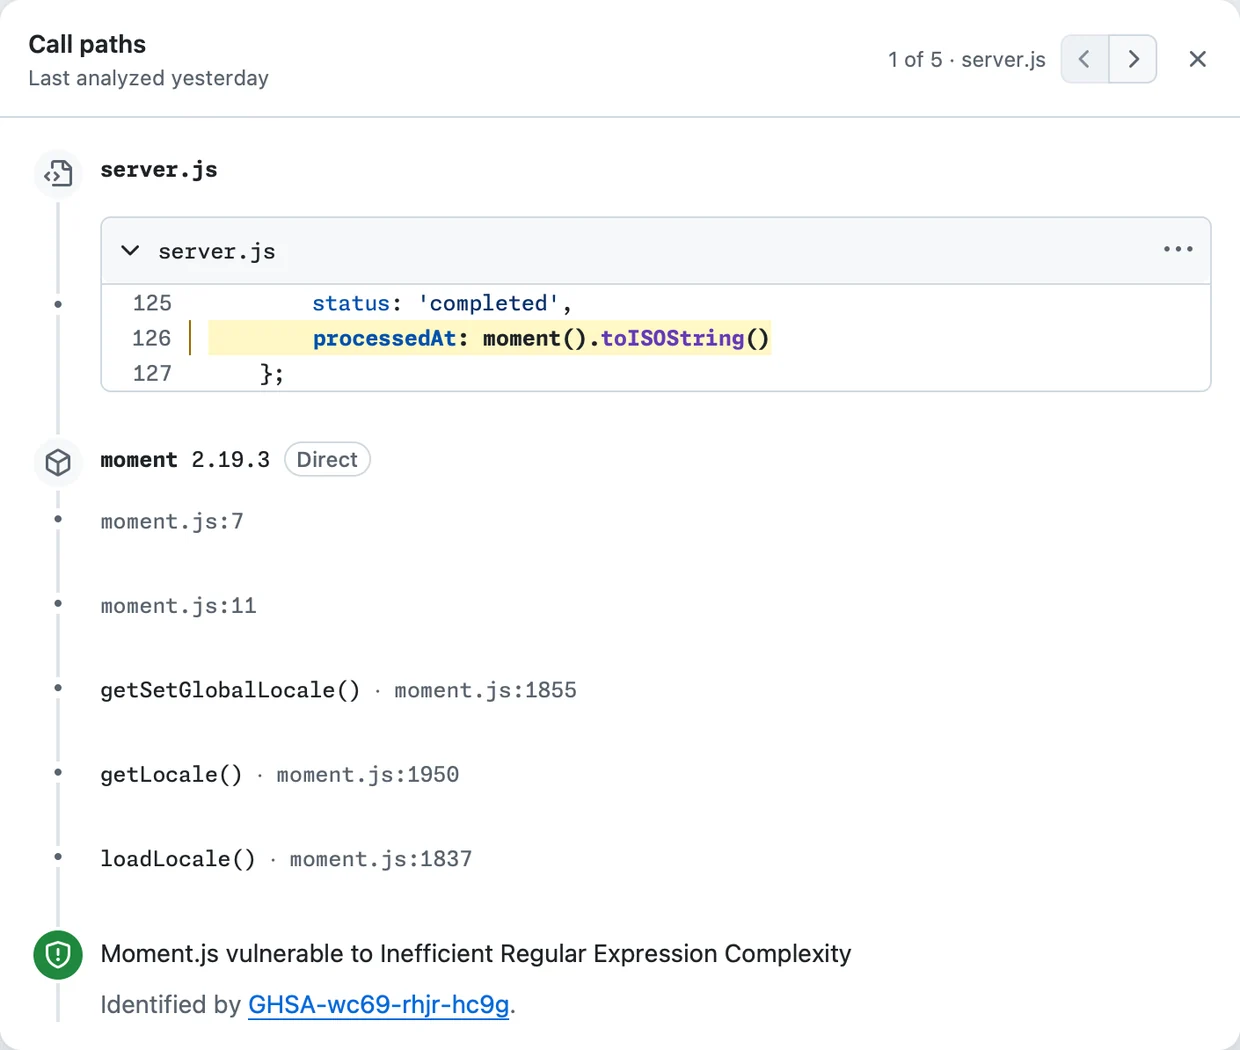
The new capability works alongside existing metrics like severity scores, EPSS scores, production context, and developer knowledge. By examining call paths from application code to vulnerable functions within dependencies, the system surfaces clear evidence directly on each alert, streamlining the triage process for engineering teams.
How the Analysis Works
Dependabot executes reachability analysis automatically through a managed GitHub Actions workflow, meaning teams do not need to manually install or maintain infrastructure. For each advisory, the system leverages curated data identifying vulnerable functions inside affected packages. CodeQL constructs a comprehensive call graph spanning the repository and its dependencies to search for active paths from application code to those functions.
To learn more about how this mechanism operates behind the scenes, developers can review the documentation provided on the platform.
Understanding Verdicts and Prioritization
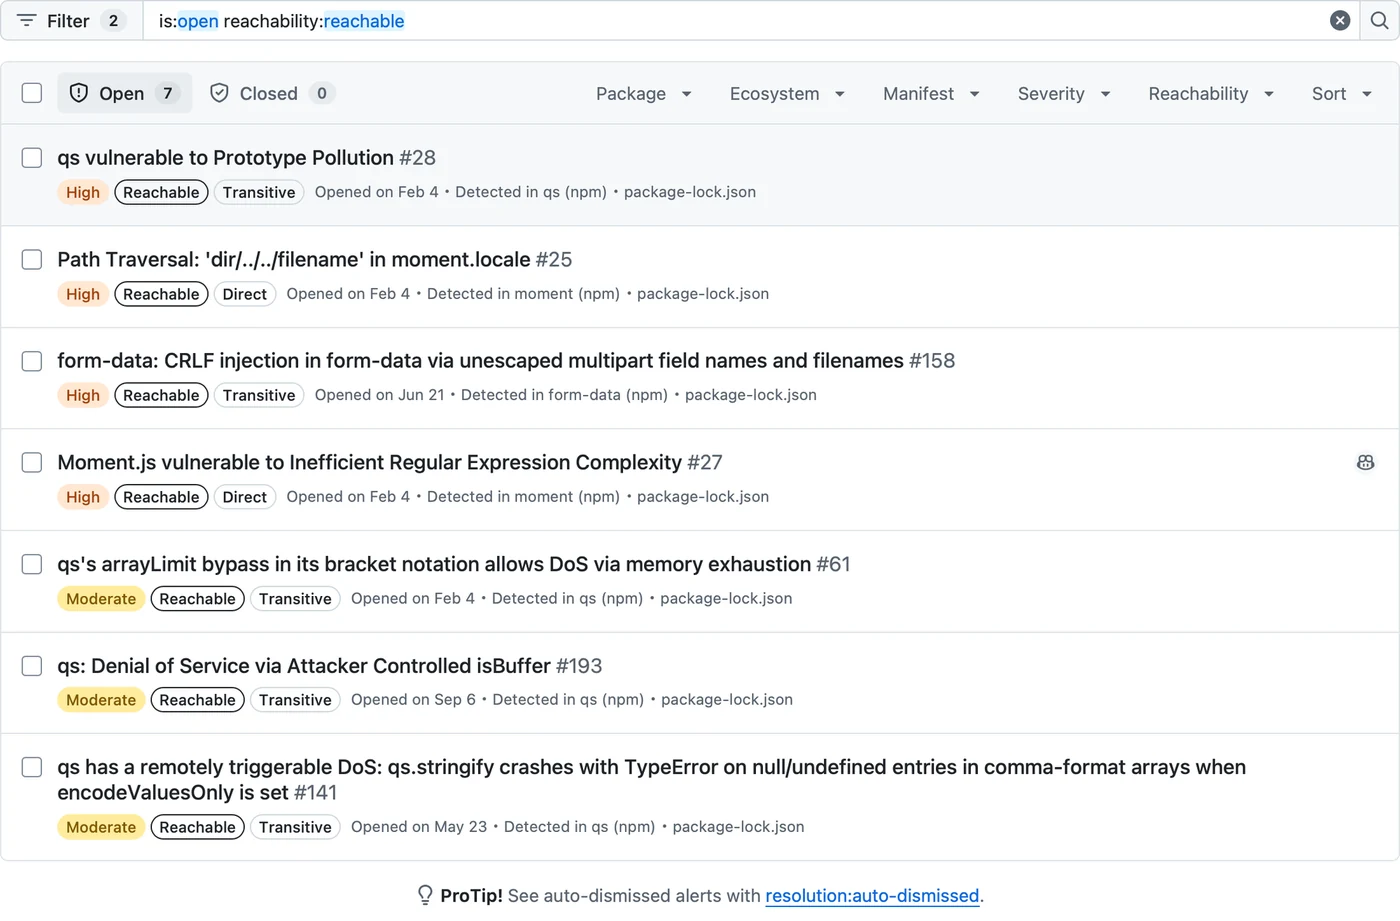
Each open Dependabot alert receives a specific verdict determined by the analysis. A verdict of "Reachable" indicates that application code contains at least one call path to the vulnerable function. "Potentially reachable" is assigned when the analysis cannot definitively determine whether code calls the vulnerable function, and these alerts should be treated as reachable.
Conversely, "Unreachable" means the analysis finished successfully and found no call path, designating these alerts as lower priority. If an alert cannot be analyzed at all, it is marked as "Reachability unavailable" and should be triaged normally. These verdicts are integrated directly into existing Dependabot alert pages without ever automatically closing or dismissing alerts.
Availability, Pricing, and Configuration
The reachability analysis feature is provided free of charge for GitHub Enterprise Cloud customers, including those using GitHub Enterprise Cloud with data residency. Organizations are not billed for the GitHub Actions minutes consumed by the analysis, and a GitHub Advanced Security license is not required to utilize the tool.
During the public preview, the feature supports JavaScript and TypeScript projects that utilize an npm, Yarn, or pnpm lockfile. The analysis executes on GitHub-hosted runners, as self-hosted runners are unsupported during this phase. Teams can enable reachability analysis across multiple repositories simultaneously by setting up a custom security configuration at the organization or enterprise level, or activate it individually within specific repository settings.
Scan Frequency and Community Feedback
Initial scans begin immediately after activation and typically complete within minutes to a few hours, depending on repository scale. Following the first scan, the platform reruns analyses daily as long as open Dependabot alerts remain present, ensuring verdicts adapt accurately to changes in source code and underlying advisories.
Developers wishing to share questions, report issues, or provide feedback on the new reachability analysis preview are encouraged to participate in the designated community discussion.
Sources
- GitHub ChangelogPrioritize Dependabot alerts with reachability analysis
Continue chronologically
Related entity coverage
Related stories
AI Scan for Pull Requests Generally Available on GitHub
GitHub announces general availability of AI Scan for pull requests, complementing CodeQL by finding vulnerabilities in additional frameworks and languages.
GitHub Deprecates All-Platform CodeQL Bundle
GitHub has officially deprecated the all-platform CodeQL bundle, directing users to adopt platform-specific binaries starting with version 2.27.0.
GitHub Introduces Improved Detection for Withdrawn Dependabot Alerts
GitHub has rolled out two key updates to help developers easily detect withdrawn Dependabot alerts via webhooks and REST API updates.
GitHub Introduces Repository Custom Runner Settings for Dependabot
Repository administrators can now configure runner types, custom labels, and runner groups for Dependabot version and security updates.