Eiliko Maker Hires Security Firm After Robot Data Breach Report
Eiliko maker Energize Lab is hiring an independent security firm after a report revealed serious vulnerabilities in its AI-powered robot charm.
 Radwan AbdulhadiEditor and technology writer
Security Concerns Prompt Response
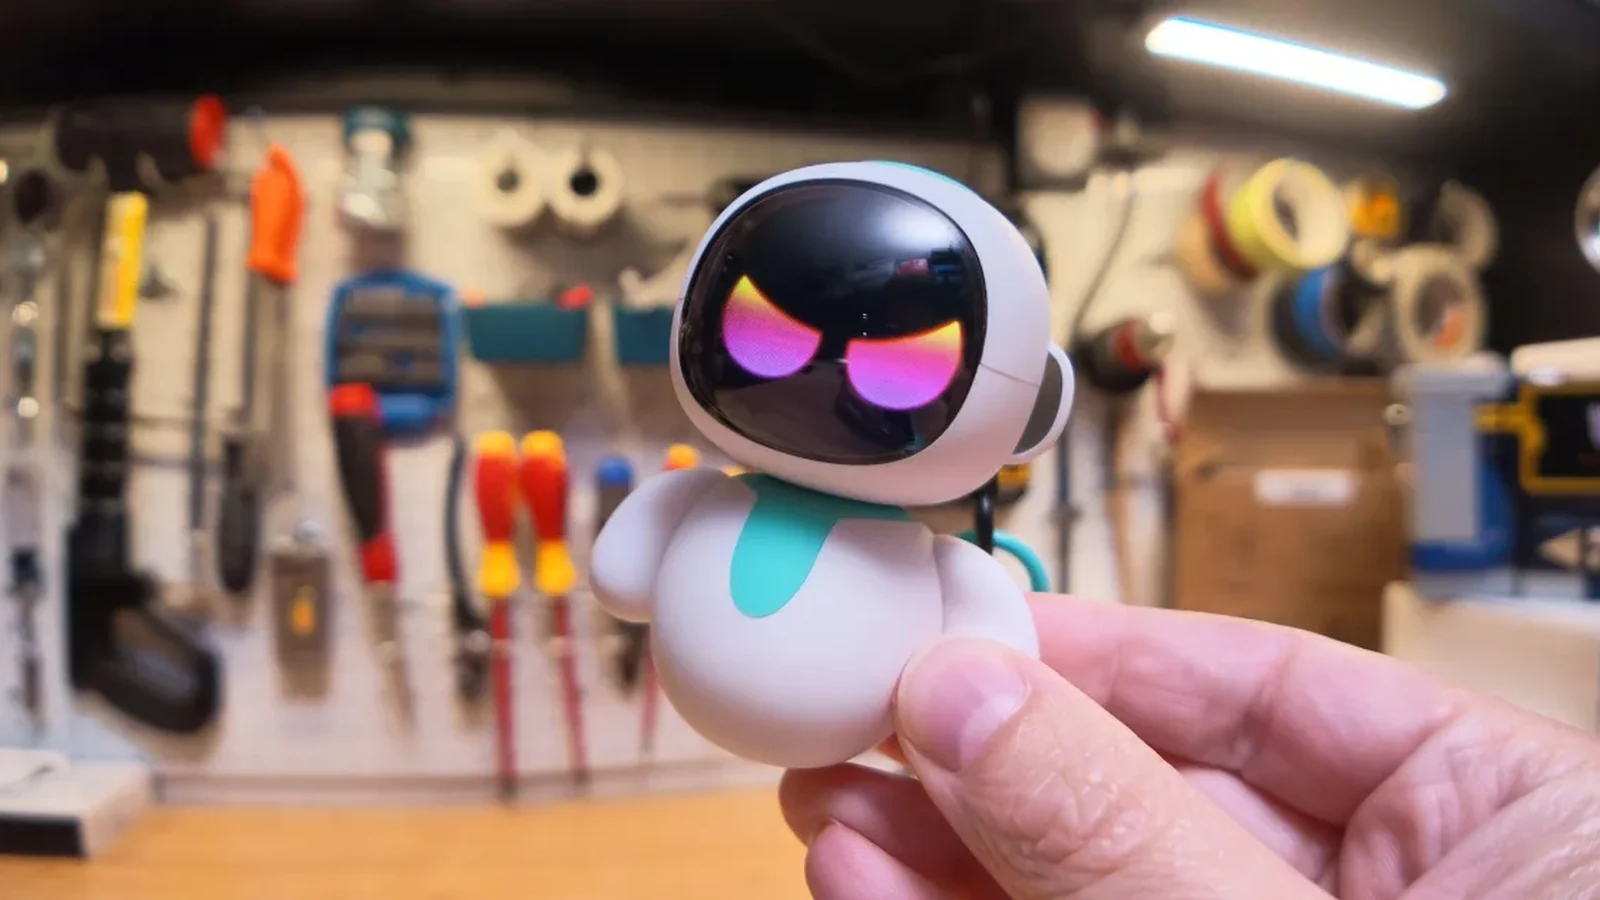
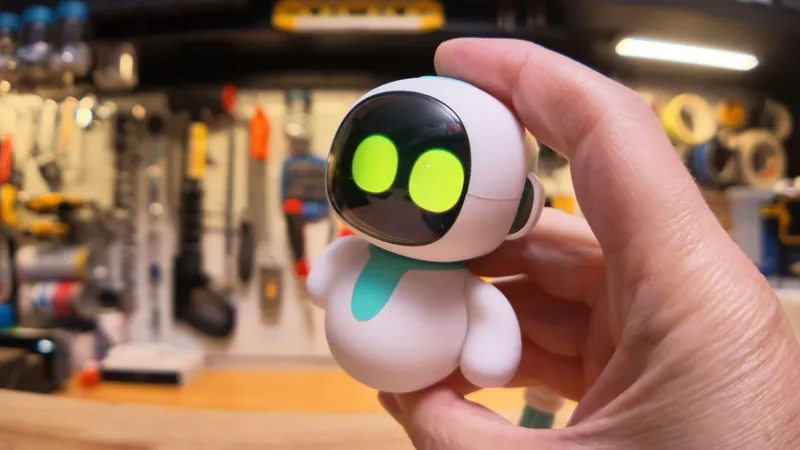
Eiliko, a small AI-powered robot charm designed to hang on bags and engage in conversation, has come under scrutiny after a report revealed significant security vulnerabilities. The device, marketed as a friendly companion, was found to be storing and exposing sensitive user data, including full conversation transcripts and personal images. The Verge reported that hackers could easily access this information, raising serious concerns about privacy and data protection. In response, Energize Lab, the company behind Eiliko, announced it is hiring an independent security firm to conduct a full review of its systems.
Researcher Reveals Ongoing Risks
Security researcher Sammy Azdoufal, who worked with The Verge on the investigation, stated that despite Energize Lab’s claims of closing external access, critical vulnerabilities remain. Azdoufal reported that he still has full SSH access to Eiliko robots and can potentially read transcripts and modify device behavior. Additionally, he confirmed that customer audio recordings and photos were still accessible via unsecured public web addresses at the time of the company’s statement. These findings suggest that the security issues may be more extensive than initially addressed.
Company Statement and Actions
In an unsigned statement sent from a generic email address, Energize Lab acknowledged the issues and outlined several measures it claims to have taken. The company said it has closed all external access to its backend systems, rotated access credentials, and disabled the interface that allowed remote modification of robot responses. It also stated that it has taken the long-term memory and custom avatar features offline and will no longer store conversation records or user profiles generated from them. Energize Lab added that it will delete previously stored data, including avatar images.
Data Deletion and Future Plans
Energize Lab confirmed that it will delete stored conversation records, user profiles, avatar images, and related content. However, the company did not rule out future data collection. It stated that the long-term memory and custom avatar features will not return until an independent security review confirms they are secure. The firm also set up a dedicated security inbox, security@energizelab.com, which it says is staffed and monitored. Despite these steps, the company admitted that rebuilding trust will require more than words.
Ongoing Skepticism from Researchers
While Energize Lab’s response includes concrete steps, researchers remain skeptical. Azdoufal and other security experts have questioned the accuracy of the company’s claim that all external access has been closed. The continued presence of unsecured public web addresses hosting customer data further undermines confidence in the company’s remediation efforts. The Verge noted that Energize Lab did not respond to repeated inquiries for over a month, only breaking its silence after the publication of the initial report.
Broader Implications for Consumer Robotics
The Eiliko incident highlights growing concerns around data privacy in consumer robotics and AI-powered devices. As more companies integrate conversational AI and cloud-based features into everyday products, the risk of data exposure increases. Security experts have long warned that many IoT and smart devices lack adequate safeguards. The case also underscores the importance of responsible disclosure and timely responses from manufacturers when vulnerabilities are reported.
Sources
- The VergeEiliko maker says it’s hiring an ‘’independent security firm’ after Verge report on its insecure robots
Continue chronologically
Related stories
Eiliko Robot Toy Vulnerabilities Expose User Data in China
An investigation reveals that Energize Lab's Eiliko robot toy and its AI companion store millions of insecure conversations on Chinese servers.
Squarespace Lays Off 19% of Workforce in Restructuring
Website builder Squarespace is cutting about 19% of its global workforce, affecting around 300 employees as part of an organizational restructuring.
How Overhead Projectors Transformed Classrooms and Learning
Explore the history of the overhead projector, a military technology that became a ubiquitous classroom fixture, changing how students learned.
Why the LeapPad Couldn't Survive the iPad
Explore the history of the LeapFrog LeapPad, how a smart book became a top-selling toy, and why it struggled to keep up with the iPad.