Eiliko Robot Toy Vulnerabilities Expose User Data in China
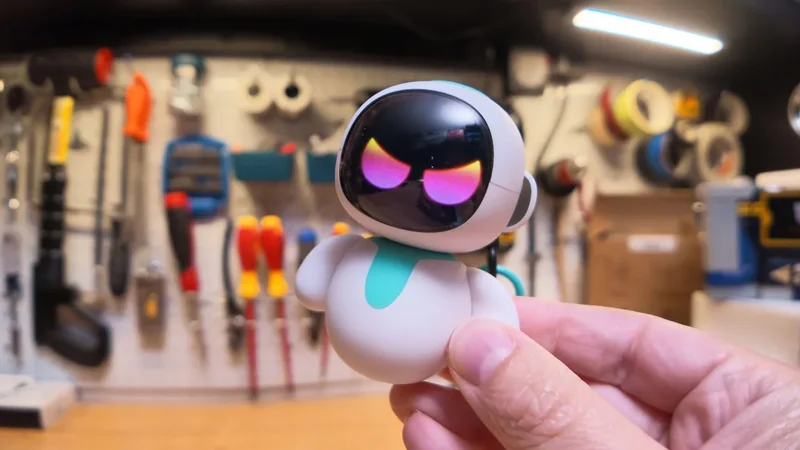
Security researchers have uncovered severe vulnerabilities in the Eiliko robot toy manufactured by Energize Lab, exposing millions of user conversations and personal profiles on unsecured Chinese servers.
 Radwan AbdulhadiEditor and technology writer
Severe Security Flaws Discovered in Eiliko Robot Toys
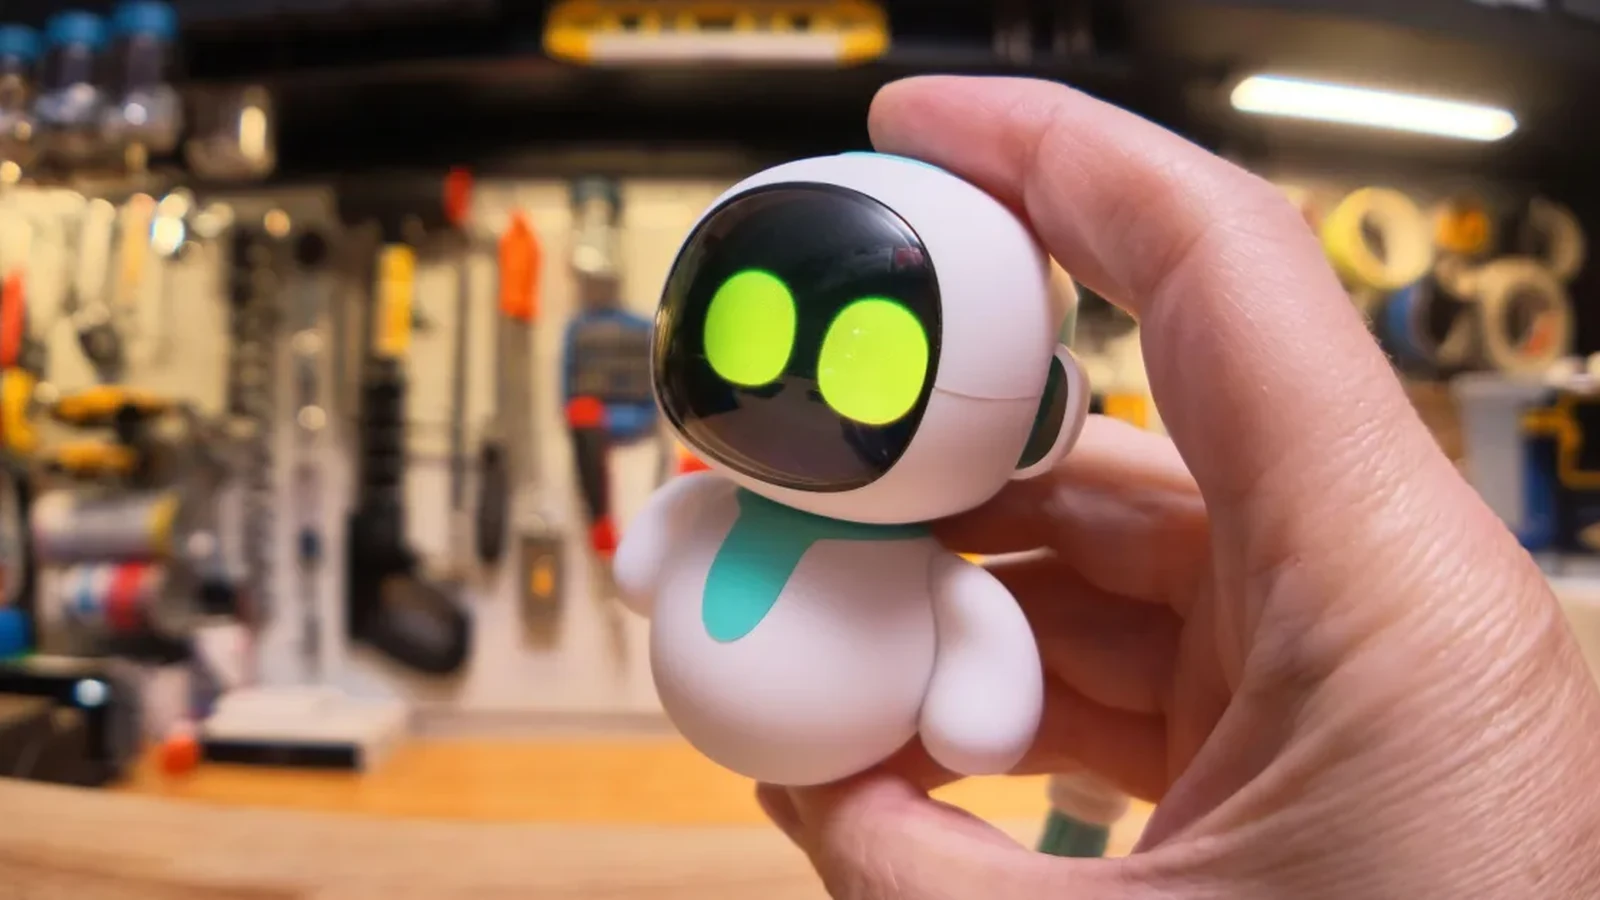
A newly popular digital pet known as Eiliko, manufactured by Energize Lab, contains severe security vulnerabilities that transmit private conversations over Wi-Fi to servers located in China. The AI companion built into the device stores vast amounts of user data in an insecure environment where malicious actors can readily gain access or hijack the device's personality.
Security researcher Sammy Azdoufal, known for previous investigations into connected hardware such as smart home devices and security systems, purchased an Eiliko toy to test its companion app. Azdoufal quickly discovered that the manufacturer's backend service was entirely unprotected and actively profiled users around the globe without adequate security safeguards.
Millions of User Conversations and Profiles Exposed
Testing revealed that within minutes of interacting with the toy, a complete transcript of conversations could be intercepted from the other side of the planet. The exposed database contained 13 million conversations gathered from tens of thousands of users worldwide. According to the collected data, the largest market for the robot toy is the United States, where more than 31,000 user profiles belong to children.
Beyond basic IP addresses and location data, Azdoufal found that the system reads conversations and constructs detailed personal profiles. These profiles include names, ages, birthdays, professions, relationships with family and friends, and evaluations of the user's personality traits and emotional states.
The platform stored sensitive snippets of text, including queries regarding personal distress and mental health. Furthermore, unencrypted photographs and short audio recordings captured by the devices were discovered stored at public web addresses, accessible without authorization.
Contradictions With Company Privacy Policies
The data collection practices observed by researchers directly contradict official corporate statements. Energize Lab's privacy policy states that audio recordings are encrypted, transmitted to service partners such as Alibaba Cloud for processing, and deleted immediately after processing completes.
Despite these written assurances, researchers found that the platform retained audio clips and unencrypted files on public web servers. Additionally, administrative passwords utilized by the infrastructure matched common default credentials found on standard vulnerability lists, reflecting a broader lack of security mindfulness within the organization.
Remote Hijacking and Personality Manipulation
The security flaws extend far beyond passive data collection, allowing external parties to take active control of the hardware. Researchers demonstrated that a remote attacker could successfully hack the toy's memory and hijack its large language model from thousands of miles away.
During remote testing, the compromised robot delivered altered factual claims and aggressive statements to users. Although the device's language model retained certain baseline safety guardrails regarding extreme dangers, the overarching vulnerabilities demonstrated that malicious actors could manipulate the entire global fleet of connected devices simultaneously.
Manufacturer Response and Official Documentation
Efforts by investigators and journalists to contact Energize Lab regarding the massive security breach yielded virtually no substantive response. Over a month of outreach directed to company founders, public relations teams, marketing staff, and technical support channels produced generic automated replies or brief acknowledgments from overseas sales management without meaningful engagement.
Detailed documentation of the security flaws has been compiled by researchers in coordination with vulnerability tracking projects. Comprehensive technical data and official vulnerability reports detailing the platform weaknesses are publicly documented for industry awareness.
Sources
- The VergeYour secrets aren’t safe with this cute robot toy — they’re on Chinese servers ready to be hacked
Continue chronologically
Related stories
Eiliko Maker Hires Security Firm After Robot Data Breach Report
Energize Lab responds to The Verge report on Eiliko robot security flaws, hiring an independent firm to review systems and delete user data.
Deploying Real-Time Voice Cloning on Amazon SageMaker AI
Learn how to deploy the Qwen3-TTS-12Hz-1.7B-Base text-to-speech model on Amazon SageMaker AI for real-time voice cloning and cross-lingual synthesis.
Chainalysis Discloses Data Breach From Offensive Agentic Techniques
Blockchain intelligence firm Chainalysis discloses a security breach involving offensive agentic techniques that exposed customer names and emails.
Bluesky Blocks Links to Leaked DHS Personnel Data
Social network Bluesky blocks links to a leaked archive of Department of Homeland Security employee records, citing policy violations.