Switch 2 security hit as hackers unlock homebrew
A security researcher has demonstrated a software-only partial jailbreak of the Switch 2, granting userland access to run homebrew and mod games.
 Radwan AbdulhadiEditor and technology writer
Switch 2 Security Compromised by Userland Exploit
A security researcher has demonstrated a software-only partial jailbreak of the Switch 2, gaining userland access that enables running homebrew, reverse engineering and modding Switch 2 games, backing up save files, and accessing most peripherals through MMIO. Detailed information regarding the method is available through Ars Technica.
The hack relies on the original Switch version of SmileBasic 4, a long-running series of programming environments and interpreters that run on Nintendo hardware. Technical specifics of the tool can be reviewed via The hack.
Discovery Process and Technical Mechanism
Researcher Sammy Hajhamid writes that he used OpenAI’s Codex to examine SmileBasic’s language interpreter with a custom harness capable of sending USB commands and viewing results via HDMI. Additional details on the process are documented where he writes about the vulnerability.
After roughly two weeks of effort, the harness discovered a 32-bit integer overflow occurring when items are removed from an array in SmileBasic. This error provides an array pointer that grants read and write access to portions of system memory. Further details about the underlying software can be found through SmileBasic 4.
Privileged Access and Proof of Concept
Following the initial memory access, Hajhamid investigated internal sysmodules to locate functions providing more privileged access to core console operations. He eventually identified a buffer overflow in the console's FileSystem services module, exposing a cached data pointer and granting arbitrary read and write privileges.
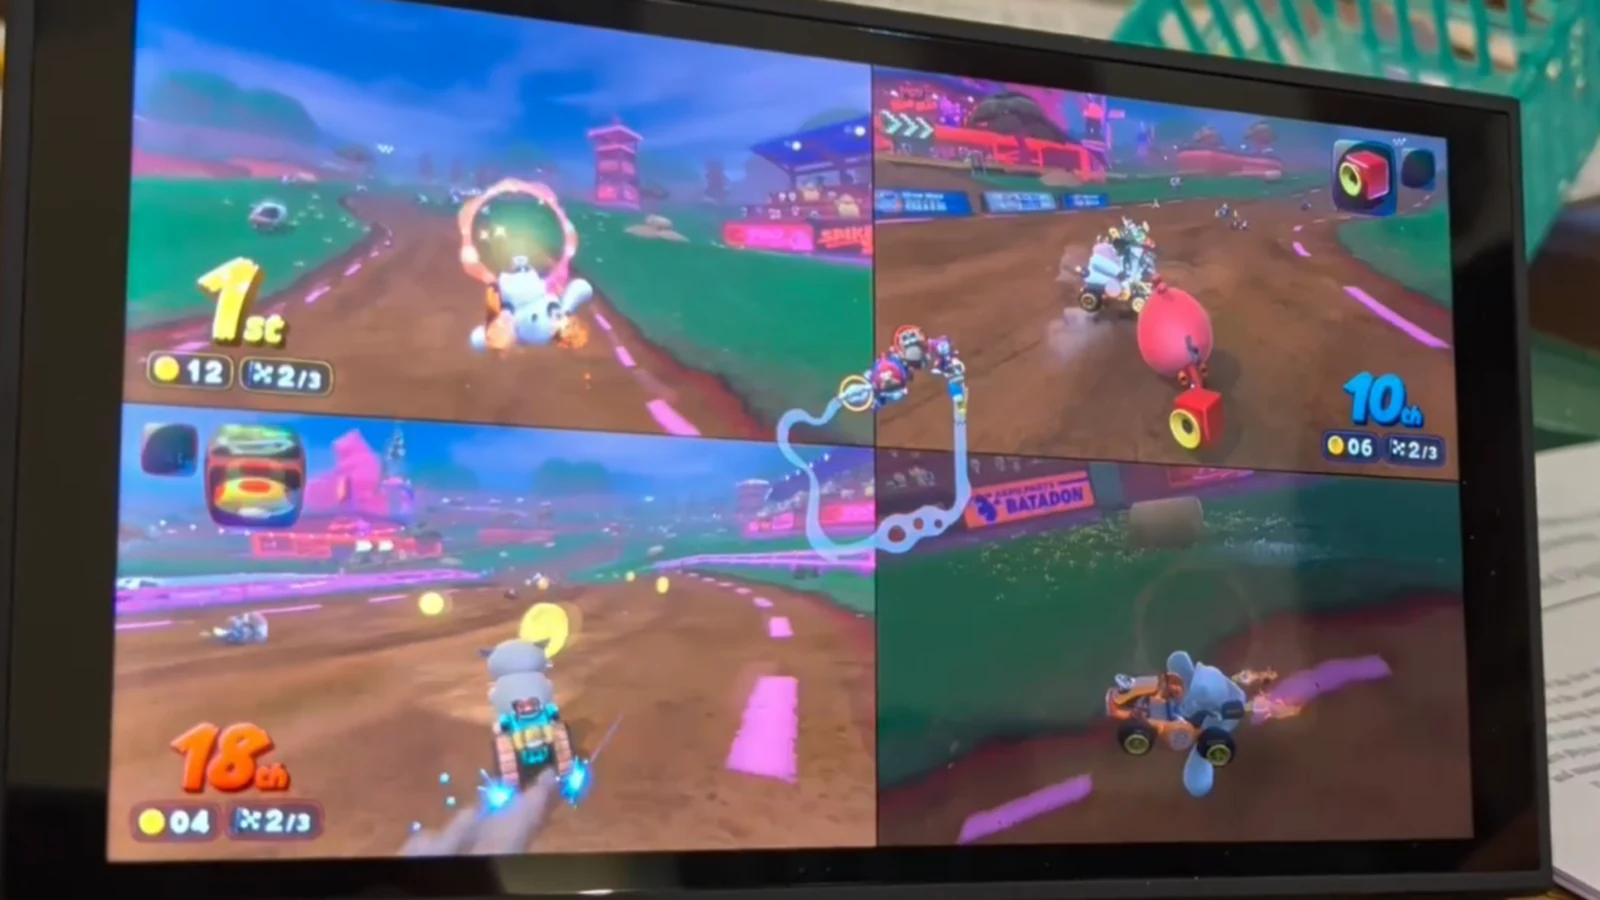
This allowed execution of privileged filesystem actions and native code execution via a faked filesystem process. Hajhamid, known online as Pepsipu, showed off a host of new modded characters in Mario Kart World as a proof of concept.
Other members of the community have demonstrated similar activities, highlighting simple demos and in-progress developer tools operating on exploited hardware.
Current Limitations and Community Response
Despite achieving userland access, the current exploit confines homebrew developers to a relatively restricted sandbox, falling short of kernel-level control over the hardware. Demonstrations showing the scope of the current access include a Full Vulkan GPU working in userland.
Additional community members have shared independent findings similarly highlighting early development progress on the console.
Nintendo Countermeasures and Outlook
Nintendo has already delisted SmileBasic 4 from the Switch eShop worldwide, though a Japanese demo version remains accessible. While this aims to slow the spread of the exploit, other hackers are already teasing alternative exploits utilizing other games.
While the current exploit operates on firmware version 23.0.1, future firmware updates are expected to patch the vulnerability. For readers seeking further updates on subscription platforms, information can be found via Learn more.
Sources
- Ars TechnicaSwitch 2 security takes a hit as hackers unlock homebrew access
Continue chronologically
Related entity coverage
Related stories
How to Fix Nintendo Switch 2 TV Connection Issues
Troubleshoot your Nintendo Switch 2 TV connection problems by checking your dock placement, power cables, HDMI settings, and system updates.
Valve Launches Steam Frame VR Headset Starting at $1,059
Valve has officially released its Steam Frame VR headset. Discover the latest tech news including new RPG titles and compact digital cameras.
Why microSD Express cards matter for the Nintendo Switch 2
Discover why the Nintendo Switch 2 requires a microSD Express card for expandable storage and how to choose the right capacity for your game library.
Is the Original Nintendo Switch Still Worth Buying in 2026?
Nine years after launch, is the original Nintendo Switch worth the investment? We break down the value of used versus new consoles in the age of Switch 2.