GitHub Introduces Confidential Comments on Security Advisories
GitHub has officially launched support for confidential comments on repository security advisories, providing maintainers a secure internal space for discussing reports without alerting reporters or external collaborators.
 Radwan AbdulhadiEditor and technology writer
New Internal Collaboration Capabilities for Security Maintainers
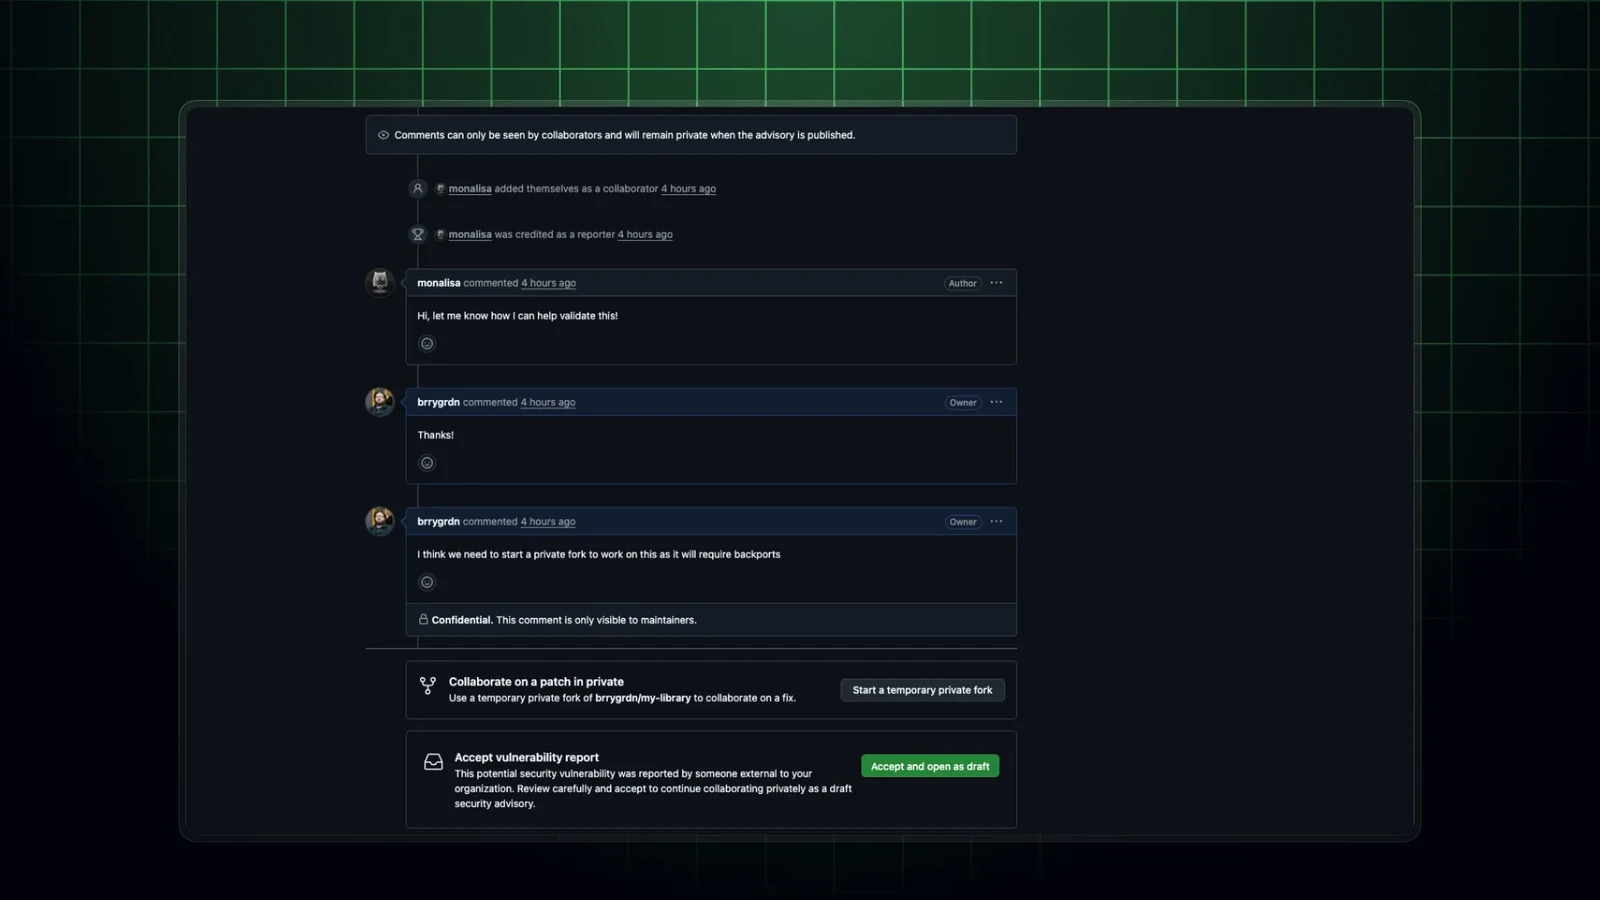
GitHub has announced an update to its platform that enables developers and maintainers to post confidential comments directly on repository security advisories. According to the [GitHub Changelog](https://github.blog/changelog/2026-10-02-confidential-comments-on-repository-security-advisories/), these confidential entries are visible exclusively to individuals who possess write access to the specific repository in question. This architectural design allows teams to deliberate, evaluate, and investigate reports internally without exposing sensitive dialogue to the original reporter or other invited external collaborators.
Prior to this deployment, every single comment published on a security advisory was automatically visible to all designated collaborators, including the external reporter who submitted the vulnerability finding. When repository teams needed to discuss potential abuse scenarios, deep investigation details, or sensitive coordination notes, they were forced to migrate their conversations to external communication channels. Consequently, critical historical context regarding the vulnerability assessment was permanently lost from the advisory’s official timeline.
Interface Design and Publishing Mechanics
The user interface for submitting internal notes has been streamlined to prevent accidental exposure. Maintainers can simply select the confidential option below the comment input box prior to publishing. Interface indicators explicitly confirm that only maintainers will be able to see the remark once submitted. Furthermore, confidential comments are clearly marked within the overarching advisory timeline so that authorized team members can easily distinguish between public-facing communications and internal technical evaluations.
GitHub has also established strict operational boundaries for these comments. Once a comment is posted, its confidentiality status cannot be toggled or altered between confidential and regular states. If a team member eventually loses their write access permissions for any reason, their capability to read past confidential comments is immediately revoked in accordance with current repository access rules. Organizations seeking comprehensive background information can [Learn more about repository security advisories](https://docs.github.com/code-security/concepts/vulnerability-reporting-and-management/repository-security-advisories) through official documentation channels.
Audit Trails and API Availability Specifications
Security and compliance teams require rigorous visibility into how internal data is accessed, and GitHub has integrated logging mechanisms to address this need. Any views of confidential comments are systematically recorded within the repository's audit log, ensuring complete traceability for organizational oversight. However, external integrations and automated scripts must account for specific API constraints, as confidential comments are fully accessible via the GraphQL API but are intentionally omitted from responses returned by the legacy REST API.
Because reporters and invited collaborators who lack write access are completely shielded from these hidden entries, they will not receive notifications regarding confidential updates. This ensures that delicate triage procedures, internal disagreements, and vendor coordination steps remain entirely contained within the core administrative group until the team is ready to communicate a unified resolution publicly.
Platform Availability and Account Tier Eligibility
The capability to post confidential comments is designed specifically to support public repositories that currently have private vulnerability reporting enabled. In terms of platform tier eligibility, the feature is accessible across GitHub Free, GitHub Pro, GitHub Team, and GitHub Enterprise Cloud accounts. By integrating this capability directly into the standard advisory workflow, GitHub aims to reduce friction in open-source and enterprise vulnerability management without requiring teams to juggle fragmented communication channels.
Sources
- GitHub ChangelogConfidential comments on repository security advisories
Continue chronologically
Related entity coverage
Related stories
GitHub Launches Security Advisory Comments API in Preview
GitHub has released the repository security advisory comments API in public preview, enabling users to read, add, and edit comments via REST API.
GitHub Releases Refreshed Repository Pull Requests Page
GitHub has officially launched its redesigned pull requests page, featuring improved search, advanced filtering, and enhanced management tools for developers.
GitHub Highlights Accessibility Statements on Repository Overview
GitHub now highlights ACCESSIBILITY.md files on repository overviews, making it easier for developers to discover and share accessibility project info.
GitHub Releases Actions Runner Controller 0.15.0
GitHub announces the release of Actions Runner Controller 0.15.0, featuring significant reliability, scalability, and observability improvements.