GitHub Launches Security Advisory Comments API in Preview
GitHub has announced the public preview of a new REST API that allows developers to read, add, and edit comments on repository security advisories, streamlining vulnerability triage and workflow automation.
 Radwan AbdulhadiEditor and technology writer
API Introduction and Capabilities
GitHub has officially launched the repository security advisory comments API in public preview, according to the [GitHub Changelog](https://github.blog/changelog/2026-10-02-repository-security-advisory-comments-api-in-public-preview/). Previously, discussions surrounding security advisories were restricted to the web user interface, despite frequently containing crucial triage context regarding vulnerability reports. With the introduction of these new endpoints, developers can now seamlessly interact with advisory discussions programmatically.
The new functionality empowers users to list comments on a repository security advisory with optional time-based filtering for updates. Furthermore, repository security advisory responses now incorporate a comment count, while global advisory responses display the count for their linked repository advisory. This addition allows teams to identify active discussions before fetching the actual content, facilitating better resource management during audits and reviews.
Streamlining Workflows and Audits
The ability to programmatically manage comments opens up several administrative and operational possibilities. Teams can export advisory discussions for thorough audits and migration processes, automatically incorporate triage notes into their tracking systems, and build custom advisory workflows that mirror existing processes for issues and pull requests.
For developers planning to integrate these new capabilities into their applications, comprehensive guidance and technical references are readily available through [our REST API docs](https://docs.github.com/rest/security-advisories/repository-advisories). These documents outline the exact endpoints and request structures required to interact with repository advisories effectively.
Access Controls and Security Scope
Access to the new advisory comments API follows strict security rules mirroring those of the advisory itself. Users must possess the repository security advisories scope, ensuring that anyone unauthorized to view a specific advisory remains unable to view its associated comments.
Additionally, utilizing the REST endpoints requires appropriate read or write repository security advisories permissions or token scopes. Non-collaborators are restricted from viewing internal comments, and confidential comments are intentionally excluded from being returned by these REST endpoints, maintaining the confidentiality of sensitive vulnerability reports.
Availability and Current Limitations
At the time of launch, the comment deletion feature is not yet supported through the API, meaning deletions must still be handled through alternative means if necessary. Additionally, related updates regarding [New fields for SecurityAdvisory GraphQL API](https://github.blog/changelog/2026-10-02-new-fields-for-securityadvisory-graphql-api) have also been introduced to the platform.
The repository security advisory comments API is currently accessible in public preview for public repositories across GitHub Free, GitHub Pro, GitHub Team, and GitHub Enterprise Cloud plans. Developers and platform administrators can return to the [Back to changelog](https://github.blog/changelog/) portal to stay updated on further ecosystem enhancements.
Sources
- GitHub ChangelogRepository security advisory comments API in public preview
Continue chronologically
Related entity coverage
Related stories
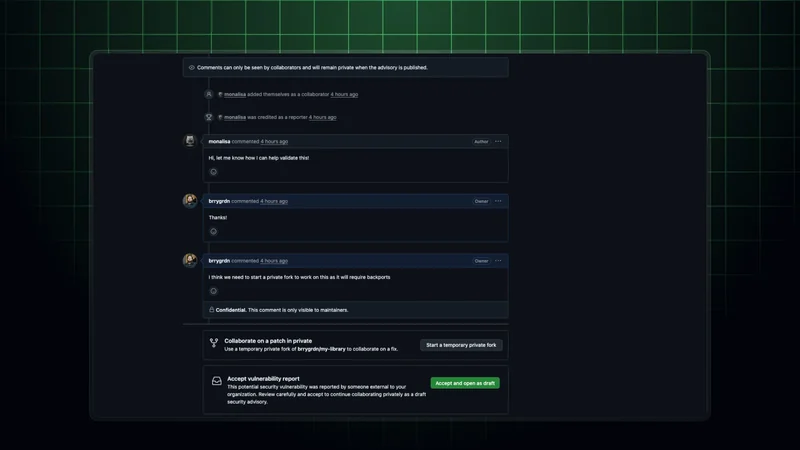
GitHub Introduces Confidential Comments on Security Advisories
GitHub now allows developers and maintainers to post confidential comments on repository security advisories for internal team discussions.
GitHub Launches Private Saved Views and Relates To API Support
GitHub introduces private saved views for repository issues and extends the 'Relates to' relationship across APIs, webhooks, and search for better issue management.
GitHub makes Actions workflow protections generally available
GitHub has moved Actions workflow execution protections to general availability, adding file-level policies, insights and REST API management.
GitHub Actions API and UI Updates Query Count Results
GitHub has introduced updates to query results in the GitHub Actions API and UI to improve performance and provide more accurate record counts.