NVIDIA Expands Confidential Computing to Scale AI Infrastructure
NVIDIA is broadening its Confidential Computing infrastructure layer to help frontier model builders securely scale workloads across cloud, neocloud, and enterprise environments.
 Radwan AbdulhadiEditor and technology writer
Expanding Confidential Computing for Frontier Models
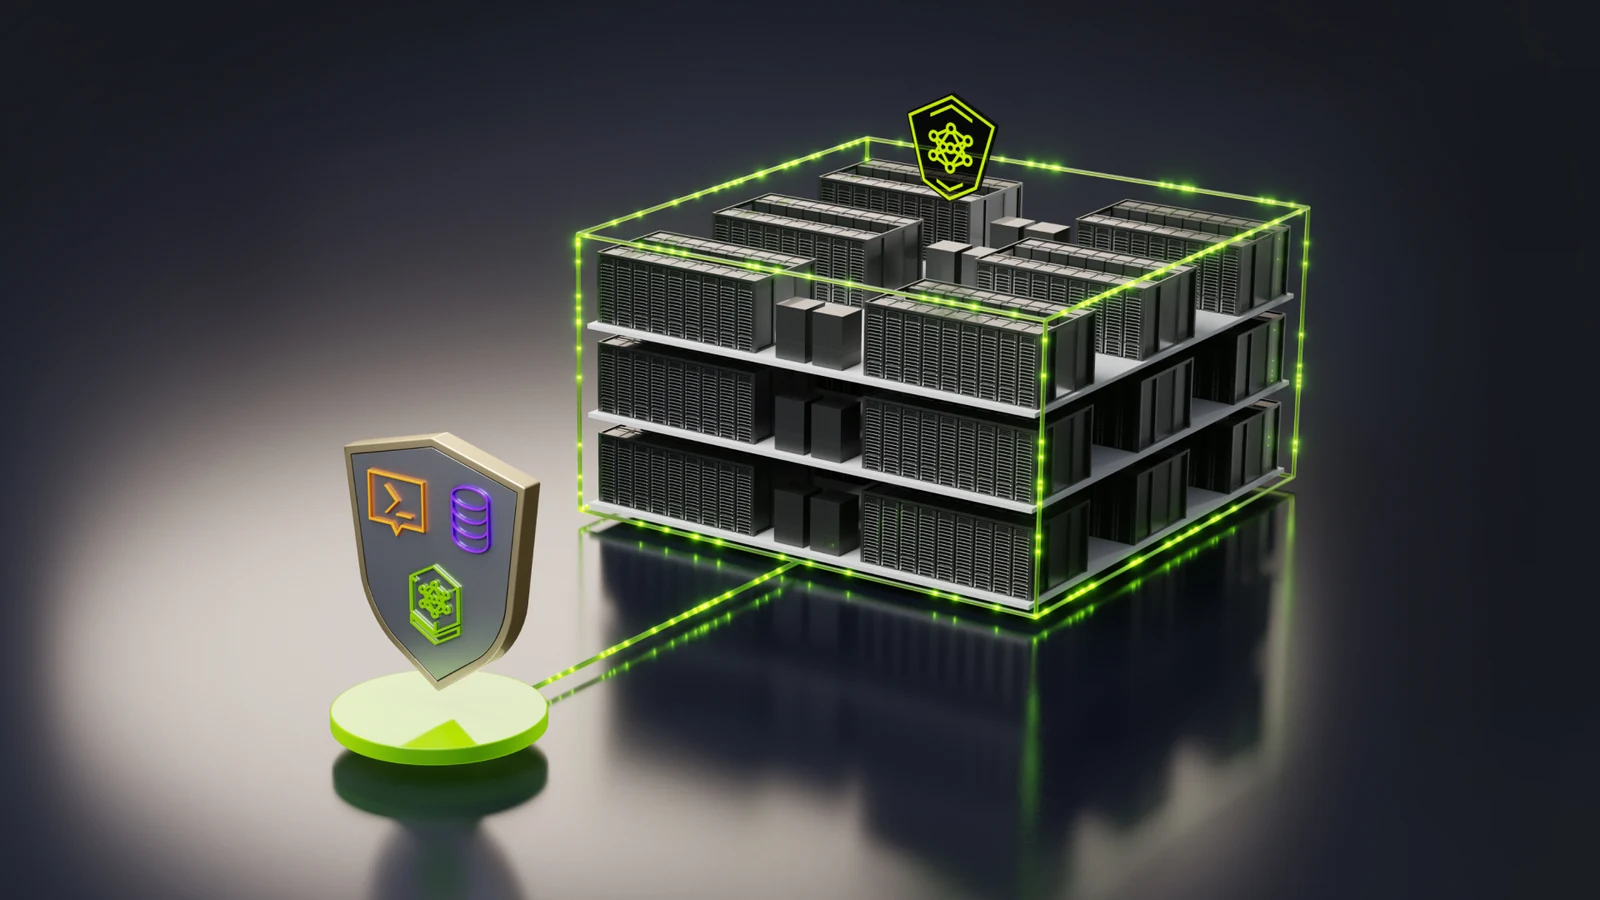
NVIDIA has announced a major expansion of its security portfolio with the introduction of Confidential Bare Metal, a new deployment option designed to protect sensitive workloads. As organizations increasingly build tools to enable safe agents across the stack, the underlying infrastructure must secure the models and data those agents rely on during execution. The NVIDIA OpenShell Reference Architecture, announced today, further contributes to this growing portfolio by helping organizations safely deploy agents at scale.
With NVIDIA Confidential Computing, frontier model builders can utilize dedicated third-party infrastructure while keeping full control of their valuable models and data. The newly introduced platform security controls protect data in transit, measure platform integrity, and enforce strict hardware-level access restrictions. These capabilities enable organizations to own and operate their bespoke software stack on accelerated infrastructure provided by third-party clouds and neoclouds.
Converged Security Architecture and Deployment Options
The updated NVIDIA Confidential Computing framework delivers a converged security architecture featuring three distinct deployment options. Organizations can match these options to their specific trust boundaries and operating requirements.
The three available deployment paths include Confidential Bare Metal for bare-metal infrastructure, Confidential Containers for Kubernetes environments, and Confidential Virtual Machines for virtualized setups. This flexibility allows supported providers to serve high-value workloads requiring robust model and data privacy protections, while giving model builders more geographic and operational choices globally.
Ecosystem Adoption by Cohere and Google Cloud
Leading industry players are already moving to integrate the expanded platform security features into their services. Cohere plans to incorporate Confidential Bare Metal into the Cohere Model Vault, utilizing trusted execution environments to extend hardware-rooted security straight to the GPU.
Phil Blunsom, chief technology officer at Cohere, stated that enterprises trust the company to provide a secure and confidential platform for inference. By using these tools, Cohere protects customer data in memory and across interconnects during execution.
Meanwhile, Google Cloud is extending support for Confidential Bare Metal to A4X Max instances powered by NVIDIA GB300 NVL72 systems. Andrés Lagar-Cavilla, distinguished engineer and AI infrastructure security lead at Google Cloud, noted that the instances combine non-virtualized accelerated compute with end-to-end cryptographic protection to preserve data privacy and protect model intellectual property.
Broadening Platform Support Across Hardware and Partners
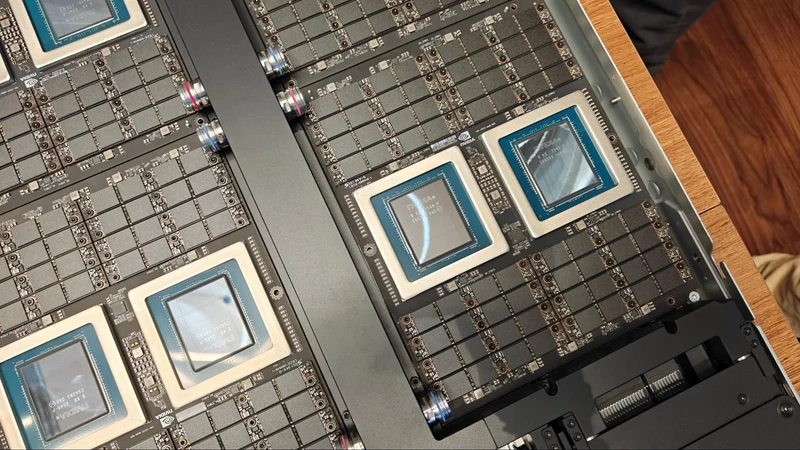
Hardware-rooted isolation and cryptographic attestation are now extending deeper into the company's product lineup. Support now covers NVIDIA Grace Blackwell NVL72 rack-scale systems, as well as x86-based NVIDIA HGX Rubin NVL8 and NVIDIA DGX Rubin NVL8 architectures.
A broad group of cloud and infrastructure providers support these deployments, including CoreWeave, Firmus, GMI Cloud, Google Cloud, IREN, Lambda, Microsoft Azure Infrastructure, Nebius, Nscale, and Vultr. Furthermore, global systems partners such as Cisco, Dell Technologies, HPE, Lenovo, Supermicro, and Bull will back these security features through NVIDIA-Certified Systems.
Sources
- NVIDIA BlogNVIDIA Confidential Computing Expands, Enabling Frontier Model Builders to Securely Scale Across Global Infrastructure
Continue chronologically
Related entity coverage
Related stories
Google Cloud and NVIDIA Announce Vera Rubin Infrastructure
Google Cloud and NVIDIA announce general availability of NVIDIA Vera Rubin infrastructure, bringing advanced agentic AI and reinforcement learning platforms.
NVIDIA and CoreWeave Launch Vera Rubin for Agentic AI
NVIDIA and CoreWeave announce the production availability of NVIDIA Vera Rubin systems, accelerating agentic AI workflows and token throughput.
Nvidia Vera CPUs Land in Oracle Cloud
Nvidia's standalone Vera CPUs arrive in Oracle Cloud Infrastructure Superclusters as part of a multi-gigawatt deployment.
Nvidia Vera CPU Benchmarked Against AMD and Intel
Nvidia's Vera data center CPU is benchmarked against AMD EPYC Turin and Intel Granite Rapids-AP, showcasing strong Python performance and bandwidth.