Tamnoon Builds AI Cloud Remediation With Amazon Bedrock
Tamnoon has detailed how it developed Tami, an AI-powered agentic cloud remediation orchestrator built on Amazon Bedrock to autonomously investigate and address security findings.
 Radwan AbdulhadiEditor and technology writer
Tackling Cloud Security Backlogs
Cloud-native application protection platforms, cloud providers, and posture scanners routinely generate more security findings than security teams can manually triage. This volume leaves critical exposures sitting unresolved while risk accumulates. According to Tamnoon, most findings remain untouched not because they are difficult to fix, but because investigating context, identifying resource owners, and confirming that a fix will not disrupt production consumes extensive senior engineering time.
To close the gap between detected vulnerabilities and actual fixes, the company developed Tami, an agentic cloud remediation orchestrator. Operating on Amazon Bedrock, the AI-powered assistant autonomously investigates security findings ingested from CNAPP and other cloud-native sources, assesses whether remediation is safe, and orchestrates fixes under strict guardrails.
The Agentic Remediation Pipeline
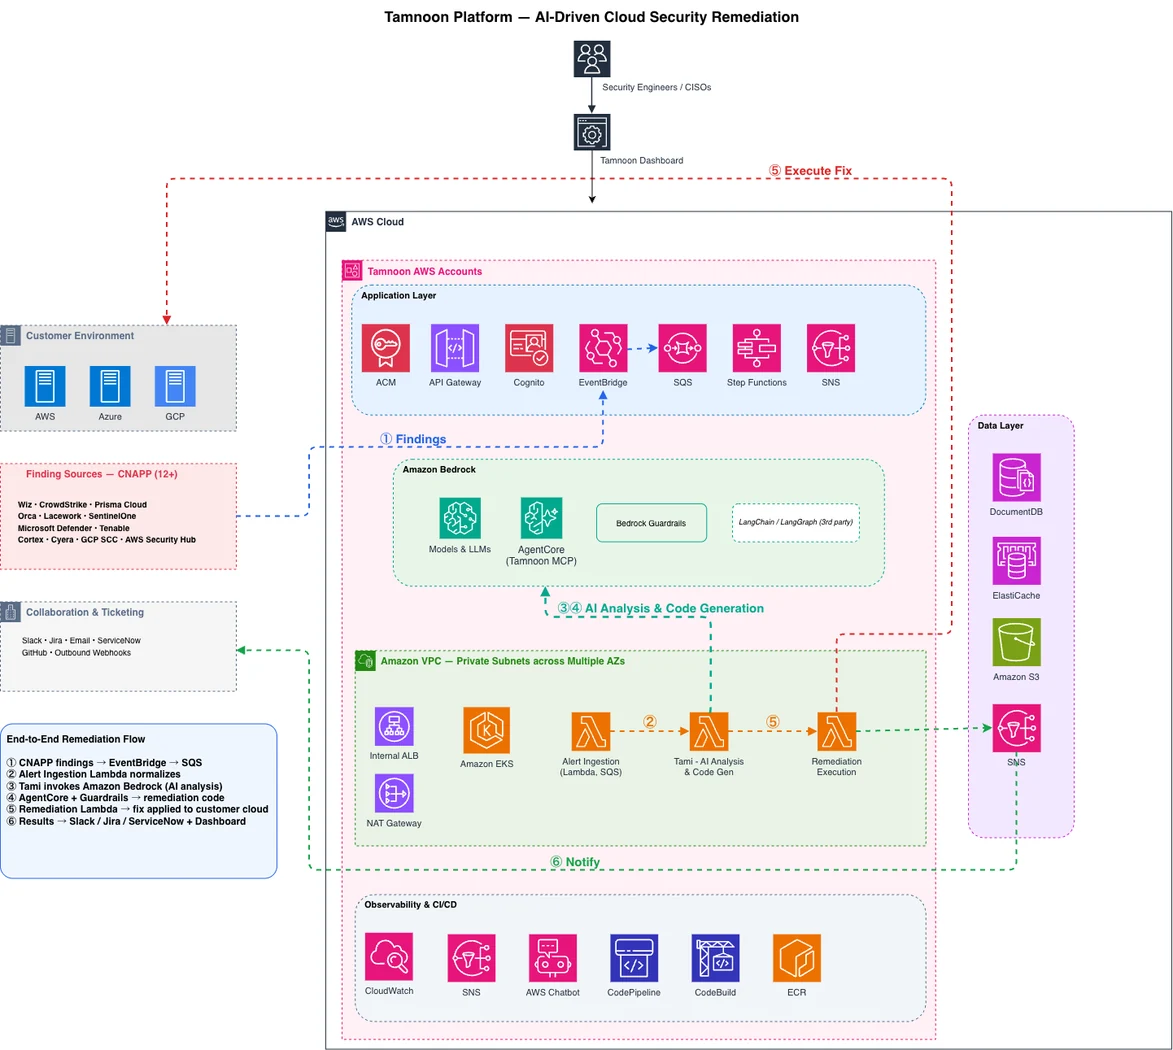
Tamnoon integrates directly with existing CNAPPs and security tools to normalize findings into a unified schema. Once ingested, the platform delegates work across four specialized AI agents operating within an event-driven, serverless architecture on AWS. Each agent is responsible for a distinct phase of the pipeline, ensuring tasks scale independently.
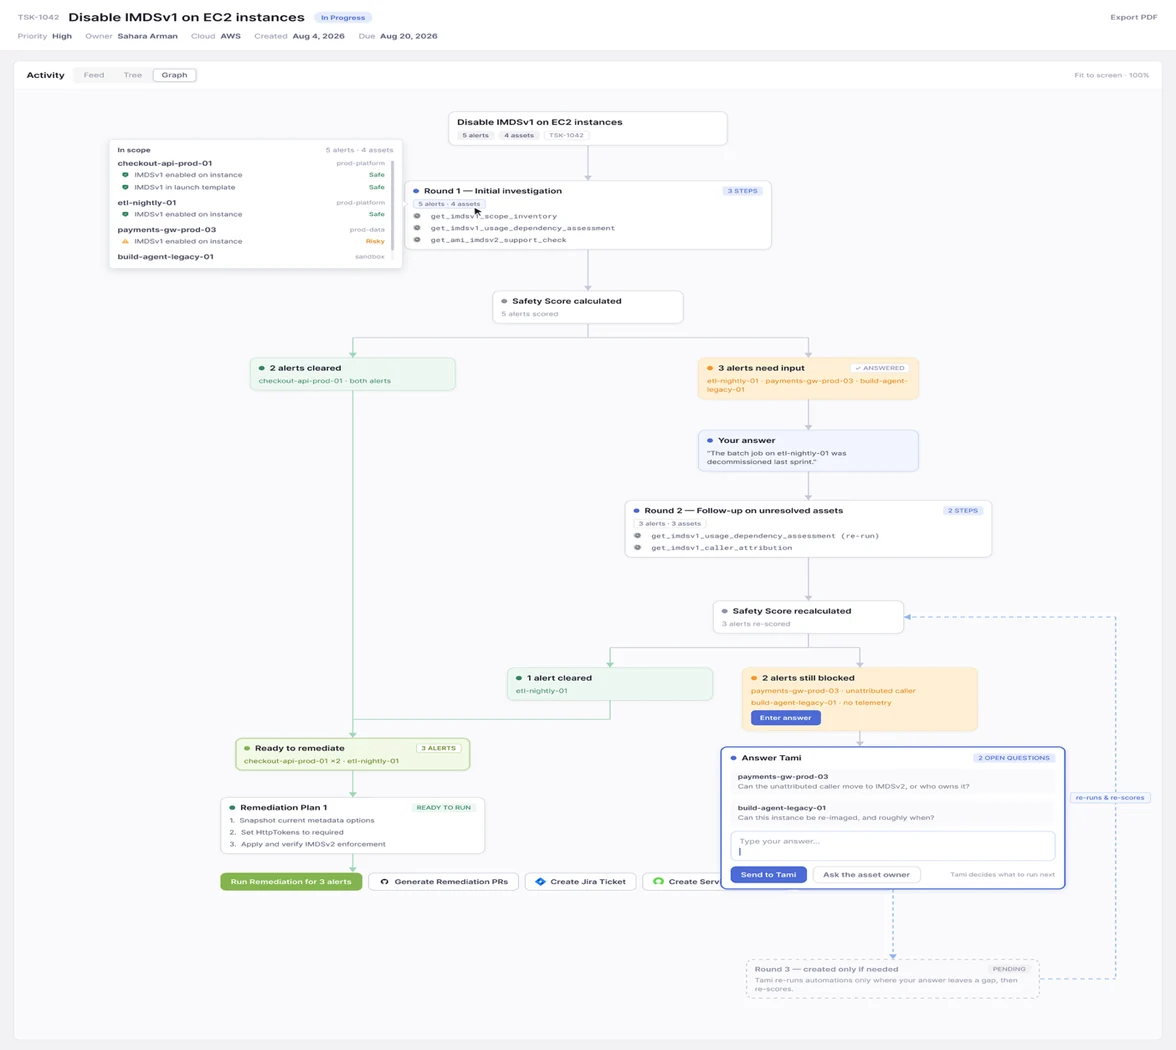
The pipeline begins with an investigation agent that utilizes context, filters through a large language model validation layer, and produces investigation plans. Next, a safety-scoring agent evaluates each asset with a conservative bias, classifying findings as safe, risky, or awaiting data. Once cleared, a remediation agent sequences dependencies and structures backup and verification steps before a code-generation agent passes artifacts through an automated review loop.
Leveraging Amazon Bedrock Capabilities
Choosing the right foundation model platform was crucial for supporting Tamnoon’s varied agent requirements. Different agents require distinct capabilities, ranging from deep investigative reasoning to high-volume validation and cost-optimized code review. Utilizing Amazon Bedrock allowed the team to invoke the most suitable model for each specific task through a single API integration.
Additionally, the platform's cross-region inference capability automatically routes requests to optimal AWS regions within defined geographic boundaries, eliminating the need for custom traffic distribution logic. Security considerations were equally vital, as inference runs directly within Tamnoon’s own AWS environment under scoped IAM permissions.
Impact and Integration Ecosystem
By automating the end-to-end workflow from finding ingestion to validated execution, the platform aims to eliminate the hesitation that typically blocks security automation. Tamnoon connects downstream from popular security tools and posture solutions, functioning alongside existing detection systems to turn raw alerts into production-safe fixes.
According to the company's deployment metrics and reported outcomes, this automated approach drove a significant reduction in critical risk indicators across customer environments. Specifically, the framework drove an over 90 percent reduction in critical cloud exposure in 90 days with zero reported production issues.
Sources
- AWS Machine Learning BlogHow Tamnoon built AI-powered cloud security remediation with Amazon Bedrock
Continue chronologically
Related entity coverage
Related stories
Orca Security Builds Discovery AI on Amazon Bedrock
Orca Security deployed Discovery AI using Amazon Bedrock to convert natural language into Sonar queries, lowering costs and latency.
Circle K Cuts DevOps Incident Triage Times With Amazon Bedrock
Circle K's DevOps team accelerated incident triage from up to 60 minutes down to under 15 minutes by implementing an agentic AI system on Amazon Bedrock.
Managing Amazon Bedrock Costs: A FinOps Playbook
Explore an end-to-end operational model for FinOps and platform teams to manage, attribute, and optimize Amazon Bedrock generative AI costs.
OpenAI GPT Models Arrive on Amazon Bedrock in Canada
Canadian organizations can now access OpenAI GPT models on Amazon Bedrock from Canada (Central) and Canada West (Calgary) using cross-Region inference.