Eon Cuts Engineer Onboarding to Minutes with Amazon Bedrock AgentCore Gateway
Eon has deployed Amazon Bedrock AgentCore Gateway to consolidate multi-cloud investigation tooling, reducing new-engineer onboarding from two days to two minutes while enforcing Cedar-based authorization for both human and autonomous agents.
 Radwan AbdulhadiEditor and technology writer
Centralizing Multi-Cloud Investigation Access
Independent software vendor Eon has replaced a fragmented landscape of per-tool credentials and locally run Model Context Protocol servers with a single authenticated Amazon Bedrock AgentCore Gateway, giving more than 100 developers and autonomous agents unified access to investigation tooling spanning AWS, Google Cloud Platform, and Microsoft Azure. The company says the change cut new-engineer onboarding from roughly two days to about two minutes.
Why Eon Needed a Unified Gateway
Eon provides an Autonomous Data Foundation that discovers and classifies cloud resources across the three major clouds, offers continuous deduplicated backup, detects ransomware, and supplies live grounded context for AI agents — all from a single read-only AWS IAM role. Its internal engineering team routinely investigates production incidents that require correlating Kubernetes pod logs, Grafana metrics, GitHub pull requests, and cloud-provider health status in a single session. As the toolset grew, each new integration added another credential to configure, secure, and rotate, while developers ran multiple local MCP servers that were difficult to standardize and keep current.
The company evaluated two options: building a custom reverse proxy with its own authentication, session management, and protocol translation layer, or adopting Amazon Bedrock AgentCore Gateway, a managed gateway with built-in identity federation, Cedar-based authorization policies, and Runtime hosting that converts local stdio-based MCP servers into Streamable HTTP endpoints. Eon chose the managed gateway because it delivered identity separation, cross-account connectivity, and policy enforcement as managed capabilities rather than custom code to maintain.
Architecture: One Gateway, Distributed Runtimes
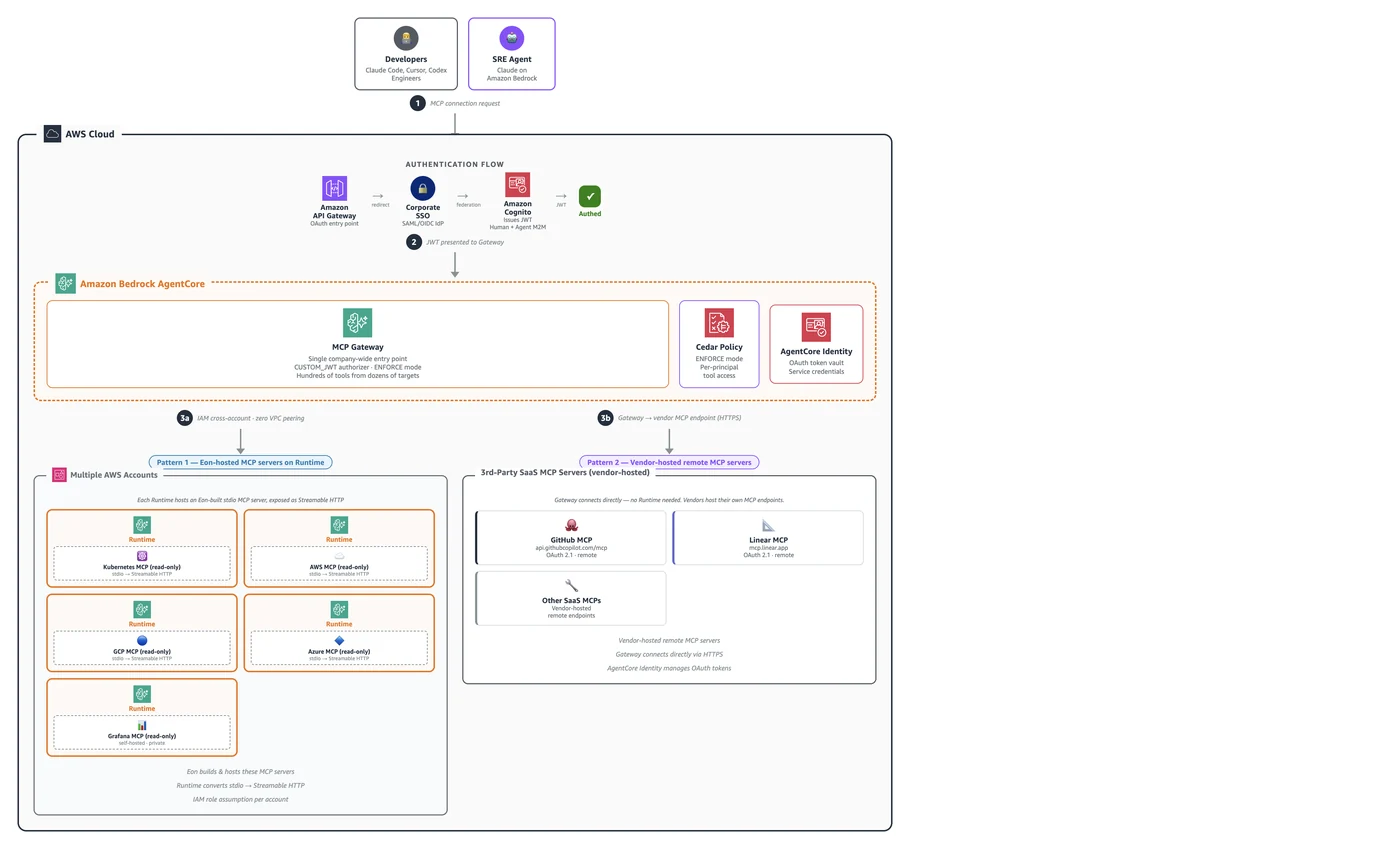
Eon deployed the full Amazon Bedrock AgentCore stack — AgentCore Gateway, Policy, Runtime, and Identity. A single MCP Gateway serves as the company-wide front door. Corporate single sign-on federates through Amazon Cognito, which mints JSON Web Tokens for human users; Amazon API Gateway sits in front as the OAuth entry point, proxying the MCP session. Autonomous agents, including an SRE agent running Claude on Amazon Bedrock, authenticate with Cognito client_credentials grants directly against the gateway.
Dozens of target MCP servers exposing hundreds of tools are hosted on AgentCore Runtimes distributed across multiple AWS accounts. Each Runtime converts local stdio-based MCP servers into Streamable HTTP endpoints accessible through the gateway. Developers using Claude Code, Cursor, or OpenAI Codex configure one MCP URL, authenticate through corporate SSO, and receive a single aggregated tools/list response — no local setup and no per-tool tokens.
Cedar Policies Enforce Read-Write Boundaries
The core security decision was enforcing read and write boundaries through Cedar policy at the gateway level. Cedar policies in ENFORCE mode control which principals can invoke which tools. Read operations are available to selected groups mapped to job roles; write operations are limited to low-impact collaboration actions such as commenting on a pull request or ticket, while production tools remain read-only. The gateway evaluates every tools/call request against Cedar before forwarding to the target.
Cedar policies are managed as code through GitHub pull requests with review comments, providing version control and an audit trail on every permission change. Humans in approved groups get read access; write operations require explicit Cedar permits granted only to specific agent identities. The gateway accepts both JWT tokens for humans and client_credentials tokens for agents, with Cedar determining what each principal can do.
Measurable Impact on Onboarding and Operations
Before the gateway, new engineers spent roughly two days configuring credentials and local MCP servers before they could investigate their first incident. Now they open their IDE, configure one MCP URL, authenticate through corporate SSO, and immediately gain access to hundreds of tools across all three clouds. Eon says the centralized approach also eliminates the operational overhead of VPC peering or AWS PrivateLink per account that was previously required to host MCP servers across multiple AWS accounts.
Sources
- AWS Machine Learning BlogHow Eon built multi-cloud investigation with an MCP Gateway on Amazon Bedrock AgentCore
Continue chronologically
Related entity coverage
Related stories
Bayer Builds Agentic Decision Engine on Amazon Bedrock AgentCore
Bayer Crop Science has developed the Agentic Decision Engine using Amazon Bedrock AgentCore and AWS Unified Operations to streamline plant breeding analytics.
Building Trust in AI Agents With Amazon Bedrock AgentCore
Discover a nine-stage production evaluation framework built on Amazon Bedrock AgentCore to catch silent AI agent regressions.
NarrateAI Brings LLM Quality Assurance to Amazon Bedrock
NarrateAI implements five advanced quality assurance techniques on Amazon Bedrock to achieve 99% numerical accuracy with real-time streaming.
MRH Trowe Gives 400 Employees Secure Self-Service AI Agents
MRH Trowe gave 400 employees secure self-service AI agent access in its first production month, using Strands Agents, Amazon Bedrock AgentCore, and LibreChat.