Google Halts Open-Source Bug Bounty Program Amid AI Spam Surge
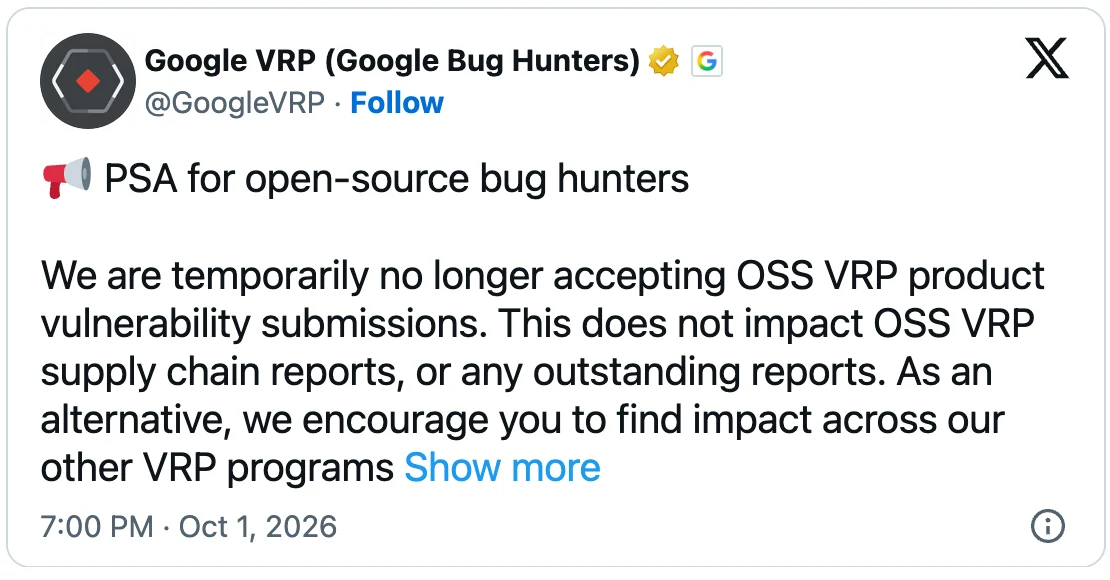
Google has temporarily suspended product vulnerability submissions to its Open Source Software Vulnerability Rewards Program due to a massive wave of automated, invalid AI-generated reports.
 Radwan AbdulhadiEditor and technology writer
Suspension of OSS VRP Submissions
Google has officially suspended submissions to its Open Source Software Vulnerability Rewards Program (OSS VRP) after experiencing a massive influx of AI-generated reports. The company originally launched the OSS VRP in August 2022 to incentivize security researchers to responsibly disclose security flaws across various open-source projects maintained by Google, including Golang, Angular, Bazel, Protocol Buffers, Fuchsia, and critical third-party dependencies.
In an official statement regarding the suspension, Google explained the root cause behind the temporary halt. The company noted that the pause is a direct result of a notable increase in automated submissions, the vast majority of which lack validity. Despite pausing product vulnerability submissions, Google clarified that supply chain reports and any outstanding submissions remain unaffected by this operational change.
Alternative Submission Channels and Future Plans
While the main product vulnerability stream for the OSS VRP is paused, security researchers still have alternative pathways to report security issues to Google. Investigators can submit security patches for open-source software via the Google Patch Rewards Program, which provides bounties of up to $15,000 for high-impact fixes. Additionally, vulnerabilities in Google Cloud open-source repositories that impact Cloud products can still be reported through the company's Cloud VRP.
Google has committed to reformatting and addressing the automated submission issues plaguing the program. The tech giant stated that it will provide further information on program changes in the first quarter of 2027. Furthermore, the company clarified that these updates and restrictions do not impact valid product vulnerabilities that were submitted prior to October 1, 2026.
Broader Context of Google Vulnerability Rewards
Since it initiated its very first vulnerability rewards program in 2010, Google has distributed more than $81.6 million to thousands of security researchers around the globe. The scale of these programs expanded dramatically over the years; notably, the company awarded a record-breaking $17.1 million to over 700 security researchers, marking a 40% increase compared to the total awarded in the previous year.
Industry-Wide Impact of AI-Generated Bug Spam
Google is far from the only organization forced to reckon with an onslaught of poor-quality, automated vulnerability reports fueled by modern artificial intelligence tools. Earlier in the year, the primary maintainer of the curl command-line utility and library completely ended the project's HackerOne security bug bounty program after being overwhelmed by an unmanageable stream of AI slop vulnerability reports.
Similarly, Intel removed all financial rewards for security flaws reported across its software, firmware, hardware, and services on its Intigriti bug bounty program. Meanwhile, software giants like Microsoft have publicly noted that the rising adoption of AI tools is significantly accelerating vulnerability discovery across the industry, raising operational demands and leading to massive patch cycles such as the record-breaking September update.
Sources
- BleepingComputerGoogle halts open-source bug bounty program amid AI spam surge
Continue chronologically
Related entity coverage
Related stories
Google Freezes Open-Source Bug Bounty Amid AI Slop
Google suspends product vulnerability submissions for its OSS VRP bug bounty program until 2027 following an influx of invalid AI reports.
Google Narrows Open Source Bug Bounty Amid Invalid Reports
Google temporarily halts product vulnerability reports for its Open Source Software Vulnerability Reward Program due to invalid automated submissions.
Google Admits Intel Googlebooks Face Android App Issues
Google acknowledges that Intel-based Googlebooks may encounter performance issues with a small handful of Android apps upon launch.
Intel Googlebooks May Struggle With Some Android Apps
Google reveals that certain Android apps may face performance issues on Intel-based Googlebooks due to their original design for Arm chips.