Google Freezes Open-Source Bug Bounty Amid AI Slop
Google has officially halted product vulnerability submissions to its Open Source Software Vulnerability Reward Program after maintainers were overwhelmed by thousands of invalid, AI-generated reports.
 Radwan AbdulhadiEditor and technology writer
Google Suspends OSS VRP Submissions
Google has officially suspended product vulnerability submissions to its Open Source Software Vulnerability Reward Program, commonly known as the OSS VRP bug bounty program, due to a massive influx of invalid AI-driven reports. According to reporting from [Tom's Hardware](https://www.tomshardware.com/tech-industry/artificial-intelligence/google-suspends-part-of-the-oss-vrp-bug-bounty-program-due-to-an-influx-of-invalid-ai-submissions-product-vulnerability-submissions-ended-october-1), the company announced the decision through an official X post on October 1.
The suspension went into effect immediately on October 1 and does not impact product vulnerabilities that were submitted prior to that date. Google has encouraged participants to explore other VRP programs while it works on reformatting and restructuring this aspect of the initiative. The tech giant has committed to providing an update on the program by the first quarter of 2027.
Scope of the Suspension and Exceptions
While product vulnerability submissions focused on public code repositories are halted, certain parts of Google's security bounty framework remain operational. The current suspension does not impact OSS VRP supply chain reports. Furthermore, Google stated that it may still accept reports covering product vulnerabilities through the Cloud VRP for select repositories impacting Google Cloud products.
The OSS VRP is a specialized security bounty initiative designed to incentivize independent researchers to discover and responsibly disclose security flaws across Google's broader open-source ecosystem. Product vulnerability submissions typically target code defects, logic flaws, or design bugs within public repositories—tasks that historically required significant manual effort and deep technical skill.
The Impact of AI Hallucinations on Maintainers
The rise of large language models and automated AI bug-hunting scripts has drastically reduced the barrier to entry, enabling automated generation of bug reports. Unfortunately, this technological shift resulted in an overwhelming influx of low-effort submissions.
Google engineers and open-source maintainers found themselves flooded with thousands of poorly written reports claiming to identify bugs that were, in reality, completely invalid or unexploitable hallucinations. Instead of fixing critical vulnerabilities, maintainers were spending an unsustainable amount of time manually sorting through and validating faulty code submissions, forcing the temporary freeze.
A Broader Industry Trend
Google is not alone in facing challenges related to automated AI submissions. Similar scenarios have played out across the broader technology industry. For instance, Linux maintainers reported being entirely overwhelmed by CVE finds after AI-powered bug hunters pushed the Linux kernel to record numbers of reported vulnerabilities per release. Consequently, Linux previously ended support for older network drivers due to an influx of false AI-generated bug reports.
Additionally, Intel suspended its own bug bounty program—which previously offered up to $100,000 per flaw—though the company did not explicitly cite AI-generated reports as the direct cause for that specific decision. Nevertheless, industry experts widely suspect that automated submissions and AI slop are driving a reassessment of bug bounty frameworks industry-wide.
Sources
- Tom's HardwareGoogle freezes open-source bug bounty program amid flood of invalid AI slop submissions
Continue chronologically
Related entity coverage
Related stories
Google Unveils New Googlebook Laptop Lineup
Google launches a new series of premium laptops featuring a hybrid OS, deep Android integration, and advanced Gemini AI capabilities to rival Mac hardware.
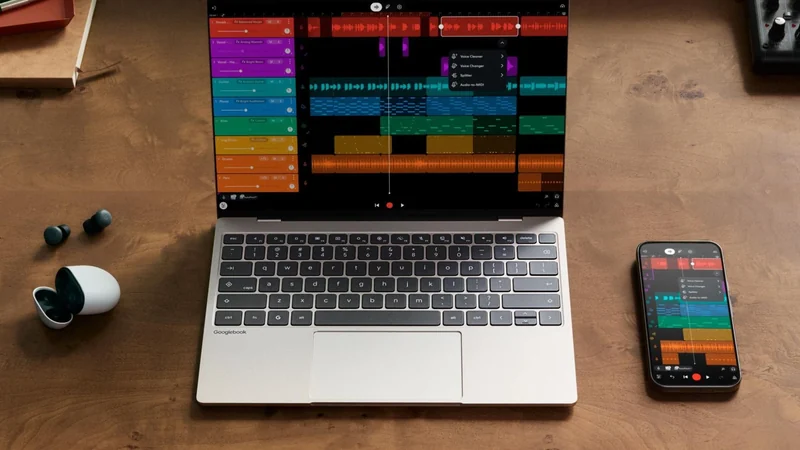
Google Launches Android-Powered Googlebook Laptop Lineup
Google is introducing its new line of Android-based Googlebook laptops on October 4th, featuring deep mobile integration and Gemini AI capabilities.
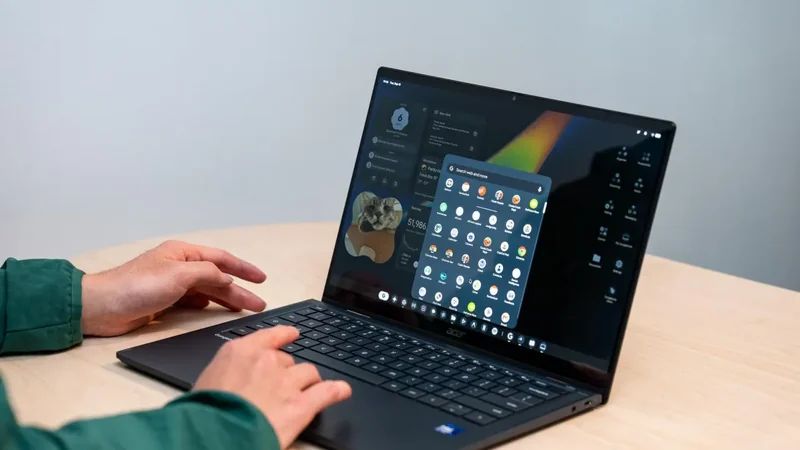
Google Launches Googlebook Laptops for Android Users
Google has officially unveiled Googlebooks, a new line of laptops designed to provide seamless connectivity and synergy with your Android smartphone.
How to Turn Your Old Windows PC Into a Chromebook for Free
Don't discard your aging hardware. Learn how to repurpose your old Windows or Mac computer by installing ChromeOS Flex for a lightweight and secure experience.