Cloudflare Launches Post-Quantum GeoKey Manager in Beta
Cloudflare has launched a closed beta for its post-quantum geographically restricted key manager, a major step forward for its Data Localization Suite and data sovereignty solutions.
 Radwan AbdulhadiEditor and technology writer
Introduction to Post-Quantum GeoKey Manager
Cloudflare is launching a post-quantum geographically restricted key manager in support of its Data Localization Suite in closed beta. This new solution is designed to protect geographically fenced decryption keys from harvest now, decrypt later attacks while helping organizations meet strict data sovereignty requirements.
While general availability is officially planned for the first quarter of 2027, today's launch marks a critical milestone in migrating Cloudflare products to post-quantum standards. The system ensures that a customer's decryption keys remain accessible only within their chosen geography.
The Threat of Harvest Now, Decrypt Later Attacks
Governments, financial institutions, healthcare providers, and defense organizations routinely process sensitive data that can remain confidential for years or decades. When standard public-key encryption is deployed, malicious actors do not necessarily need a quantum computer immediately to compromise security.
Instead, adversaries can store intercepted ciphertexts until future quantum computers become powerful enough to break the underlying classical cryptography. For organizations operating under strict geographic regulations, defending against this strategy requires end-to-end encryption guarantees that ensure only servers within a designated region can access plaintext data.
Evolution of Geo-Restricted Key Management
Cloudflare initially pioneered geo-restricted transport layer security keys back in 2017 to give customers granular control over where private keys could be unwrapped on the anycast network. This architecture provided technical guarantees regarding the specific region where customer requests were decrypted.
The platform subsequently evolved in 2022 to support ciphertext policy attribute based encryption, which expressed geographic requirements using specific regional attributes rather than tying encrypted keys to a fixed set of physical data centers.
Hybrid Cryptographic Protection and Key Hierarchy
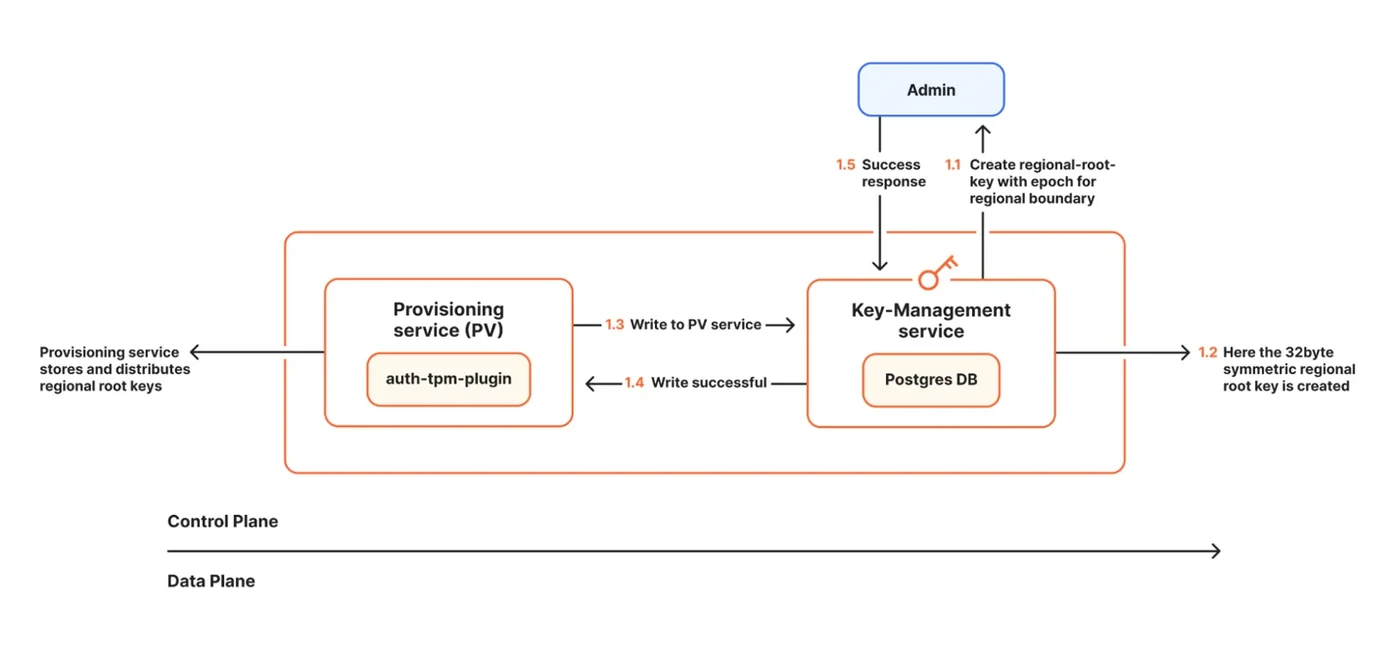
Because production-ready post-quantum attribute-based encryption schemes are not currently available and customers typically rely on a manageable number of regions, Cloudflare adopted a simpler, highly maintainable design utilizing hybrid cryptographic protection.
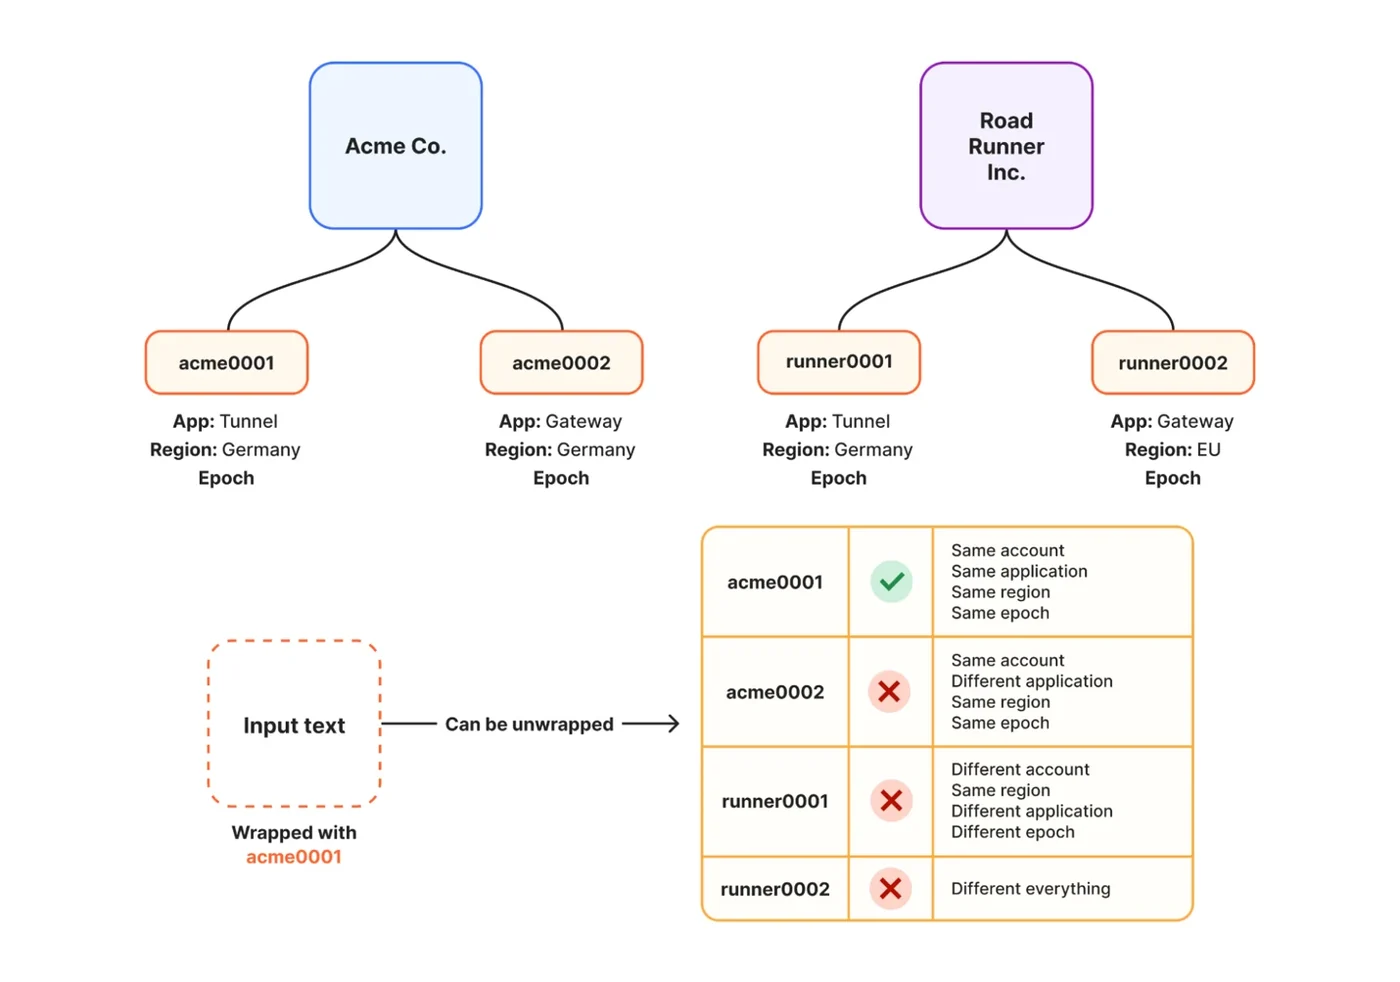
The platform combines ML-KEM-768 and X25519 protection across two distinct layers. A regional root key functions as a symmetric secret tied strictly to one region, while application-specific key pairs are derived for individual services such as Gateway or Tunnel.
Initialization and Regional Isolation Guarantees
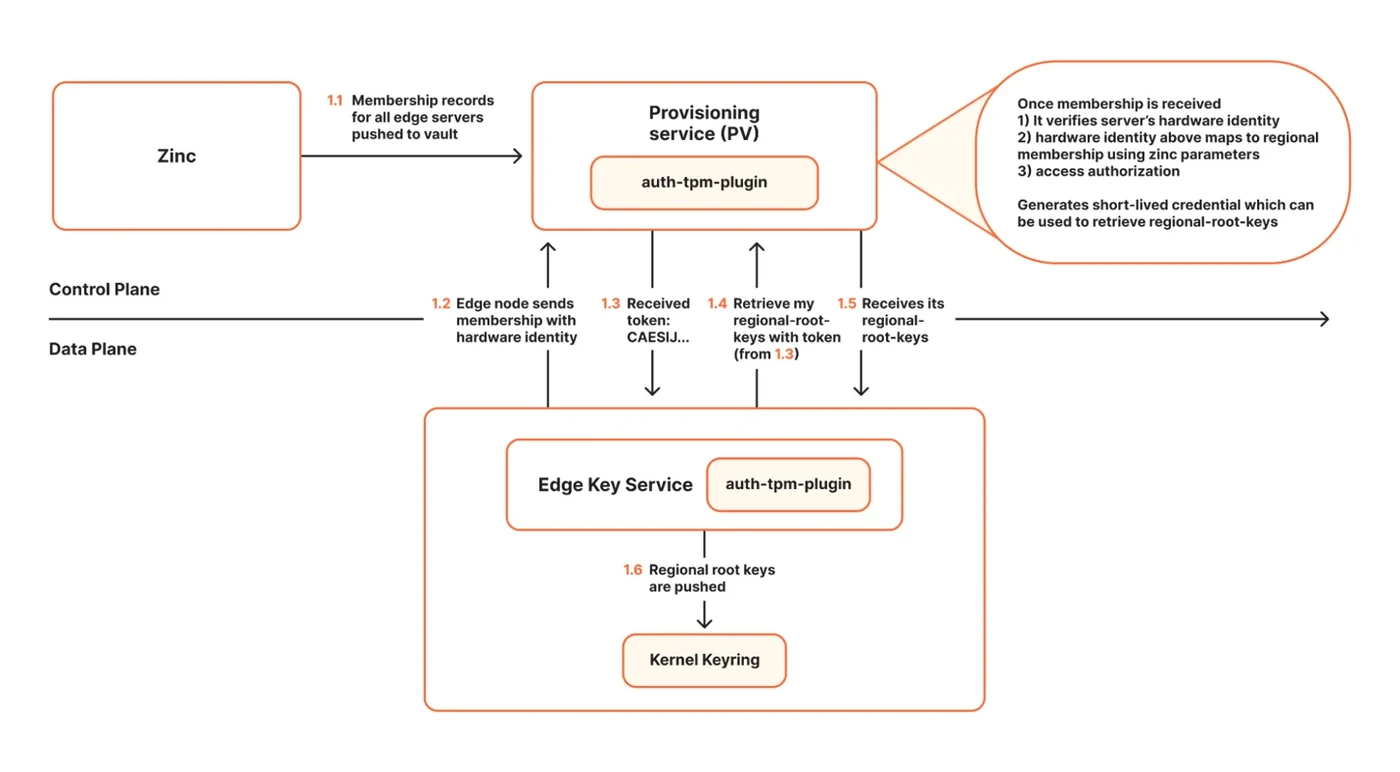
During system startup, the edge key service on each Cloudflare server verifies that it has successfully loaded all required regional root keys. If any configured key is missing or malformed, the service intentionally refuses to start to preserve security boundaries.
Following initialization, individual requests fail closed if metadata identifies a regional root key that is not available locally. This operational model ensures that regional root keys never leave their intended geographic boundaries.
Sources
- Cloudflare BlogBringing post-quantum cryptography to geographically fenced key management
Continue chronologically
Related entity coverage
Related stories
Cloudflare Builds AI Tool to Drive Post-Quantum Migration
Cloudflare is developing an internal AI-powered tool called CryptoLabe to discover cryptography across its codebase and track post-quantum readiness.
Cloudflare and IETF Fight Quantum IPsec Downgrade Threats
Cloudflare and the IETF have developed a new transcript authentication extension to protect post-quantum IPsec tunnels from downgrade attacks.
Cloudflare Builds Post-Quantum CA Supporting Merkle Tree Certificates
Cloudflare is launching a new certificate authority supporting Merkle Tree Certificates to address post-quantum scaling challenges and transparency needs.
Cloudflare Announces Intent to Become a Public Certificate Authority
Cloudflare is applying to become a public certificate authority, combining an established root, an ACME-first approach, and Merkle Tree Certificates.