
Cloudflare Builds Post-Quantum CA Supporting Merkle Tree Certificates
Cloudflare has announced plans to build a new certificate authority that will support Merkle Tree Certificates at scale, paving the way for efficient post-quantum cryptography on the web.
 Radwan AbdulhadiEditor and technology writer
The Post-Quantum Scaling Challenge for the Web PKI
The Web Public Key Infrastructure ecosystem, which ensures users connect to the correct websites, faces an imminent challenge from the arrival of quantum computers. This threat has prompted the industry to upgrade systems to post-quantum cryptography by 2029.
Simply swapping post-quantum cryptography into certificates at Internet scale leads to unacceptable performance degradation. Estimates suggest that post-quantum signatures will balloon the amount of data that certificate transparency logs need to store by forty times, driving the need for a redesigned architecture.
Introduction of Merkle Tree Certificates
To solve these performance and scaling barriers, Merkle Tree Certificates have emerged as the preferred path forward following broad industry support and experimental deployment with Chrome. MTCs are designed to provide compact, auditable authentication without the heavy overhead of traditional certificate chains.
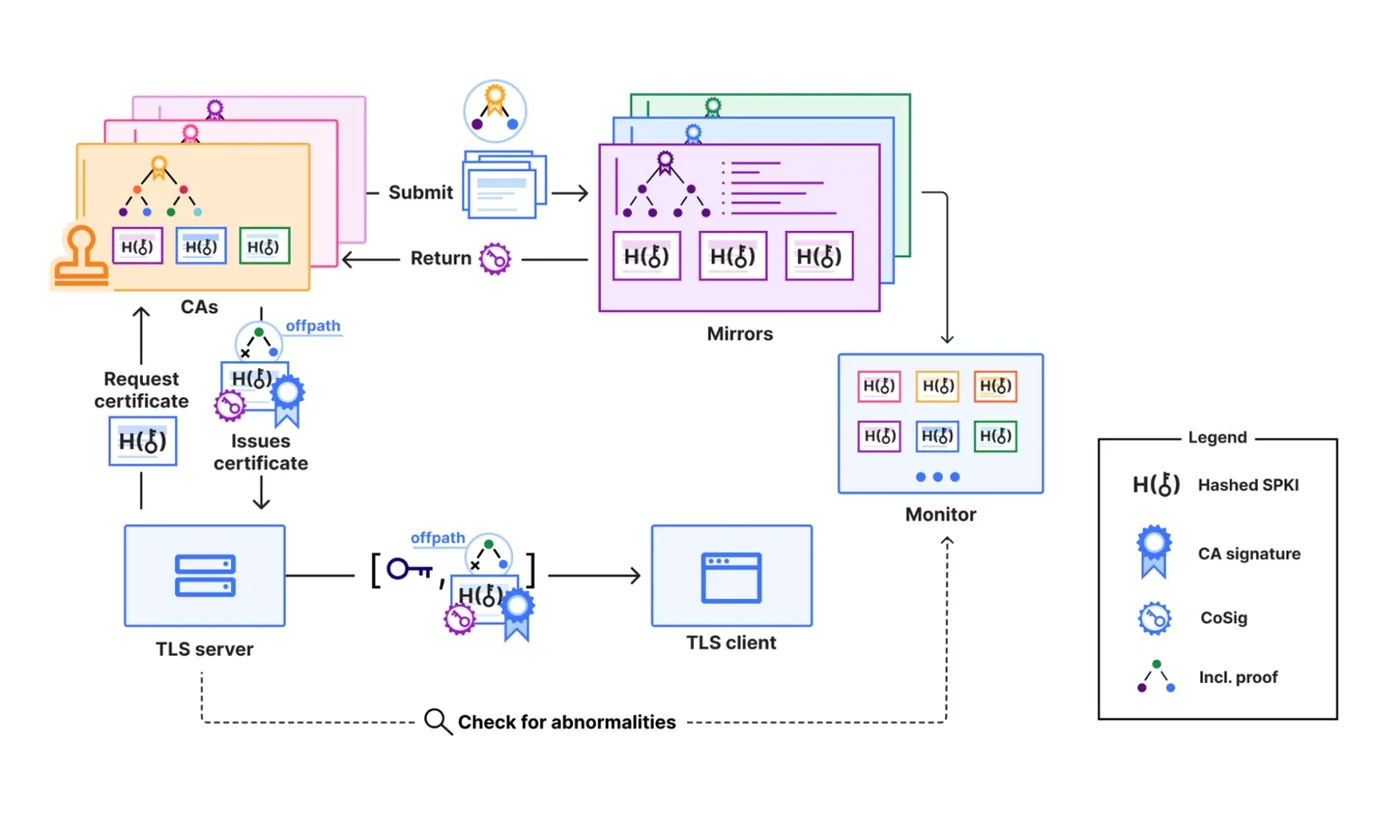
Defined in a draft specification from the IETF PLANTS working group, Merkle Tree Certificates batch certificates into an append-only Merkle tree. This allows a certificate authority to sign the root of that tree rather than signing many individual certificates separately.
Instead of validating each certificate individually, browsers and other clients can verify a certificate using a compact inclusion proof consisting of a sequence of cryptographic hashes against a signed tree head. The core concept behind MTCs couples issuance and logging, treating transparency as a fundamental requirement rather than an add-on.
Cloudflare's New Certificate Authority
Cloudflare has announced the creation of a new certificate authority (CA) that will support MTC issuance at scale. The company is targeting early 2027 for inclusion in Chrome's newly launched Quantum-resistant Root Store.
In alignment with its mission to help build a better Internet and its tradition of offering strong cryptography for free, Cloudflare plans to provide standard MTC issuance at no cost. Operating a CA that supports both classical certificates and MTC issuance allows the organization to default to the most secure authentication method available.
Certificate Transparency and Monitoring in the Post-Quantum Era
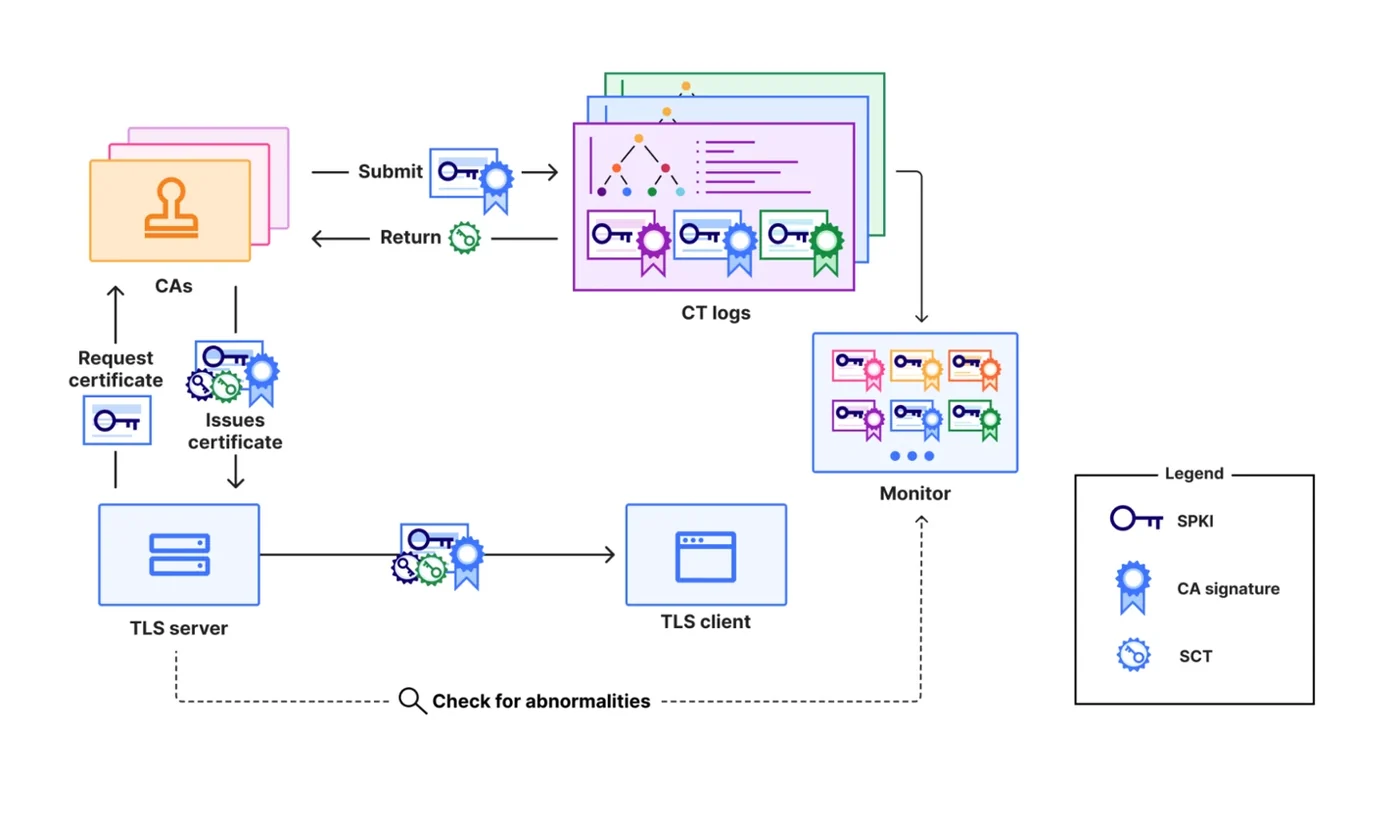
Certificate transparency makes certificate issuance publicly auditable by requiring certificates to be submitted to public logs. Cloudflare has operated the Nimbus family of certificate transparency logs since 2016 and is introducing Raio as a new family of static CT logs going forward.
As organizations upgrade their servers to use post-quantum authentication, certificate transparency monitoring will play an essential role in detecting potential post-quantum downgrades. Domain owners who upgrade their domains should monitor logs for unexpectedly issued legacy certificates to prevent clients from falling back on malicious downgrade paths.
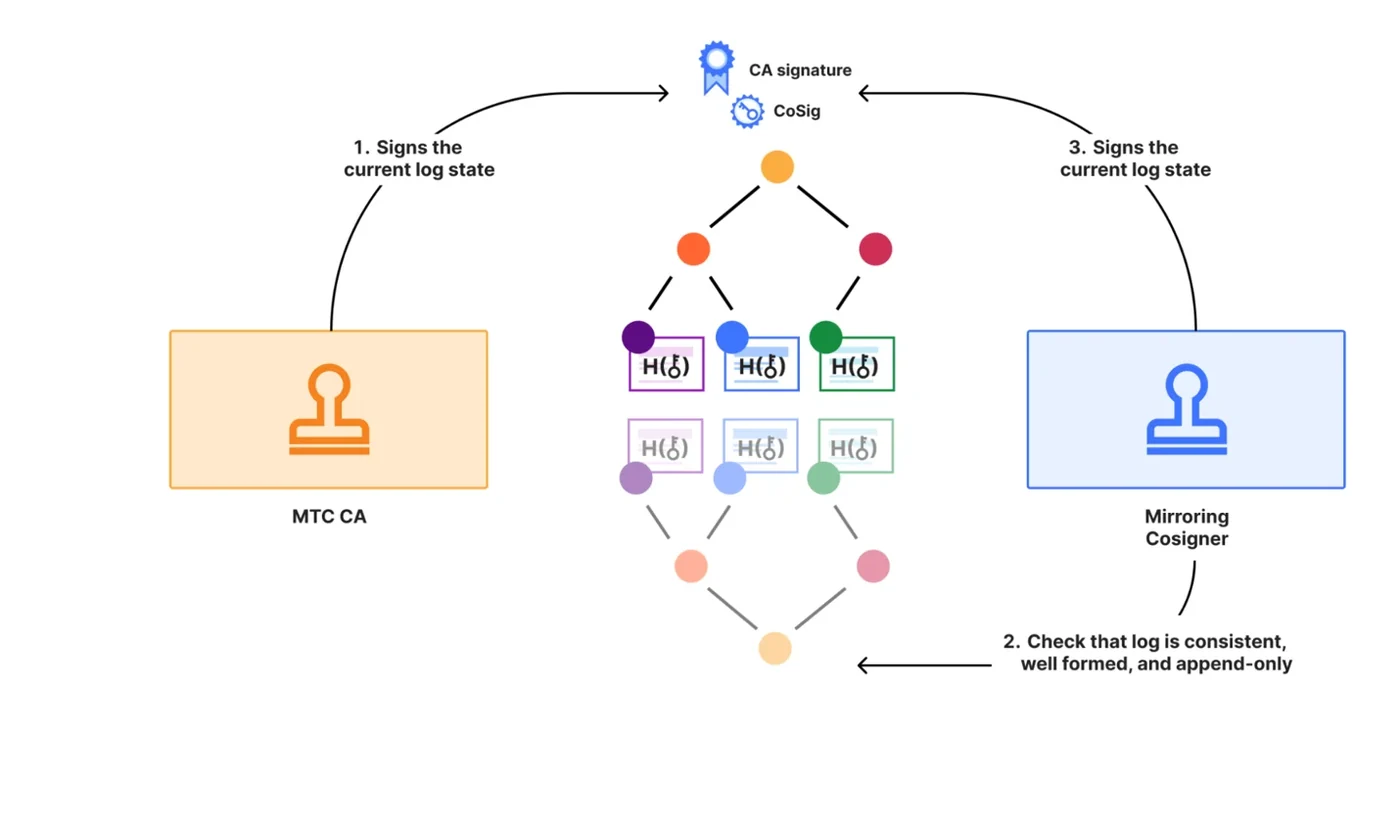
Redesigning the PKI Architecture
Building out the capability to issue Merkle Tree Certificates forms an integral part of Cloudflare's creation of its new CA. The process involves tracking new post-quantum Root Program requirements while simultaneously writing an issuance and mirroring software stack alongside traditional compliance and operational functions.
While the core responsibilities of a certificate authority remain centered on validating domain control, binding domains to public keys, and issuing certificates, the MTC ecosystem shifts the workflow. Instead of signing certificates directly and subsequently logging them, the CA maintains transparency directly through the structure of the Merkle tree.
Sources
- Cloudflare BlogBuilding a post-quantum certificate authority with Merkle Tree Certificates