
CISA Warns Ransomware Gangs Are Exploiting TeamCity Flaw
The U.S. Cybersecurity and Infrastructure Security Agency has updated its catalog to warn that ransomware gangs are exploiting a critical JetBrains TeamCity flaw originally patched in July.
 Radwan AbdulhadiEditor and technology writer
CISA Issues Ransomware Warning for TeamCity Flaw
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) warned federal agencies that ransomware groups are now exploiting a critical JetBrains TeamCity vulnerability that was initially patched back in July. According to reports detailed by BleepingComputer, the security agency updated its tracking data to highlight the ongoing threat.
The vulnerability itself is tracked under the identifier CVE-2026-63077. Following its discovery, CISA officially added CVE-2026-63077 to its catalog of actively exploited vulnerabilities, prompting strict compliance directives for U.S. federal networks.
Technical Details of the Authentication Bypass
JetBrains addressed the issue by shipping fixes for TeamCity On-Premises versions 2025.11.7 and 2026.1.3, characterizing the issue as a critical authentication bypass vulnerability. This flaw allows malicious actors with HTTP or HTTPS network access to execute arbitrary operating system commands directly on affected servers.
An unauthenticated attacker can leverage the vulnerability via the TeamCity agent polling protocol. By bypassing authentication checks entirely, perpetrators can execute arbitrary OS commands using the privileges tied to the TeamCity server process. Depending on how those privileges are configured, a successful attack can easily expose sensitive data, modify server states, and compromise downstream CI/CD pipelines.
Catalog Update and Active Exploitation
After JetBrains confirmed that the security flaw was actively exploited in the wild, the company shared indicators of compromise and urged customers to restrict server access if immediate patching was not feasible. CISA has since expanded its catalog of actively exploited vulnerabilities to reflect the evolving nature of these threat campaigns.
While detailed specifics regarding the exact attacks targeting this vector remain limited, CISA formally flagged the vulnerability as being abused by ransomware gangs in its KEV catalog updates. Since October 2023, the agency has recorded four distinct TeamCity security issues that have been exploited in the wild and subsequently leveraged in ransomware incidents.
Current Internet Exposure and Mitigation
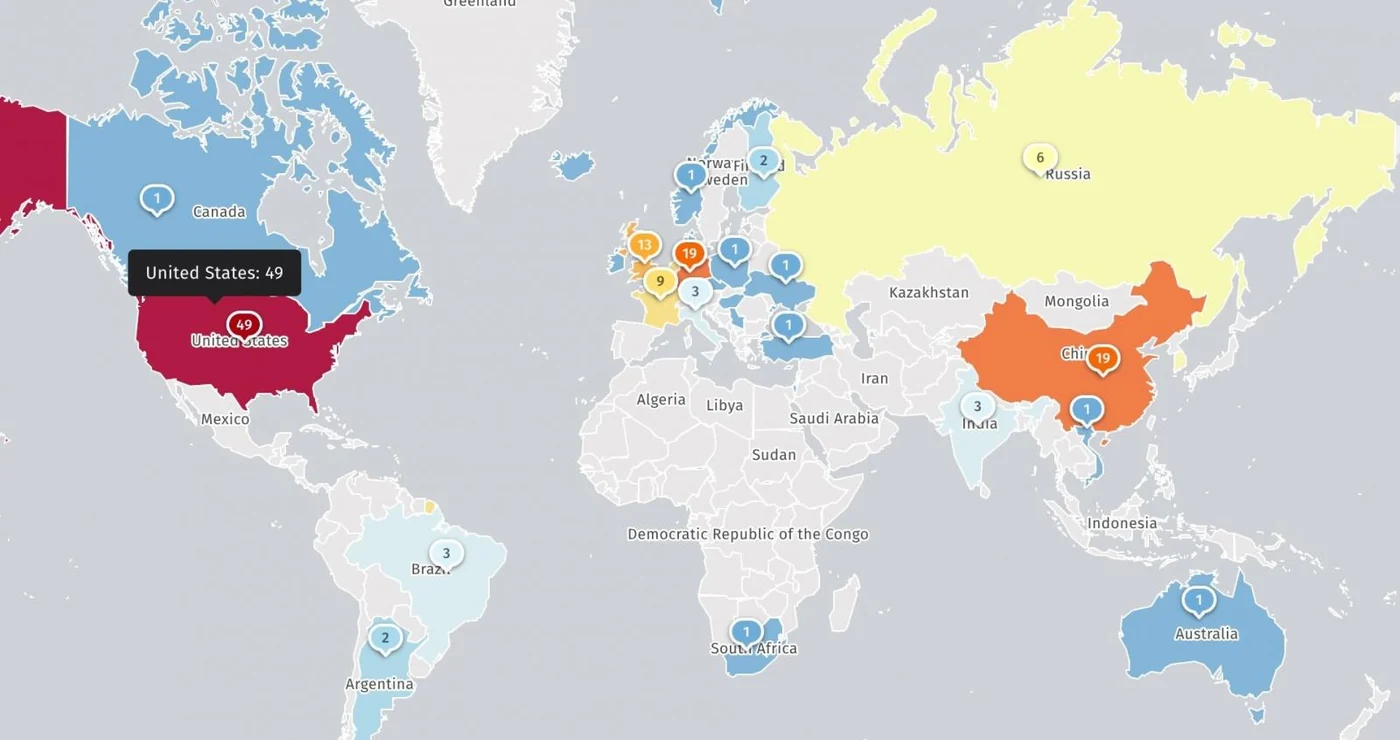
Security intelligence and threat watchdogs continue to monitor the landscape for vulnerable endpoints. According to data compiled by Shadowserver, there are currently just over 160 TeamCity servers remaining unpatched against the flaw. This figure represents a notable improvement from the approximately 700 Internet-exposed systems originally spotted immediately after the patch was released.
Because both state-backed hacking groups and criminal ransomware syndicates routinely target integration platforms, administrators are strongly advised to apply updates immediately. Prior incidents have demonstrated that continuous integration servers remain prime targets for espionage and extortion campaigns alike.
Sources
- BleepingComputerCISA: Ransomware gangs now exploiting critical TeamCity flaw