Microsoft and Japan Take Down Giant Phishing Network
A joint international investigation led to the disruption of a sprawling Chinese-language cybercrime infrastructure that powered over a billion malicious phishing messages across more than 150 countries.
 Radwan AbdulhadiEditor and technology writer
International Takedown Targets Cybercrime Marketplace
Microsoft, in collaboration with Japan's National Police Agency, has successfully helped dismantle a massive global cybercrime operation that facilitated more than a billion malicious phishing messages. According to a detailed report from <a href="https://www.bleepingcomputer.com/news/security/global-takedown-hits-network-behind-1-billion-phishing-messages/">BleepingComputer</a>, the international disruption targeted an expansive ecosystem used by threat actors to launch widespread SMS and email attacks.
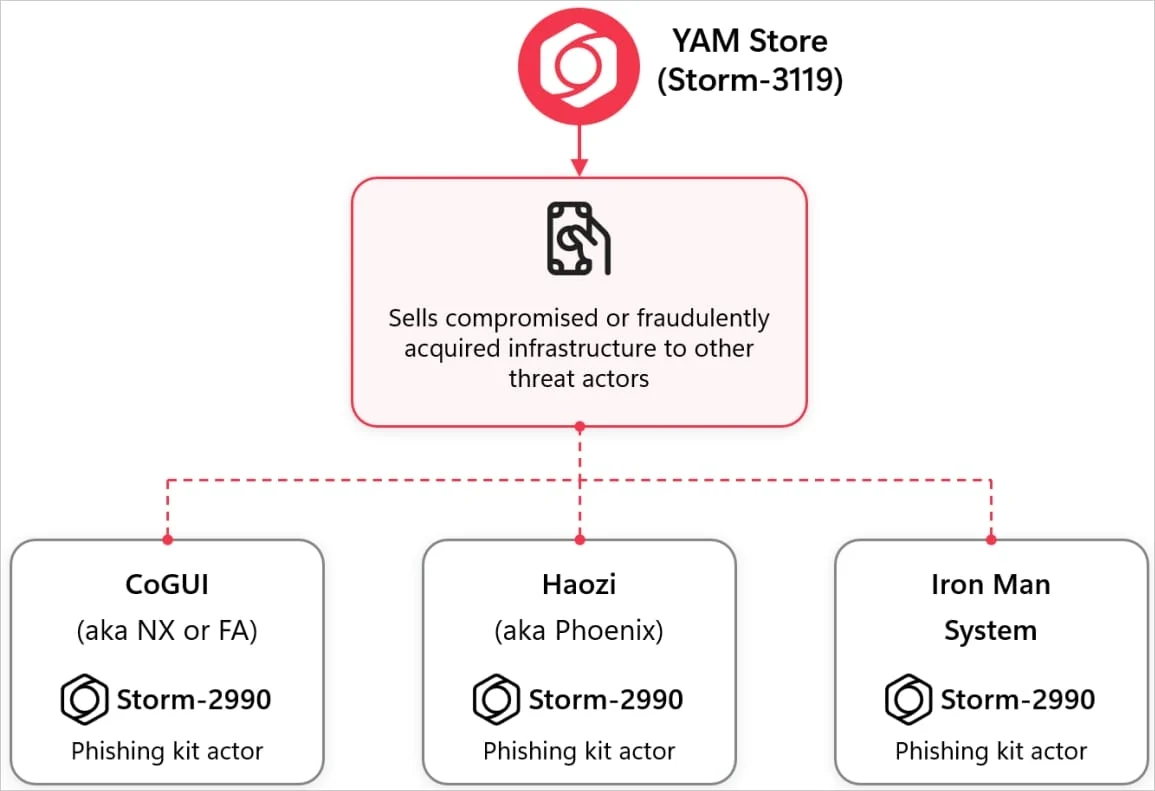
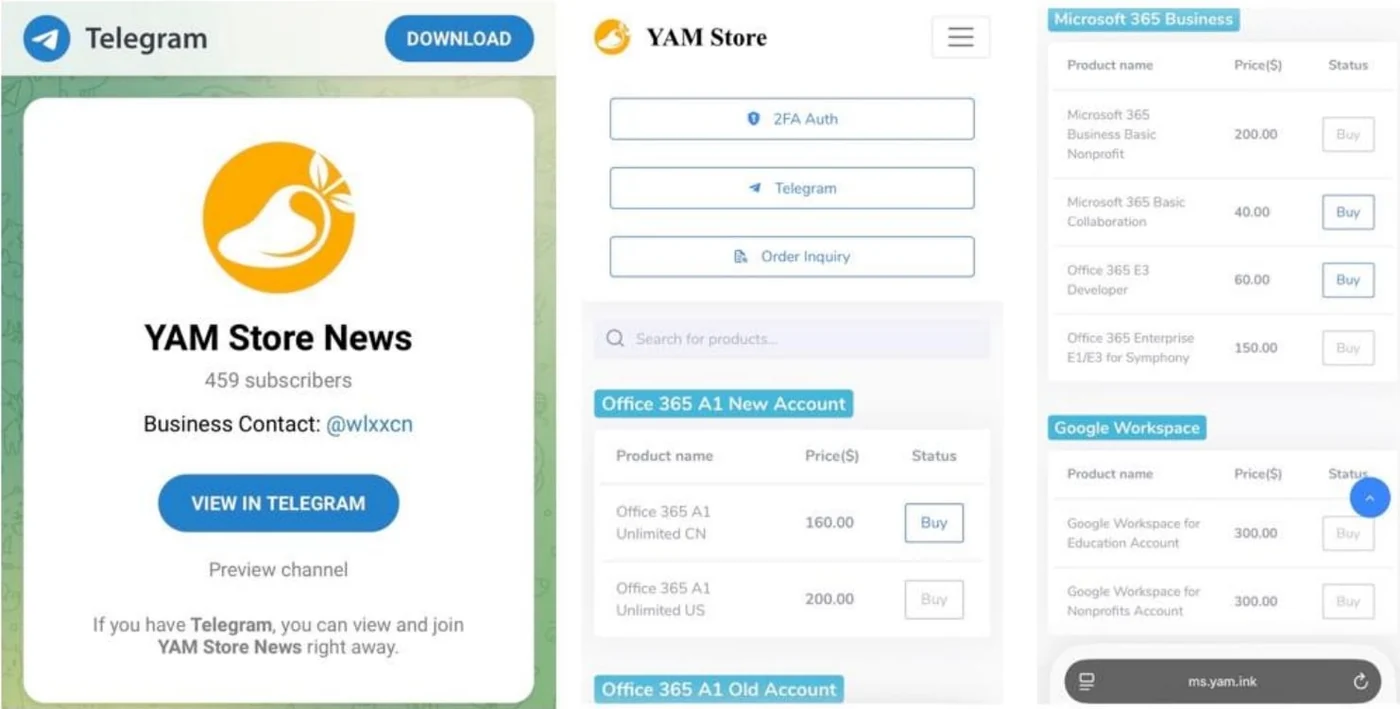
The investigation traced the fraudulent activity back to a sprawling Chinese-language underground infrastructure marketplace known as YAM Store, alongside a pair of major phishing kits designated as CoGUI and Iron Man. Together, these platforms generated tens of millions of dollars for their operators while targeting consumers, financial institutions, healthcare organizations, and other businesses.
Scale of the Global Phishing Ecosystem
Since January 2026, the dismantled network collectively enabled more than one billion malicious messages targeting over 75,000 organizations across more than 150 countries. Among those targets, more than 750 million messages were specifically geared toward Microsoft customers, often utilizing device-code phishing methods to obtain authentication tokens.
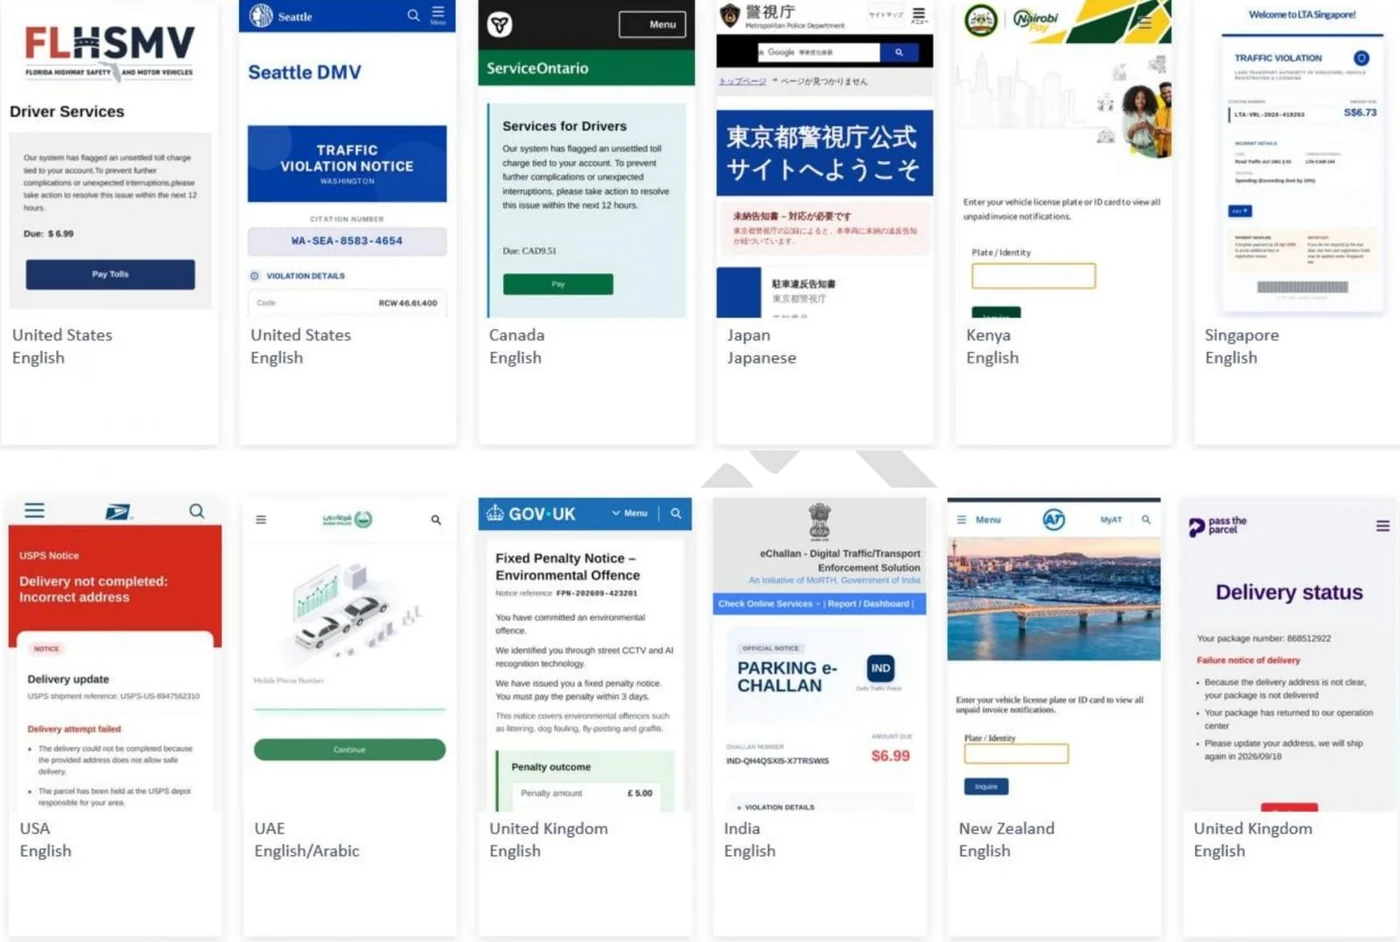
The scale and methods of the operation were outlined further when <a href="https://blogs.microsoft.com/on-the-issues/2026/10/14/disrupting-the-service-economy-behind-transnational-cybercrime-operations/">dismantle a marketplace for scammers</a> became a primary objective for the tech giant and its law enforcement partners. Investigators noted that scammers used the infrastructure to deploy fake lures concerning nonexistent parking tickets, package delivery problems, traffic penalties, and account verification requests.
Exploiting Expired Domains and AI Generation
The YAM Store marketplace functioned by selling stolen or fraudulently acquired Microsoft and Google accounts, environments, licenses, and storage to cybercriminals. Operators systematically acquired expired web domains belonging to real organizations, rebuilding defunct websites to make them appear active and legitimate.
In addition to hijacking expired domains, the threat actors utilized artificial intelligence tools to generate entirely fake organizations, complete with supporting content and documentation. Within compromised Microsoft environments, operators abused SharePoint and OneDrive storage for hosting phishing assets while managing accounts through stolen application credentials.
Phishing Kits and Enterprise Impersonation
The infrastructure relied heavily on advanced phishing kits like CoGUI and Iron Man to evade security analysts. While CoGUI initially targeted victims in the United States and Japan, the Iron Man platform eventually took precedence by mid-2026, offering over 2,300 templates designed to impersonate banks, retailers, delivery services, and government agencies.
Security researchers, including firms like Resecurity, analyzed the exposed infrastructure of the Iron Man system and uncovered extensive product-selection subsystems linked to payment-card capture. Additional historical threat intelligence, such as email campaigns tracked by Proofpoint, had previously identified similar Chinese-language phishing kits consistently targeting entities in Japan.
Enforcement Actions and Domain Seizures
Following a court order from the U.S. District Court for the Southern District of Florida, coordinated enforcement actions were taken to dismantle the network. <a href="https://www.microsoft.com/en-us/security/blog/2026/10/14/the-hidden-network-inside-the-phishing-infrastructure-ecosystem-powering-global-cybercrime/">report</a> details that Microsoft worked alongside health sector cybersecurity non-profit Health-ISAC to successfully seize and redirect web domains powering YAM Store, CoGUI, and Iron Man.
In total, Microsoft disabled over 20,000 accounts connected to the YAM Store marketplace and blocked more than 100,000 web domains that were actively being used for impersonation and fraud. Additional takedown efforts and infrastructure removals are continuing globally with support from various international cybercrime coordination centers and security partners.
Sources
- The VergeMicrosoft and Japan took down a cybercrime network behind over a billion scam messages
- BleepingComputerGlobal takedown hits network behind 1 billion phishing messages
Continue chronologically
Related entity coverage
Related stories
Global Law Enforcement Takedown Hits Phishing Network
Law enforcement and global partners disrupt a massive cybercriminal ecosystem responsible for over one billion malicious phishing messages.
Microsoft Disrupts Chinese Phishing Market Behind 1B+ Messages
Microsoft and Health-ISAC seize domains powering YAM Store, CoGUI, and Iron Man, disrupting a massive Chinese-language phishing-as-a-service market.
Microsoft Disrupts EvilTokens Phishing-as-a-Service Platform
Microsoft's Digital Crimes Unit has disrupted the EvilTokens phishing platform, which compromised 12,000 accounts across 10,000 global organizations.
Microsoft Authenticator Replaces Backup With Google One
Microsoft Authenticator for Android is replacing its own password and account backup system with Google One starting in January.