Synology Issues Urgent Warning Over C3RB3R Ransomware Attacks
Taiwanese network-attached storage maker Synology has issued an urgent security warning to customers following a sharp rise in C3RB3r ransomware attacks targeting outdated devices.
 Radwan AbdulhadiEditor and technology writer
Urgent Security Warning Issued for Synology NAS Devices
Taiwanese network-attached storage appliance maker Synology has issued an urgent warning to its customer base, urging users to update their devices immediately following a noticeable surge in C3RB3r ransomware attacks. The company published details regarding the threat in a Thursday advisory, calling on all system owners to take immediate protective measures.
To safeguard sensitive data from ongoing compromise, the storage manufacturer strongly recommends that users enable automatic updates and upgrade the DiskStation Manager software running on their network-attached storage hardware to the latest available version.
Exploiting Outdated Software and Vulnerabilities
According to the company's security communications, threat actors have actively exploited a critical vulnerability originally patched in December 2024 to target network-attached storage hardware running older iterations of the DiskStation Manager operating system. These malicious campaigns are specifically designed to encrypt user files and extort heavy financial payments.
Although Synology has not explicitly named the exact vulnerability driving the current wave of intrusions, the organization directed users to its November 2024 security advisory. That bulletin detailed previously addressed security flaws that allowed attackers to execute arbitrary code under CVE-2024-10441, read files under CVE-2024-50629, and write files under CVE-2024-10445 on unpatched systems.
Security experts and the manufacturer advise customers to immediately block external access to the management web interface from the public internet as an additional precautionary layer.
Widespread Customer Impact and Ransom Demands
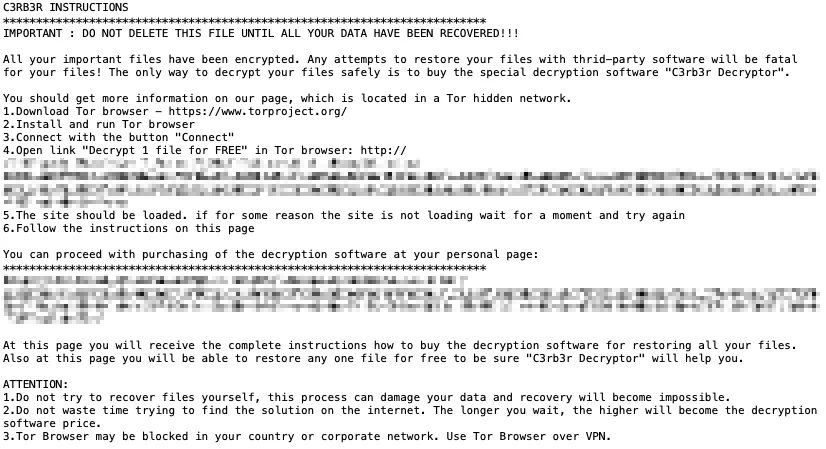
The manufacturer's alert follows a massive wave of public reports from system owners whose files were encrypted by the malicious software. Impacted individuals have been prompted via drop notes to purchase a specialized decryption tool from a dark web portal in exchange for thousands of dollars.
The first public user warnings surfaced more than two weeks ago across online community forums, with affected users confirming that the malware deploys a ransom note titled read-me3.txt and appends a .L0CK3D file extension to all compromised documents.
The ransom note explicitly warns victims that attempting to recover files using alternative third-party tools could cause permanent data destruction, leaving purchase of the proprietary decryptor as the only viable recovery path presented by the operators.
Historical Context of Synology and C3RB3R Attacks
Synology rarely issues security advisories warning of attacks directly targeting customer hardware. The last comparable security alert of this nature was published in August 2019 following widespread brute-force intrusion campaigns that resulted in eCh0raix ransomware infections across vulnerable storage systems.
The C3RB3R designation currently appearing in these network-attached storage attacks borrows its moniker from an older Ransomware-as-a-Service operation that emerged in 2016. Prior to winding down its operations at the end of 2019, the historical Cerber variant accounted for a major fraction of global ransomware activity targeting enterprise environments.
Meanwhile, internet threat intelligence gathered by the Shadowserver Foundation indicates that over 380,000 Synology network-attached storage devices remain directly exposed to the public internet, highlighting the extensive potential surface area for these ongoing cyberattacks.
Sources
- BleepingComputerSynology warns of C3RB3R ransomware attacks targeting NAS devices
Continue chronologically
Related stories
Synology NAS Hit by Ransomware via 18-Month-Old Exploit
An internet-accessible Synology DS918+ NAS fell victim to a ransomware attack after running 18 months behind on security patches and exposing its web interface.
CISA Confirms Active Exploitation of Maximum-Severity GitLab Flaw
CISA confirms active exploitation of a maximum-severity GitLab vulnerability tracked as CVE-2026-97229 and urges administrators to apply patches immediately.

CISA Warns Ransomware Gangs Are Exploiting TeamCity Flaw
CISA alerts federal agencies that ransomware gangs are now actively exploiting a critical JetBrains TeamCity authentication bypass vulnerability.
Kiteworks Patches Max-Severity Code Injection Flaw
Secure file-sharing company Kiteworks releases security updates addressing 126 vulnerabilities, including a max-severity code injection flaw in its EPG solution.