Google Freezes Open Source Bug Bounty Program Over AI Influx
Google has temporarily suspended a key bug bounty initiative after being overwhelmed by automated, invalid reports and hallucinations generated by artificial intelligence tools.
 Radwan AbdulhadiEditor and technology writer
Program Suspension and Timeline
Google has officially paused its open source bug bounty program following a dramatic and unprecedented surge in automated submissions. In announcements shared via <a href="https://x.com/GoogleVRP/status/2105689195180179605">on X</a> and <a href="https://bughunters.google.com/about/rules/open-source/google-open-source-software-vulnerability-reward-program-rules#reward-amounts">the program website</a>, the tech giant confirmed that the Open Source Software Vulnerability Rewards Program was suspended effective October 1. The initiative previously rewarded independent researchers for discovering security vulnerabilities within the company's various open source software projects.
While the pause has left open-source security researchers without this specific avenue for compensation for the time being, Google has committed to providing a formal status update during the first quarter of 2027. Until then, the submission portal remains closed for vulnerability reporting under this specific framework.
The Impact of AI Slop on Security Teams
The primary catalyst behind the sudden freeze is an influx of low-quality, automated content often referred to as AI slop. <a href="https://techcrunch.com/2026/10/04/google-froze-its-open-source-bug-bounty-program-due-to-a-significant-rise-in-ai-submissions/">TechCrunch</a> originally detailed how cybersecurity experts and industry analysts have been warning for months that generative artificial intelligence tools posed a severe risk of overwhelming structured bug bounty programs with noise rather than signal.
As generative technologies have become more accessible, malicious actors and misguided hobbyists alike have increasingly leveraged automated systems to spit out vulnerability claims. These tools frequently produce convincing-looking reports that lack any grounding in reality, forcing security triage teams to spend valuable engineering hours separating legitimate findings from automated garbage.
Engineering Burnout and Hallucinations
<a href="https://www.tomshardware.com/tech-industry/artificial-intelligence/google-suspends-part-of-the-oss-vrp-bug-bounty-program-due-to-an-influx-of-invalid-ai-submissions-product-vulnerability-submissions-ended-october-1">According to Tom’s Hardware</a>, the volume of incoming reports became entirely unsustainable for internal staff. Google engineers and independent open source maintainers found themselves buried under an avalanche of invalid vulnerability claims and severe hallucinations produced by automated scripts and LLMs.
Because open source projects often rely on small communities of maintainers who volunteer their time or split duties with other engineering tasks, processing hundreds of bogus security alerts can completely paralyze software development cycles. The sheer ratio of invalid submissions to genuine threat disclosures left the company with few alternatives other than a hard operational freeze.
Google Official Statements and Context
Addressing the public and the broader developer ecosystem, Google did not mince words regarding the quality of the recent influx. The company explicitly noted that the suspension was enacted due to a notable spike in automated entries, emphasizing that the vast majority of these incoming reports possessed zero validity.
“This pause is due to a significant rise in automated submissions, the vast majority of which are not valid,” Google stated in its public announcements. The move highlights a growing industry-wide vulnerability where open protocols and crowdsourced security frameworks are being weaponized or simply drowned out by generative tools.
Alternative Options for Bug Hunters
For researchers and security professionals who still wish to contribute valid findings to Google's ecosystem, the company has offered a path forward during the interim period. Participants who previously focused exclusively on the open source vulnerability rewards program are encouraged to explore Google’s other active bug bounty programs.
Whether these alternative channels will implement stricter filtering mechanisms, rate limits, or automated screening tools to defend against the same wave of artificial intelligence-generated submissions remains to be seen. However, the temporary closure of the open source initiative serves as a stark warning to the wider tech industry about the hidden operational costs of unmonitored automation.
Sources
- TechCrunchGoogle froze its open source bug bounty program due to a ‘significant rise’ in AI submissions
Continue chronologically
Related entity coverage
Related stories
Google Freezes Open-Source Bug Bounty Amid AI Slop
Google suspends product vulnerability submissions for its OSS VRP bug bounty program until 2027 following an influx of invalid AI reports.
Brian Chesky: AI Agents Need an AI-Native Operating System
Airbnb CEO Brian Chesky discusses the state of consumer AI, the limits of current chatbots, and why AI agents require a dedicated operating system.
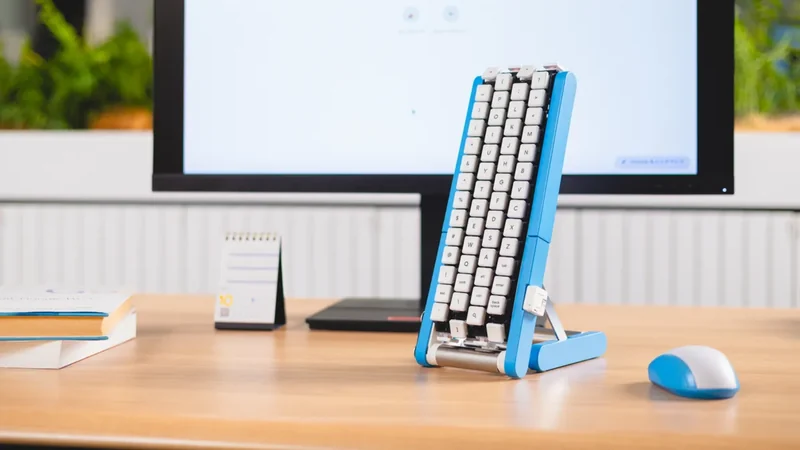
Google Japan Reveals Conveyor-Belt Gboard Keyboard
Google Japan has unveiled its latest quirky keyboard creation: a 3D-printable Gboard featuring moving conveyor belts designed for easier one-handed typing.
Google Introduces New Model Access Limits for Gemini Users
Google is updating the Gemini app to restrict model access for free and AI Plus users, while expanding Deep Think capabilities for higher-tier subscribers.