PoeLLM Cryptomining Malware Hits Over 3,400 Servers
A newly detailed cryptomining campaign has successfully targeted thousands of exposed servers, leveraging an unconventional command-and-control mechanism hidden inside a poem hosted on GitHub.
 Radwan AbdulhadiEditor and technology writer
Overview of the Canto Incognito Campaign
A sophisticated malware campaign tracked since April 2026 has successfully impacted more than 3,400 victim servers. According to [Black Lotus Labs reports](https://www.lumen.com/blog/en-us/canto-incognito-tracking-the-poellm-malware), the operation—dubbed Canto Incognito—utilizes a specialized piece of [cryptomining malware](https://www.tomshardware.com/tech-industry/artificial-intelligence/microsoft-warns-gpu-mining-malware-is-being-spread-to-users-through-seo-poisoning-and-ai-chatbots-cryptojacking-campaign-targets-gamers-and-high-end-pc-users-with-downloads-disguised-as-popular-pc-utilities) known as PoeLLM. Researchers discovered that the infrastructure relies on an unusual command-and-control configuration, pointing toward financially motivated actors looking to exploit expanding enterprise attack surfaces.
Detailed findings on the campaign were highlighted by [Tom's Hardware](https://www.tomshardware.com/tech-industry/cyber-security/cryptomining-malware-used-poetry-to-infect-more-than-3-400-servers-researchers-say-four-words-in-the-poellm-verse-changed-11-times-point-the-botnet-to-new-servers), noting that the primary commonality among the initial wave of victims involved communication with endpoints tied to Russian crypto mining services. As AI infrastructure grows rapidly, researchers warn that exposed environments present lucrative targets due to valuable data and hardware access, particularly GPUs.
The GitHub Poetry Command Mechanism
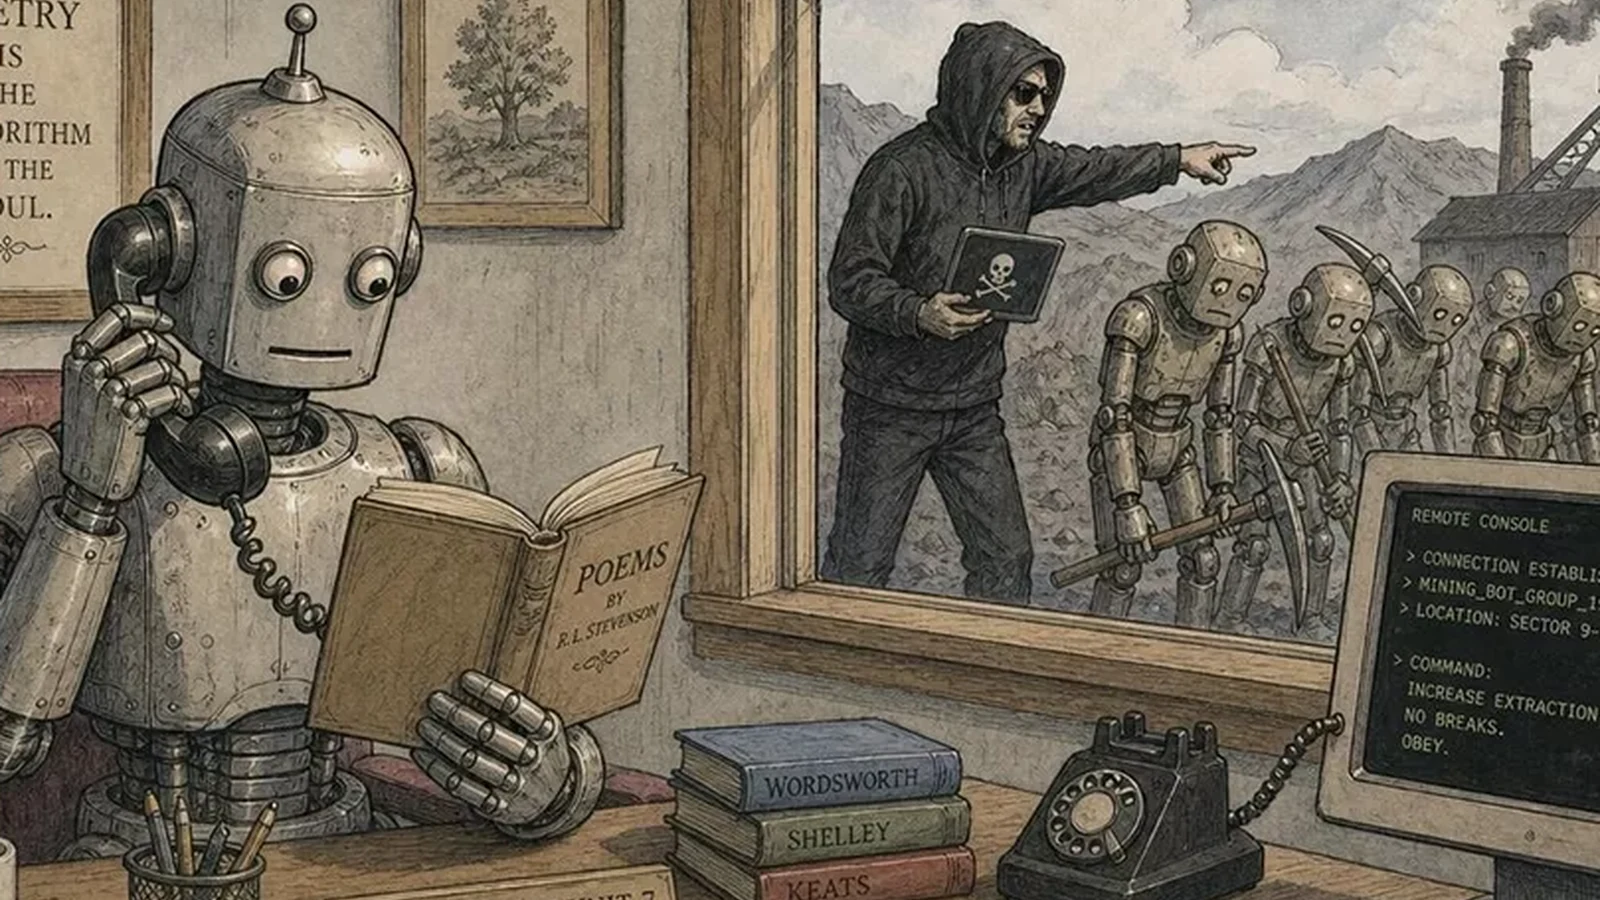
One of the most distinctive aspects of the PoeLLM malware is its command-and-control (C2) mechanism. Instead of relying on hardcoded IP addresses or standard domain generation algorithms, the malware encodes its C2 server addresses into a two-stanza poem hosted on GitHub titled 'On the Nature of Connection.'
First committed in April, the poem features specific words that the malware parses and decodes into valid IPv4 addresses. This verse has been altered 11 times so far, with each new version updating the botnet to direct infected hosts to fresh C2 servers. Security researchers note that utilizing a poem served as a clever obfuscation vehicle for hiding important instructions, though they clarify this is distinct from adversarial poetry or AI prompt injection attacks.
Targeted Open-Source AI and Enterprise Services
The vast majority of the compromised servers were running vulnerable open-source artificial intelligence and large language model services. Prominent targets include LiteLLM, which acts as a proxy server and AI gateway allowing companies to route application traffic across multiple models through a single endpoint. Gotenberg, a Docker-based API for PDF conversion that explicitly warns against internet exposure, was also hit.
Additional platforms affected by the scanning and exploitation activity include Ollama—which runs open-weight models locally—and Gitea, a self-hosted Git platform. Enterprise gateway appliances like Ivanti Sentry may have also been targeted, with a single instance of an Ivanti Sentry device leading Lumen researchers to initially uncover the wider campaign.
Exploitation Vectors and Payloads
Broad scanning for vulnerable endpoints began in May, driven by the exploitation of publicly exposed services. For LiteLLM, researchers point to a crafted POST request directed at the connection endpoint as the likely exploitation path. This vulnerability—tracked as CVE-2026-42271, where two endpoints could execute supplied commands on the host without role checks—was added to CISA's catalog of exploited vulnerabilities in June.
Once a server is successfully breached, the malware deploys payloads consisting of XMRig and Iron miners connected directly to Kryptex mining infrastructure. Furthermore, the newly infected servers are weaponized to act as scanners and exploit servers, propagating the infection to additional targets across the web.
Mitigation and Recommended Security Steps
At the time of reporting, Lumen confirmed that it successfully blocked all traffic moving to and from the PoeLLM C2 servers, though three of the 12 original command servers remained active and continued attempting to infect new victims. Network administrators are urged to review connection logs against indicators of compromise provided on Lumen's GitHub page.
To secure systems against similar threats, organizations should audit external exposure when installing open-source tools, close unnecessary network ports, and apply patches immediately. Specific advisory recommendations include updating LiteLLM to version 1.83.7 or later, and updating Ivanti Sentry to versions R10.5.2, R10.6.2, or R10.7.1 as outlined by security bulletins.
Sources
- Tom's HardwareCryptomining malware that locates its control server in a GitHub poem has hit more than 3,400 servers, researchers say
Continue chronologically
Related entity coverage
Related stories
GitHub Copilot CLI Adds Local Model Discovery Support
GitHub Copilot CLI version 1.0.94-0 introduces local model discovery, letting developers choose supported models directly from their workflows.
GitHub Adds BYOK Support to Copilot Usage API
GitHub updates its Copilot usage metrics API to separate bring-your-own-key usage and enterprise custom models from Copilot-hosted data.
GitHub Copilot in Visual Studio 2026 September Update
The September 2026 update for GitHub Copilot in Visual Studio introduces Git agent pull request exploration, BYOM updates, and NuGet vulnerability fixes.
GitHub Copilot Weekly Releases Bring New Features and Controls
Discover the latest GitHub Copilot weekly releases, featuring Claude Haiku 5.5, local sandboxing, improved multi-account management, and updates.