GitHub Adds User Attribution and Telemetry Controls
Enterprise administrators gain new managed settings to attribute GitHub Copilot activity to users while keeping sensitive prompts, responses, and tool content strictly private.
 Radwan AbdulhadiEditor and technology writer
New User Attribution Capabilities for Enterprise Administrators
Enterprise administrators can now utilize telemetry in managed settings to attribute GitHub Copilot activity directly to an individual user. This process is designed to work effectively without collecting the user's prompts, responses, or underlying tool content. More details can be found on the [GitHub Changelog](https://github.blog/changelog/2026-10-12-client-telemetry-user-attribution-and-configurable-capture/).
The new identity setting introduces specific attributes to OpenTelemetry data, providing administrative visibility while maintaining strict boundaries regarding content exposure. To understand how these configurations fit into larger setups, administrators can review [the enterprise managed settings reference](https://docs.github.com/copilot/reference/enterprise-administrators/enterprise-managed-settings) for deeper architectural guidelines.
Identity Capture Settings and OpenTelemetry Attributes
The telemetry.capture.identity setting introduces three key attributes to OpenTelemetry data streams. Among these are user.name, which captures the authenticated Copilot account name as the current GitHub login, and process.user.name, which records the local operating-system account.
Identity capture remains turned off by default across environments and stays entirely separate from any existing pseudonymous user identifiers. Fine-grained capture controls are currently available in the Copilot CLI, the GitHub Copilot app, and VS Code sessions utilizing Agent Host.
Fine-Grained Independent Controls for Content Capture Classes
Beyond basic user identity attributes, administrators can independently govern five separate capture classes to tailor telemetry data collection to strict compliance or auditing requirements. Every single capture class remains completely off by default to safeguard user privacy.
The controllable classes include prompts, which encompass user, system, and developer prompts alongside supported input context. They also cover responses for assistant replies and reasoning content, toolArguments for raw tool commands and schemas, toolOutput for results and errors, and policyDetail for sandbox filesystem paths.
Precedence Rules and Legacy Configuration Support
When enterprises deploy managed settings, explicit values defined at the management level take precedence over standard local settings, software development kit configurations, and local environment variables.
The existing captureContent setting remains available for teams as a legacy shorthand to handle the five specific content classes collectively. However, this legacy setting is strictly scoped and never enables identity capture on its own.
Security Guidelines and Community Engagement
Because prompt, tool, and policy capture mechanisms can inadvertently expose sensitive information like source code, file contents, commands, and workspace paths, security teams must exercise caution. Organizations are advised to enable only the exact classes required for their specific audit use case and route telemetry securely to an approved collection endpoint.
To learn more about tracking performance and metrics, developers and administrators can also check out guidelines on how to [monitor agent usage with OpenTelemetry](https://code.visualstudio.com/docs/agents/guides/monitoring-agents). Furthermore, practitioners can join ongoing conversations by visiting the [GitHub Community](https://github.com/orgs/community/discussions/199139) discussion boards.
Sources
- GitHub ChangelogClient telemetry user attribution and configurable capture
Continue chronologically
Related entity coverage
Related stories
GitHub Copilot App Adds OpenTelemetry Support
The GitHub Copilot app now supports OpenTelemetry configuration via enterprise-managed settings, letting organizations track agent activity and performance.
GitHub Copilot adds model tiers, reviews and Sentry
GitHub Copilot’s latest weekly release adds model-selection tiers, code review improvements, Sentry integration and new agent controls.
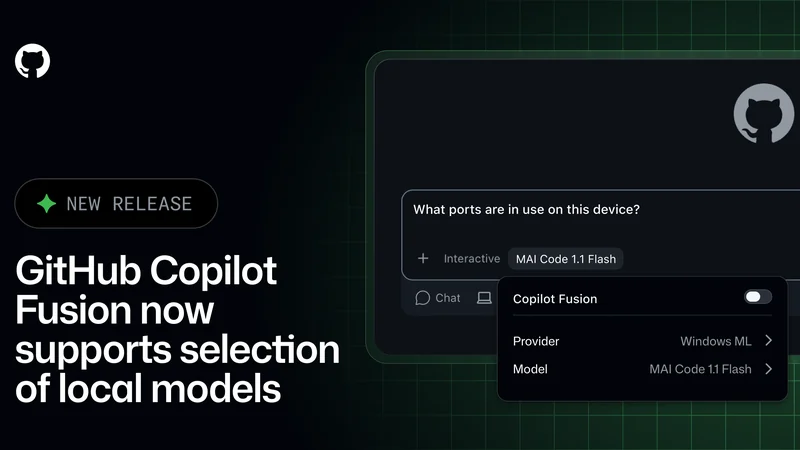
GitHub Copilot Fusion Adds Support for Local Models
GitHub Copilot Fusion now supports intelligent routing for local models in an experimental preview across the Copilot CLI, app, and VS Code.
GitHub Tightens Enterprise Copilot Settings Enforcement
GitHub is giving enterprise administrators stricter control over Copilot policies with fresh settings checks and minimum client versions.