Stolen UpdraftCentral Keys Used to Backdoor WordPress Sites
A threat actor has compromised TeamUpdraft's website and accessed customer databases, exposing UpdraftCentral connection keys to launch active backdoor attacks against connected WordPress sites.
 Radwan AbdulhadiEditor and technology writer
Security Incident at TeamUpdraft
TeamUpdraft, the developer behind popular WordPress backup and security plugins, has announced that unauthorized parties accessed its infrastructure over the weekend. According to [TeamUpdraft said](https://teamupdraft.com/blog/security-incident-october-2026/), the security incident on teamupdraft.com involved unauthorized access to the customer database, which contained critical billing details, order histories, and sensitive connection keys.
The developer offers tools such as UpdraftPlus, a website backup and restoration plugin with over [4 million downloads](https://wordpress.org/plugins/updraftplus/), alongside UpdraftCentral for remote multi-site management. Company representatives responded quickly by closing the access route, signing out user accounts, and replacing potentially affected keys and credentials.
Exposed Connection Keys and Potential Impact
The exposed customer database included connection keys for services like UpdraftCentral, UpdraftVault, and UpdraftClone. TeamUpdraft confirmed that its core plugin files, downloads, and self-hosted UpdraftCentral instances remain unaffected by the incident. However, because an estimated 10% of sites utilizing the backup tool feature an UpdraftCentral or Migrator key, roughly 400,000 websites could face exposure to downstream attacks.
Active Backdoor Campaigns and Researcher Observations
Security analysts have identified malicious campaigns leveraging the stolen credentials. As noted by [Oliver Sild](http://x.com/OliverSild/status/2112184190842392819), lead researcher at Patchstack, threat actors have begun using the stolen keys to backdoor connected sites in a campaign that may surpass previous threats.
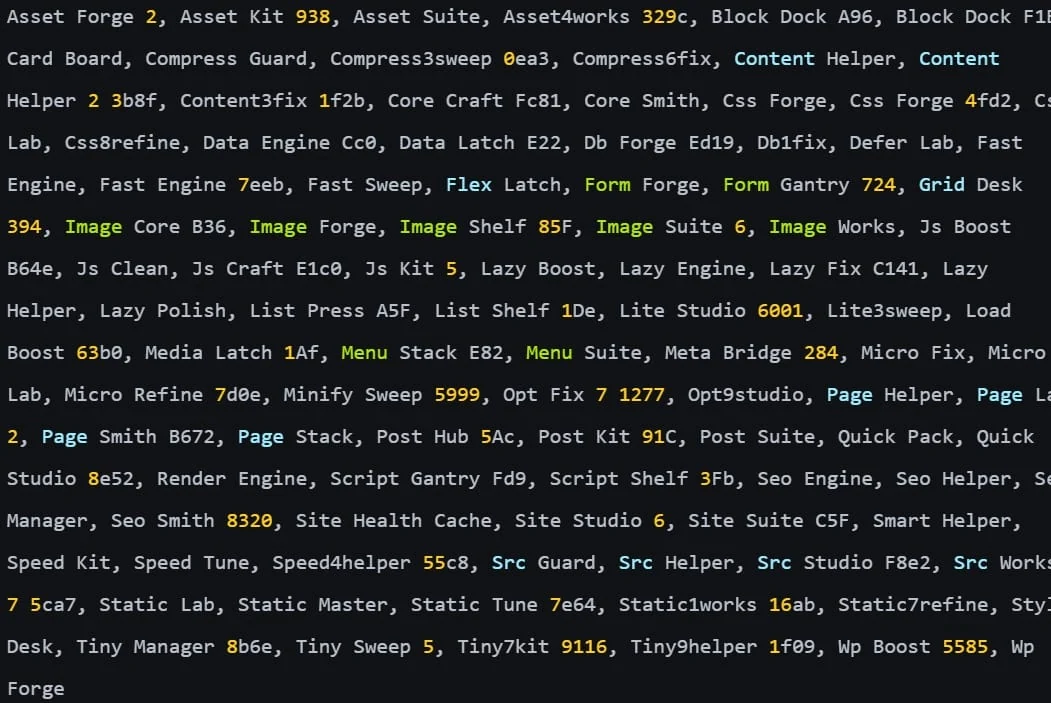
According to Patchstack, the [attacks started on October 18](http://patchstack.com/articles/updraftcentral-key-compromise-wordpress-backdoors/) to execute arbitrary code and create unauthorized accounts with full administrator privileges. Researchers logged at least 99 distinct malicious backdoor plugins disguised as maintenance and optimization tools, such as "Site Health Cache."
Further analysis from [Nethemba says](https://nethemba.com/updraftcentral-backdoor-analysis/) that newer backdoor variants allow attackers to log in as existing administrators or generate privileged accounts without exploiting underlying server vulnerabilities or software flaws.
Remediation and Mitigation Steps
To mitigate the risk of takeover, users must update UpdraftPlus to version 1.26.13 for free users or 2.26.13 for Premium users. Following the update, administrators should log into each WordPress site and delete existing UpdraftCentral connection keys by navigating to Settings, UpdraftPlus Backups, Advanced Tools, UpdraftCentral, and selecting Manage existing keys.
Administrators are also advised to inspect system logs and files for any indicators of compromise provided by TeamUpdraft, Patchstack, and Nethemba. If a compromise is confirmed, sites should be restored from clean backups immediately, team account passwords changed, sessions revoked, and two-factor authentication reset.
Sources
- BleepingComputerStolen UpdraftCentral keys used to backdoor WordPress sites
Continue chronologically
Related stories
Critical Bricksforge WordPress Plugin Flaw Under Attack
A critical vulnerability in the Bricksforge WordPress plugin is actively exploited in the wild, allowing unauthenticated threat actors to gain full control.
Ninja Forms and WooCommerce Plugins Hit by Exploitation Campaign
Hackers are actively exploiting high-severity stored XSS vulnerabilities in WordPress plugins Ninja Forms and WPC Product Bundles to compromise sites.
Amazon: PHP2Shell Exploitation Began Days Before Patches
Amazon Threat Intelligence reveals that threat actors began targeting critical PHP2Shell vulnerabilities four days before emergency patches were released.

Rank Math PRO Plugin Compromised in Supply-Chain Attack
The Rank Math PRO WordPress SEO plugin was compromised in a supply-chain attack, distributing malicious downloads that planted hidden backdoors.