OVHcloud CLI Releases Backdoored on GitHub to Steal Secrets
French cloud and hosting provider OVHcloud has warned developers and system administrators that attackers hijacked a developer's GitHub account to distribute backdoored versions of its open-source command-line interface tool.
 Radwan AbdulhadiEditor and technology writer
GitHub Repository Hijacked to Distribute Malware
French cloud and hosting provider OVHcloud has issued a security warning to users after attackers compromised its open-source command-line interface tool to distribute information-stealing malware. The threat actors managed to hijack a developer’s GitHub account to gain unauthorized entry into the OVHcloud CLI repository, subsequently modifying multiple versions of the tool.
OVHcloud offers the CLI tool as a convenient alternative for system administrators and developers to manage cloud and hosting services directly from a terminal, as well as to automate routine operational tasks. However, this repository compromise allowed malicious versions to reach users who downloaded the software during the incident window.
Detection and Response by OVHcloud Leadership
OVHcloud <span id="ceo-said">CEO said</span> that the company’s CLI repository on GitHub had been breached, urging anyone who downloaded the latest release to immediately update or remove the tool. According to the disclosure, the compromised release appeared at 14:47 on October 19 and was successfully detected and blocked at 16:21 following a customer report.
In subsequent statements, <span id="octave-klaba">Octave Klaba</span> clarified that the affected versions included v0.11.0, v0.12.0, v0.13.0, v0.14.0, and v0.15.0. Fortunately, the older version 0.10.0 and the newer release 0.16.0 were verified to be completely clean. Despite the relatively poor quality of the binary, its core objective was to retrieve developer secrets from local disks.
CI/CD Pipelines Remained Unaffected
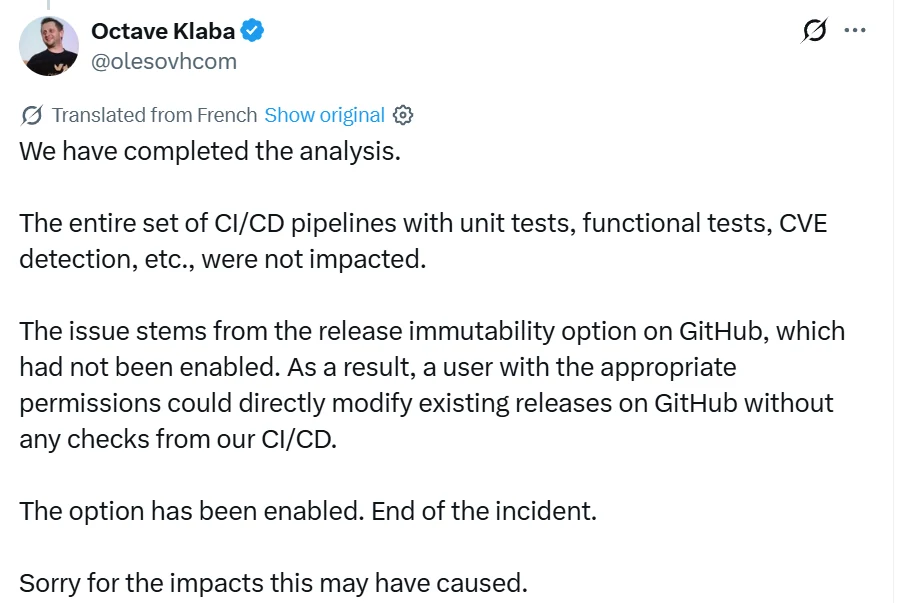
Further investigation into the incident revealed that GitHub’s release immutability setting had been disabled. This misconfiguration allowed a sufficiently privileged account to directly modify existing releases without having to pass through automated continuous integration and deployment checks.
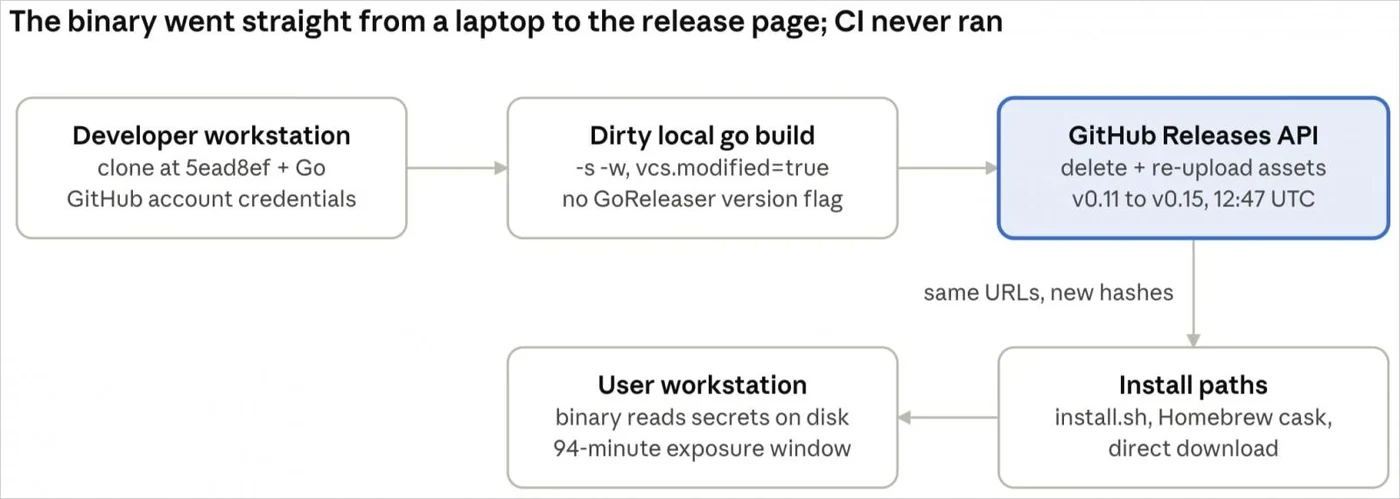
OVHcloud confirmed that the entire set of CI/CD pipelines—including unit tests, functional tests, and CVE detection mechanisms—were entirely unaffected by the breach. The attacker bypassed standard checks by uploading locally built, malware-infected packages directly through the compromised developer profile.
Connection to GlassWorm Threat Intelligence
According to <span id="opensource-malware-researchers-found">OpenSourceMalware researchers found</span>, a community-driven threat intelligence platform, this incident was likely part of a broader operation. The campaign bears similarities to previous <span id="since-late-2025">since late 2025</span> activities involving the <span id="vscode">VSCode</span>, <span id="openvsx">OpenVSX</span>, <span id="github-and-npm">GitHub, and npm</span> software development ecosystems.
Researchers noted that the specific GitHub account used in the attack had actually been compromised for more than half a year prior to the incident. Public repositories tied to the account exhibited scripted history rewrites and hidden loaders, matching established indicators for related supply-chain attacks.
Remediation and Affected Operating Systems
The trojanized packages targeted specific client environments, affecting macOS across both Intel and ARM architectures, Linux on x86_64 and ARM64, as well as Windows x86-64 systems. Importantly, building directly from the source code and utilizing official Docker images remained completely unaffected throughout the attack.
Following the discovery, OVHcloud enabled GitHub’s release immutability feature to prevent similar unauthorized modifications. However, executives strongly urge any user who downloaded an affected CLI package to perform an immediate system cleanup and revoke all stored credentials.
Security analysts point out that <span id="once-attackers-have-valid-credentials-only-37-of-their-actions-s-blocked">Once attackers have valid credentials, only 37% of their actions are blocked</span>, highlighting why thorough remediation and secret rotation are critical after any potential supply-chain exposure.
Sources
- BleepingComputerOVHcloud CLI releases backdoored on GitHub to steal developer secrets
Continue chronologically
Related entity coverage
Related stories
GitHub Copilot CLI Adds Local Model Discovery Support
GitHub Copilot CLI version 1.0.94-0 introduces local model discovery, letting developers choose supported models directly from their workflows.
GitHub Copilot Gains Desktop App Control in Public Preview
GitHub Copilot introduces computer use in public preview for the CLI and macOS and Windows apps, enabling desktop application interactions.
GitHub Deprecates All-Platform CodeQL Bundle
GitHub has officially deprecated the all-platform CodeQL bundle, directing users to adopt platform-specific binaries starting with version 2.27.0.
Hugging Face Crypto-Mining Malware Campaign Returns
A cryptomining and backdoor campaign abusing Hugging Face model repositories has quickly returned following an initial takedown.