Fake Crypto App on Apple App Store Linked to $23K Theft
A fraudulent cryptocurrency trading application previously hosted on the Apple App Store has been tied to ongoing digital asset thefts, according to security findings.
 Radwan AbdulhadiEditor and technology writer
Fake App Store Crypto Tool Linked to Thefts
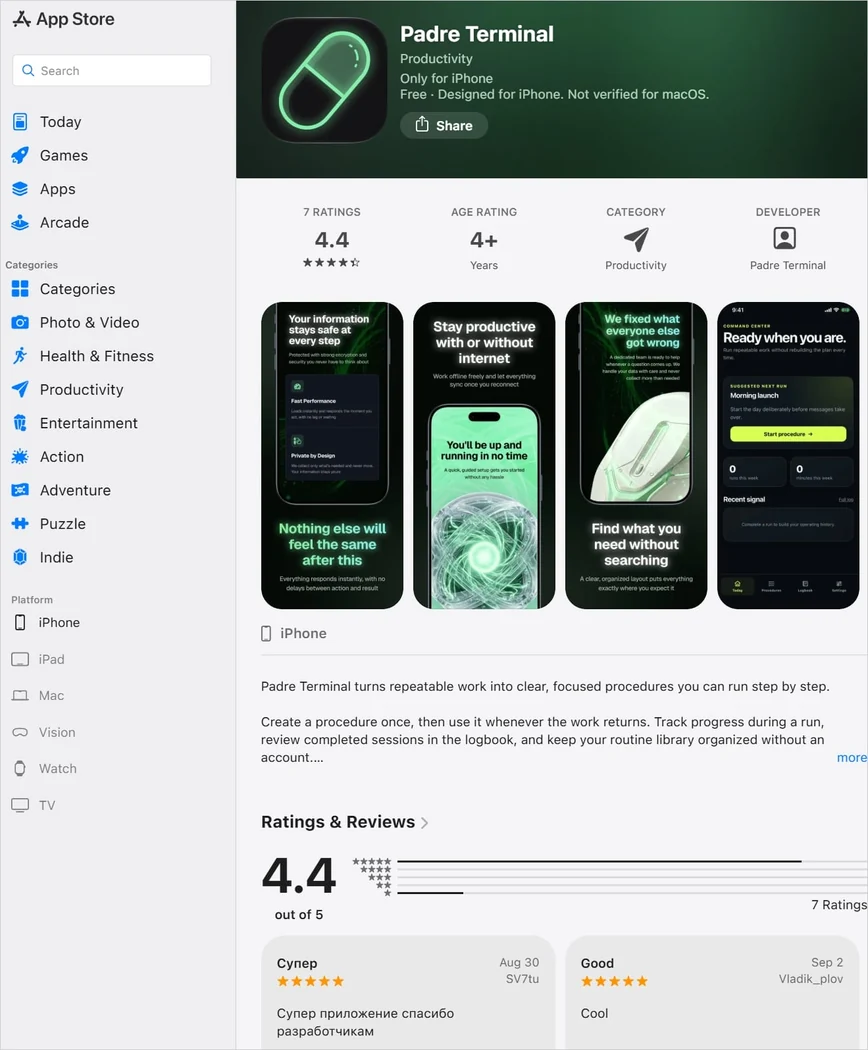
A fraudulent cryptocurrency trading application named Padre Terminal, which was previously available for iOS users on the Apple App Store, has been linked to the theft of approximately $23,000 from 27 Solana wallets. Detailed insights into the incident were originally covered by BleepingComputer, highlighting ongoing security concerns regarding malicious mobile software impersonating legitimate financial projects. Further details are available from BleepingComputer in the original source material.
According to blockchain investigator Iris, at least one victim was directly compromised via the rogue app downloaded from the official storefront, though the precise vectors for other impacted wallets are still under review. The researcher noted that the malicious utility drains cryptocurrency assets after unsuspecting users import their private keys into the program.
Impersonation of Legitimate Platform Services
The authentic Padre trading service primarily focused on buying and selling meme coins on the Solana blockchain and was later renamed Terminal by pump.fun. Investigators have clarified that the official platform operates strictly as a web-only service, meaning any mobile applications mimicking it are unauthorized and potentially dangerous.
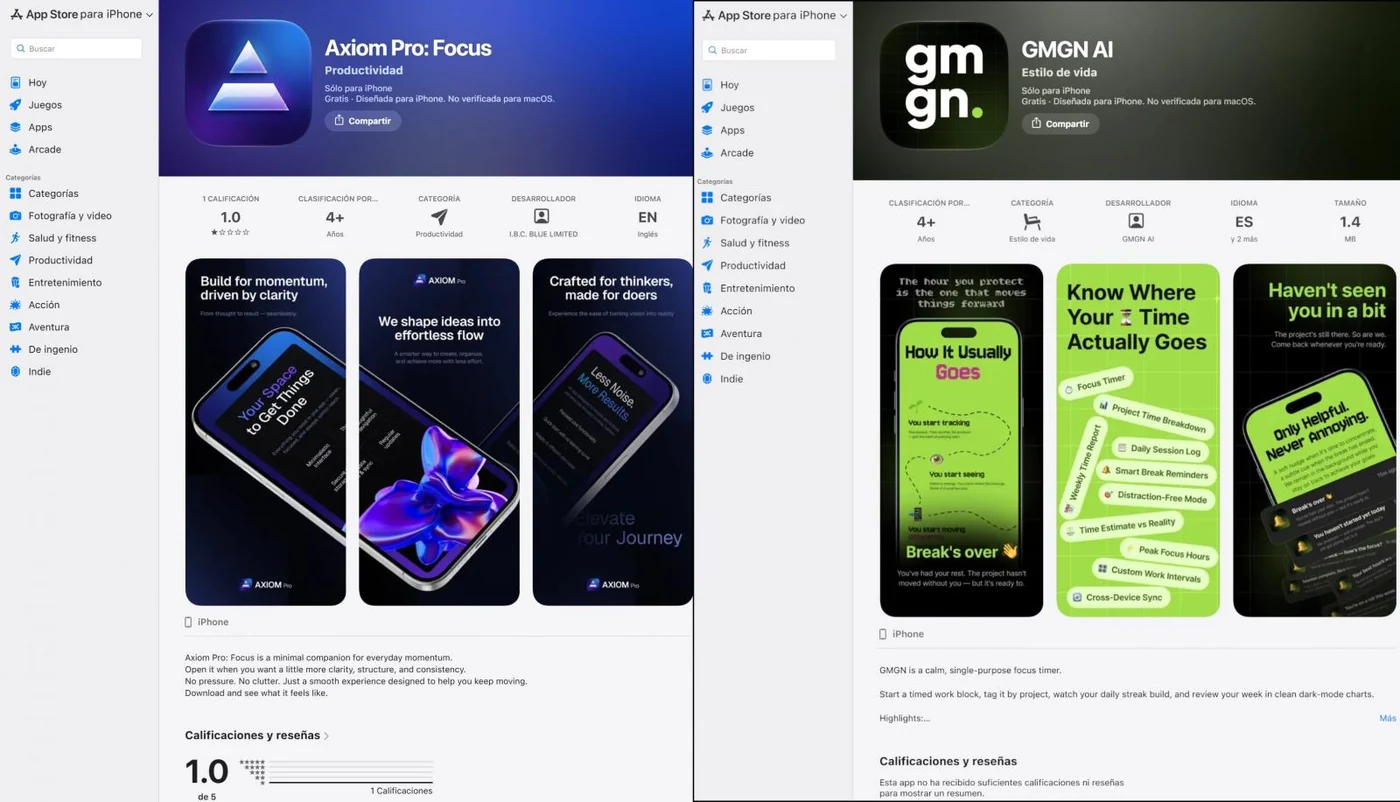
During initial investigations, multiple apps with similar names were identified on the App Store. While one served as the confirmed wallet-draining application, another represented the official pump.fun application that has been live since October 2024. The malicious Padre Terminal app has since been removed from the platform, with its direct store listing returning a 404 error.
Blockchain Tracking and Fund Movements
Blockchain tracking indicates that the malicious operation successfully drained 27 Solana wallets starting from October 25, stealing roughly $23,000 in digital assets. Stolen funds were traced directly to a specific cryptocurrency address on the blockchain network.
Further analysis by investigators revealed that the attacker converted remaining USDC tokens into SOL to prevent potential freezing actions by token issuers. The operator then transferred a significant portion of the stolen funds to a newly created recipient address. Security tracking showed substantial combined holdings across these associated accounts without immediate cash-out activity.
Broader Ecosystem Risks and Past Incidents
Security analysts have identified several other suspicious listings on the App Store impersonating popular crypto projects, featuring deceptive descriptions masking their true functionality. User reviews frequently warn others about unauthorized asset transfers, mirroring past security episodes such as a fraudulent Leather cryptocurrency wallet app that similarly targeted digital asset holders before being removed.
Experts recommend that users exercise caution by navigating to application download pages directly from official project websites rather than searching blindly within app store marketplaces. Avoiding apps with minimal user engagement, few reviews, or mismatched developer identities helps mitigate these widespread social engineering risks.
Sources
- BleepingComputerFake crypto app on Apple App Store linked to $23K wallet theft
Continue chronologically
Related entity coverage
Related stories
Apple Backports CoreGraphics Zero-Day Patches to Older Devices
Apple has backported security patches for a CoreGraphics zero-day vulnerability to older iPhone and iPad models following targeted attacks.
Mozilla, Google, and Apple Block Weak eMudhra Certificates
Major tech vendors including Mozilla, Google, and Apple have blocked eight compromised eMudhra intermediate certificates featuring critically weak private keys.
Apple to Introduce 'Made for iPhone Duo' App Store Badge
Apple is rolling out a new App Store badge to highlight applications optimized for its new foldable device, the iPhone Duo, ahead of its launch.
Apple Updates App Store Rules to Explicitly Ban AI Nudify Apps
Apple has updated its App Store guidelines to more explicitly ban AI-powered nudify apps that generate nonconsensual intimate imagery.