Cloudflare Introduces Full Transaction Detection for WAF
Cloudflare has expanded its web application firewall by adding full transaction detections and response rules to evaluate HTTP requests alongside their corresponding responses.
 Radwan AbdulhadiEditor and technology writer
Expanding Web Application Firewall Capabilities
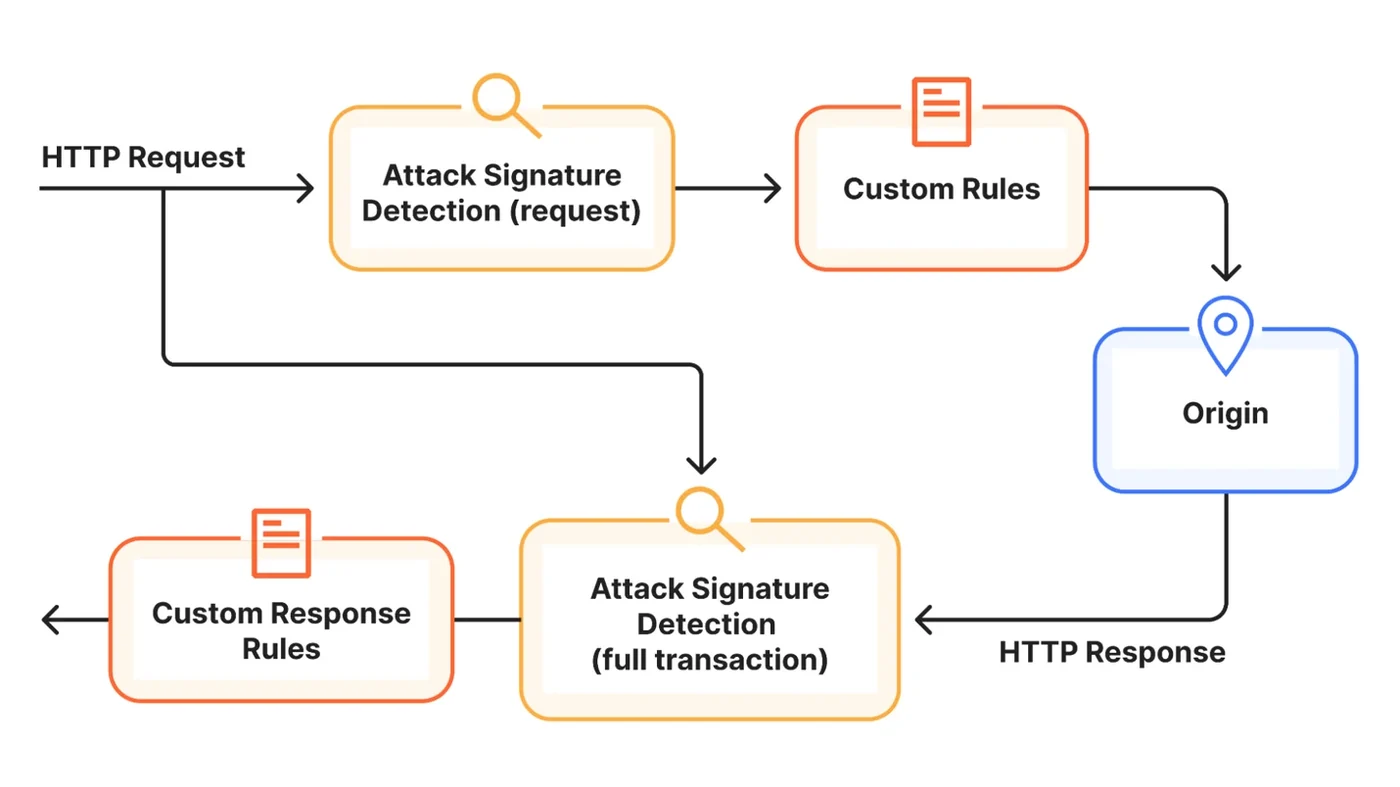
Cloudflare has announced an expansion to its web application firewall, introducing full transaction detections and response rules. According to the company, these additions allow the system to evaluate each HTTP request alongside its response to identify evidence of exploitation, answering both whether a request looks malicious and what happened when the application handled it. Further details are available from Cloudflare Blog in the original source material.
The platform update helps security teams address modern vulnerabilities uncovered by frontier models and persistent AI agents. These automated tools can adapt payloads and chain vulnerabilities, making application responses critical for determining whether an attack attempt succeeded.
Correlating Requests and Responses
While inspecting incoming requests remains essential for stopping recognizable attacks, some threats only become clear when evaluated alongside what the origin returns. A suspicious input followed by a response exposing sensitive data tells a different story than the same input followed by a rejection or error.
Full transaction detection correlates attempted access with response content, providing stronger evidence of sensitive data exposure than either signal alone. For example, in a path traversal attempt, request inspection can recognize the attempt, but the response provides the missing evidence needed to confirm if a private file was exposed.
Detection and Mitigation Separation
The new capabilities extend Cloudflare's always-on application security framework, with detection results made available in Security Analytics to support investigations. By design, detection and mitigation are kept separate so that security teams can inspect traffic behavior and understand which endpoints and signatures are involved before applying a blocking policy.
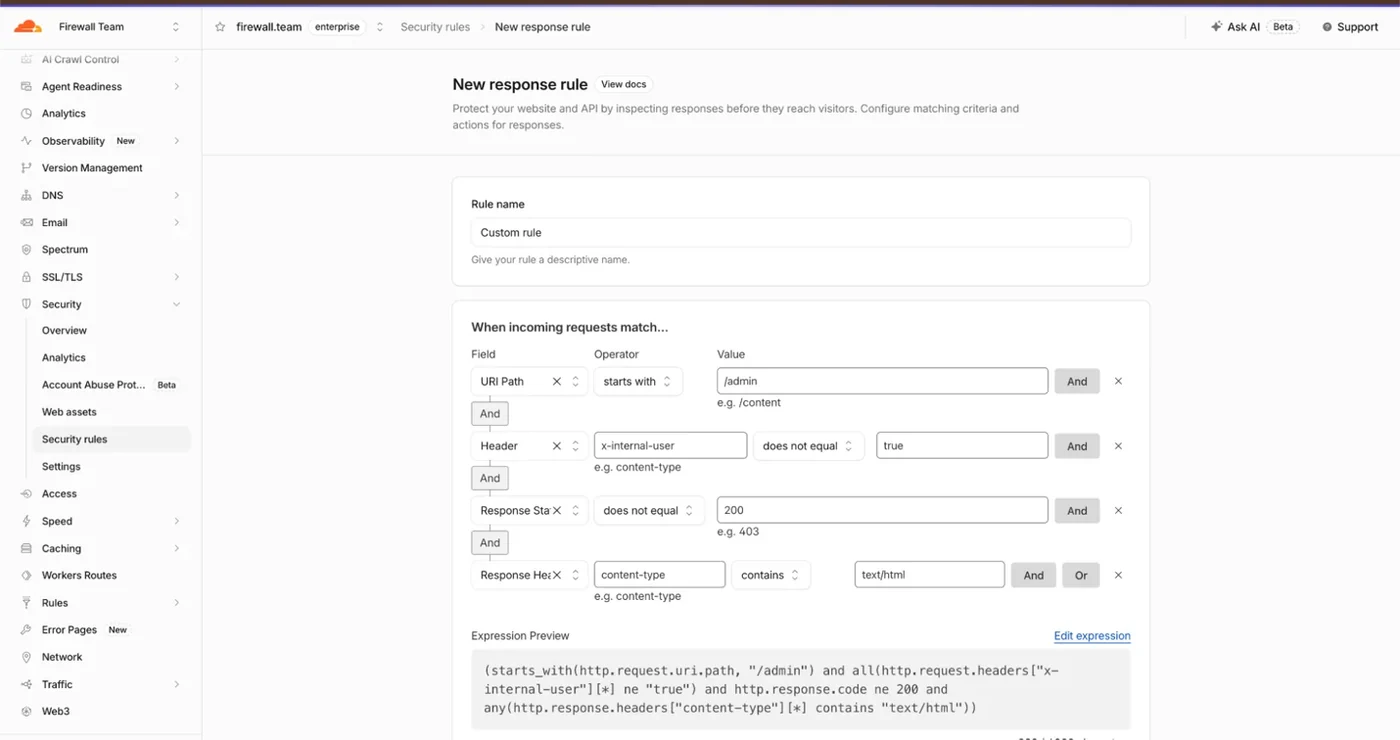
The platform introduces new fields for confidence values and categories associated with matching signatures, mirroring existing request detection fields. Security teams can use these fields within custom rules or managed protections.
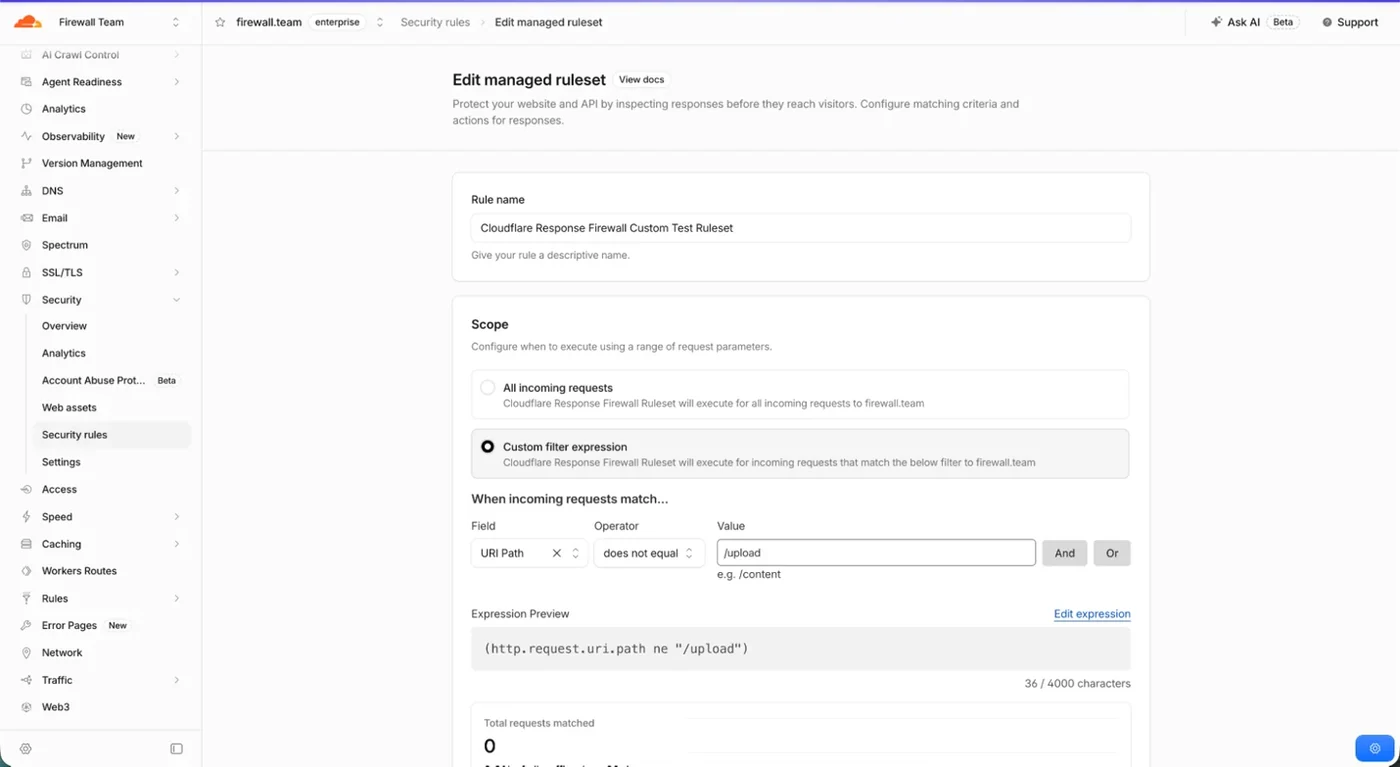
Response Phase Controls and Availability
Response custom rules allow teams to turn full transaction detections into inline protection by blocking a matching origin response before it reaches the requester. When a rule matches, Cloudflare replaces the origin response with a WAF block page and an HTTP 403 status or a custom response.
Cloudflare is making these new capabilities generally available across all service tiers, including Free plans. The initial managed protections built using this framework focus on the recently disclosed php2shell vulnerability, with coverage expected to expand over time to include data exposure and exfiltration signals.
Sources
- Cloudflare BlogIntroducing full transaction detection for Cloudflare WAF
Continue chronologically
Related entity coverage
Related stories
Cloudflare Deploys WAF Protections for php2shell Vulnerabilities
Cloudflare has automatically deployed default WAF rules to protect web applications against newly disclosed php2shell vulnerabilities in PHP.
Cloudflare Launches Application Profiles for Positive Security
Cloudflare introduces Application Profiles to enforce positive security policies, analyzing HTTP request structures to reduce attack surfaces.
Cloudflare Introduces Threat Signals for Free
Cloudflare launches Threat Signals and expands access to its Threat Events Platform, bringing agentic open-source intelligence to every account.
Cloudflare Launches Private Origins for All Customers
Cloudflare services for private origins are now generally available, bringing WAF, bot management, caching, and Workers to private applications.