GitHub Enterprise Cloud Launches License Compliance
GitHub Enterprise Cloud customers can now manage dependencies' licenses at scale using sophisticated, ruleset-based checks that enforce centralized policies.
 Radwan AbdulhadiEditor and technology writer
General Availability for GitHub Enterprise Cloud
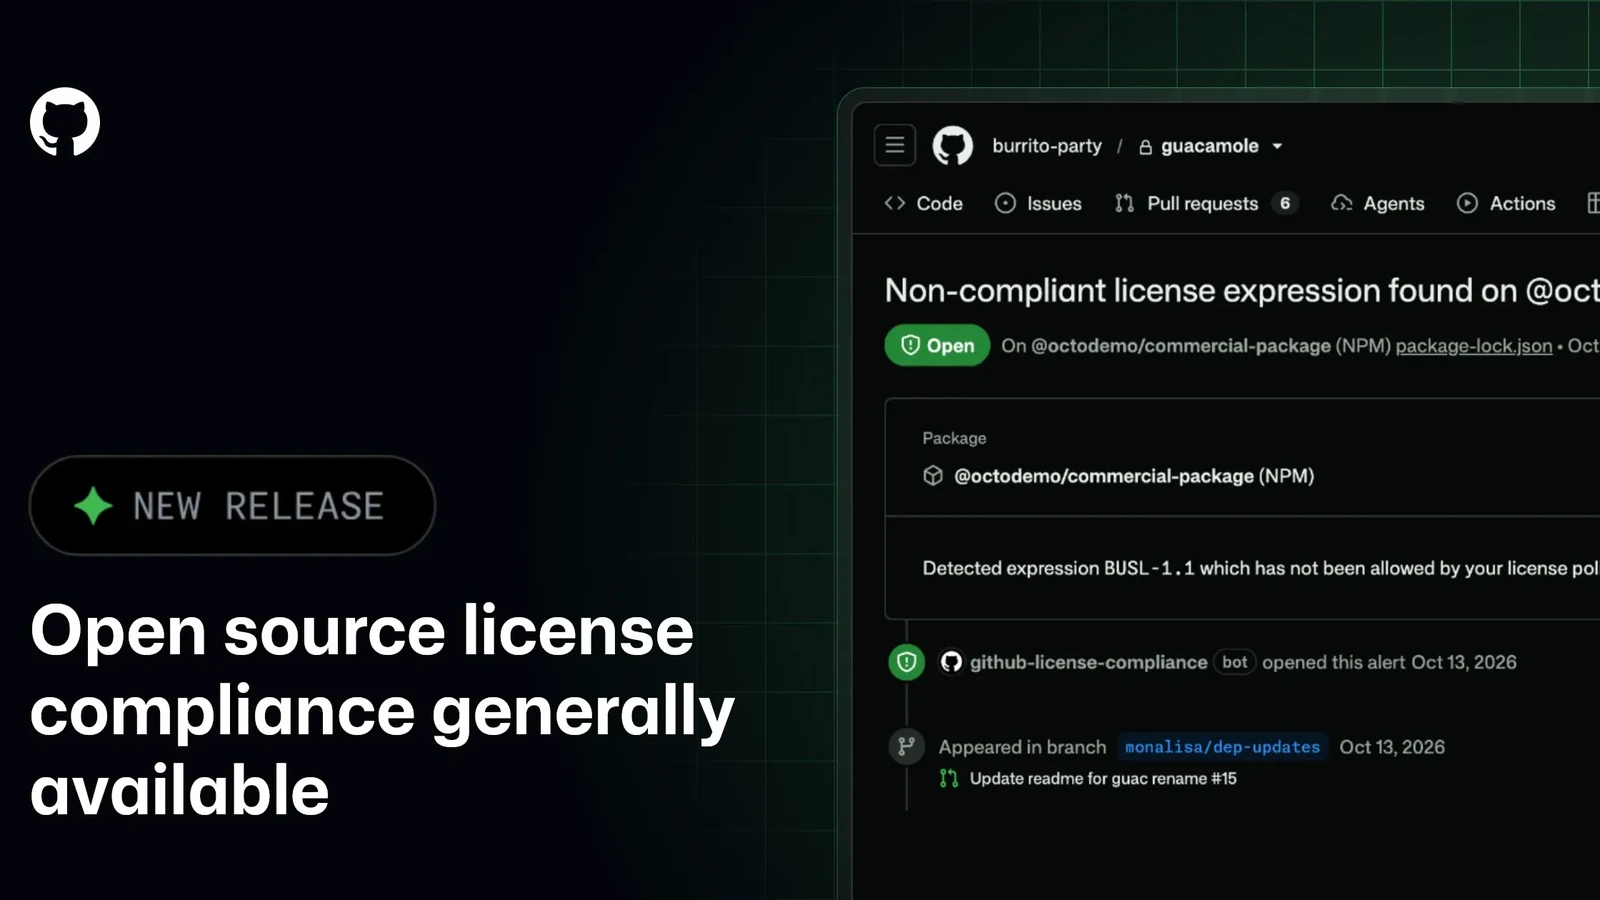
Enterprises can now manage their dependencies’ licenses at scale with sophisticated, ruleset-based checks that enforce a centralized policy. Open source license compliance is now generally available for GitHub Enterprise Cloud customers, including data-resident GHEC, for repositories with GitHub Code Security enabled. Detailed setup instructions can be found by reviewing documentation on About open source license compliance.
Expanding Dependency Review and Pull Request Checks
The open source license compliance feature expands on the capabilities of the dependency review action by introducing an enterprise-wide license policy. The policy is activated by targeting repositories with a ruleset that uses a new 'Require license compliance results before merging' condition, which functions similarly to existing code scanning conditions.
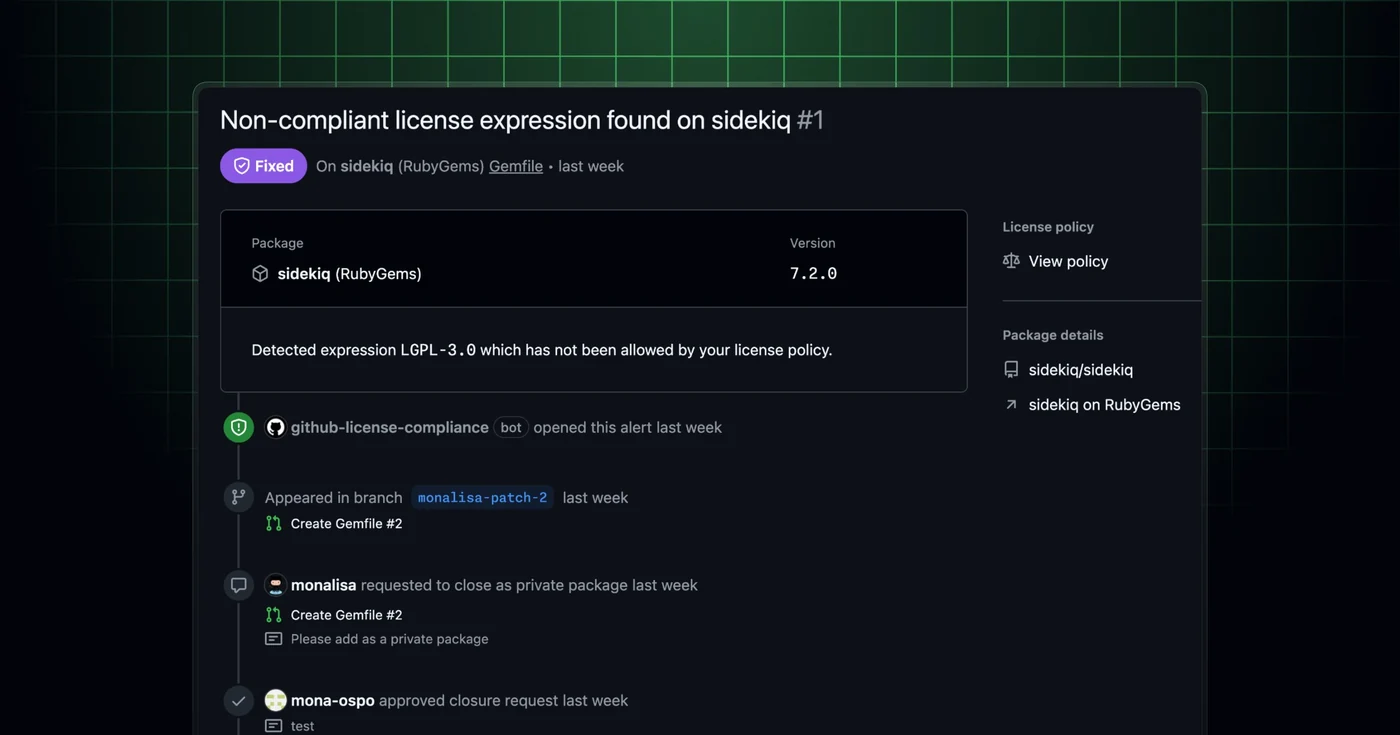
When developers open pull requests that add or modify dependencies, license checks automatically ensure each new or changed dependency has an acceptable license. The feature annotates the pull request with a message about each noncompliant dependency. These annotations must be addressed by removing or replacing the dependency, amending the license policy, or creating package exceptions.
New Enterprise Roles and Management Console
Open source license compliance introduces a new predefined enterprise role called Enterprise Open-Source License Manager. This role can be assigned to individuals or teams who should review and approve closure requests. Policy managers receive email notifications regarding pending requests and can manage them directly from the enterprise console.
Improvements Since the Public Preview
Since the public preview release in June, several key improvements have been introduced. License information is now available for GitHub Enterprise Cloud data residency customers, enabling the license compliance feature while also populating the dependency graph and Software Bill of Materials (SBOM) exports with license data.
Additionally, license policy changes now emit audit log events designed for integration with external systems of record. Developers can also engage with the broader community by visiting the GitHub Community platform.
New API Endpoints for Integration and Coding Agents
The release includes new API endpoints for downloading, updating, and replacing the enterprise license policy. Furthermore, a new API endpoint has been established for checking whether packages comply with organizational policy, allowing coding agents to avoid recommending or incorporating packages that violate license usage rules. Information regarding these programmatic capabilities is detailed in the REST API endpoints for dependency-graph documentation.
Sources
- GitHub ChangelogOpen source license compliance generally available
Continue chronologically
Related entity coverage
Related stories
GitHub Actions Workflow Lockfiles Enter Public Preview
GitHub Actions workflow dependency lockfiles are now in public preview for GitHub Enterprise Cloud, offering enhanced security and consistency.
GitHub Introduces Dependabot Reachability Analysis Preview
GitHub launches reachability analysis for Dependabot alerts in public preview, helping teams prioritize JavaScript and TypeScript vulnerabilities.
GitHub Introduces Improved Detection for Withdrawn Dependabot Alerts
GitHub has rolled out two key updates to help developers easily detect withdrawn Dependabot alerts via webhooks and REST API updates.
GitHub Introduces Repository Custom Runner Settings for Dependabot
Repository administrators can now configure runner types, custom labels, and runner groups for Dependabot version and security updates.