Criminal IP Introduces AITEM for Attack Surface Management
Criminal IP has announced AITEM, an AI-powered threat exposure management approach designed to connect exposure discovery with investigation, risk prioritization, and response.
 Radwan AbdulhadiEditor and technology writer
The Evolution of Attack Surface Management
Criminal IP by AI SPERA, a cyber threat intelligence platform delivering decision-ready intelligence and attack surface visibility to security teams worldwide, has announced that it will participate in GovWare 2026 in Singapore. As security operations increasingly move beyond asset discovery toward understanding, prioritizing, and responding to exposure, the organization is introducing AITEM (AI-Powered Threat Exposure Management) as its vision for the next evolution of Attack Surface Management.
Traditional ASM tools have historically served a critical purpose by helping organizations discover internet-facing assets such as servers, domains, IP addresses, and admin panels before attackers can find them. However, industry stakeholders note that discovery alone is no longer sufficient to combat modern threats. Organizations can learn more by checking out the details on [Introducing AITEM: AI-Powered Threat Exposure Management](https://www.criminalip.io/contact-us?mtm_campaign=GovWare_2026&mtm_source=BleepingComputer&mtm_medium=press) provided by the platform.
According to AI SPERA CEO Byungtak Kang, seeing a threat and responding to it are completely different challenges. Building a safer cyber world requires a distinct shift from visibility to action. Organizations today maintain more visibility than ever, yet many still struggle to effectively prioritize and act upon the risks revealed by these scans. By applying artificial intelligence to filter noise, enrich context, and guide investigations, security teams can concentrate on the exposures that matter most and respond in real time, ultimately turning raw insight into meaningful action.
Bridging the Gap Between Detection and Action
The operational gap between detection and action has become even more critical as artificial intelligence lowers the operational barrier for attackers. Automated scanning tools, published proof-of-concept exploit codes, and AI-assisted vulnerability discovery mean that malicious threat actors can identify and target exposed assets faster than ever before. Consequently, the primary challenge for defenders is no longer just visibility, but rather the overall speed of response.
AITEM expands the traditional scope of Attack Surface Management far beyond an external asset inventory. Powered directly by Criminal IP threat intelligence, the system brings exposure across external assets, open-source intelligence (OSINT), dark web data, internal infrastructure, Shadow AI, leaked data, and emerging vulnerabilities into a comprehensive threat exposure management framework.
Instead of stopping short at basic asset discovery and generic risk scores, AITEM is engineered to connect fragmented security findings with the deep context that security teams need to thoroughly investigate, prioritize, and respond to incidents.
Four Stages of AI-Powered Exposure Management
The newly introduced AITEM framework applies artificial intelligence across four distinct stages of exposure management. First, in the Detect stage, the platform connects emerging threats and vulnerabilities directly to the products, services, and assets that physically exist within a given organization's operational environment.
Second, during the Investigate stage, the system allows security teams to query assets, exposures, vulnerabilities, and security findings using natural language while seamlessly bringing relevant context together in a single centralized location.
Third, the Prioritize stage evaluates exposure by utilizing organization-defined risk criteria alongside real-world exploitability and active attacker behavior, rather than relying exclusively on generic vendor risk scores.
Finally, the Automate stage turns prioritized findings into actionable alerts, tickets, and workflow actions that can be routed directly to the appropriate response teams, helping transition critical exposures efficiently from initial detection toward complete remediation.
Context and Infrastructure Integration
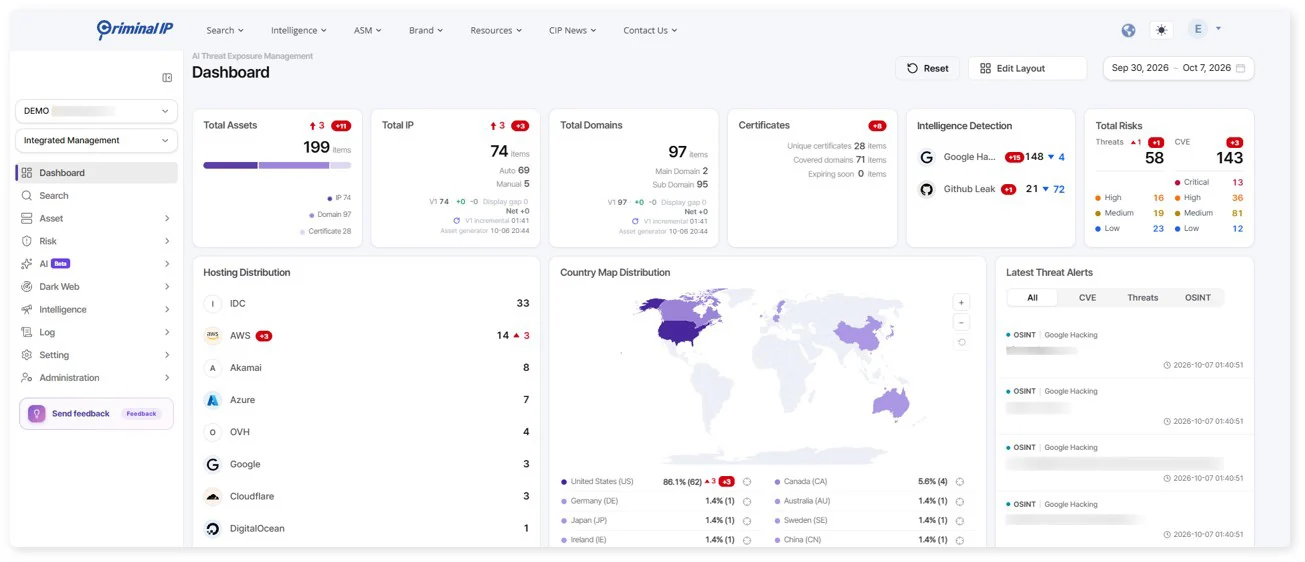
AITEM is built entirely upon underlying Criminal IP threat intelligence, which infuses real-world context into exposure management well beyond standard vulnerability data alone. Open ports, exposed services, vulnerabilities, connected infrastructure, historical abuse records, active scanner behaviors, threat attribution, and malicious infrastructure are all brought together to help security teams comprehend not just what is currently exposed, but what is actively happening around that exposure and why it matters.
The strategic direction that Criminal IP is pursuing with AITEM reflects a much broader industry evolution observed across the global cybersecurity landscape. During major security events like RSAC 2026, agentic AI, AI Security Operations Centers (SOC), and Shadow AI emerged as prominent themes, while leading vendors continued their transition from siloed security tools toward tightly integrated, AI-driven security operations.
As CEO Byungtak Kang emphasized, competition in the attack surface management sector is no longer determined by who discovers the greatest number of assets. Instead, success will belong to those who can operate with greater speed, respond more effectively, and mobilize their organizations. AI should handle repetitive analytical labor, leaving human operators to focus on judgment, accountability, and critical prioritization.
Presentation at GovWare 2026
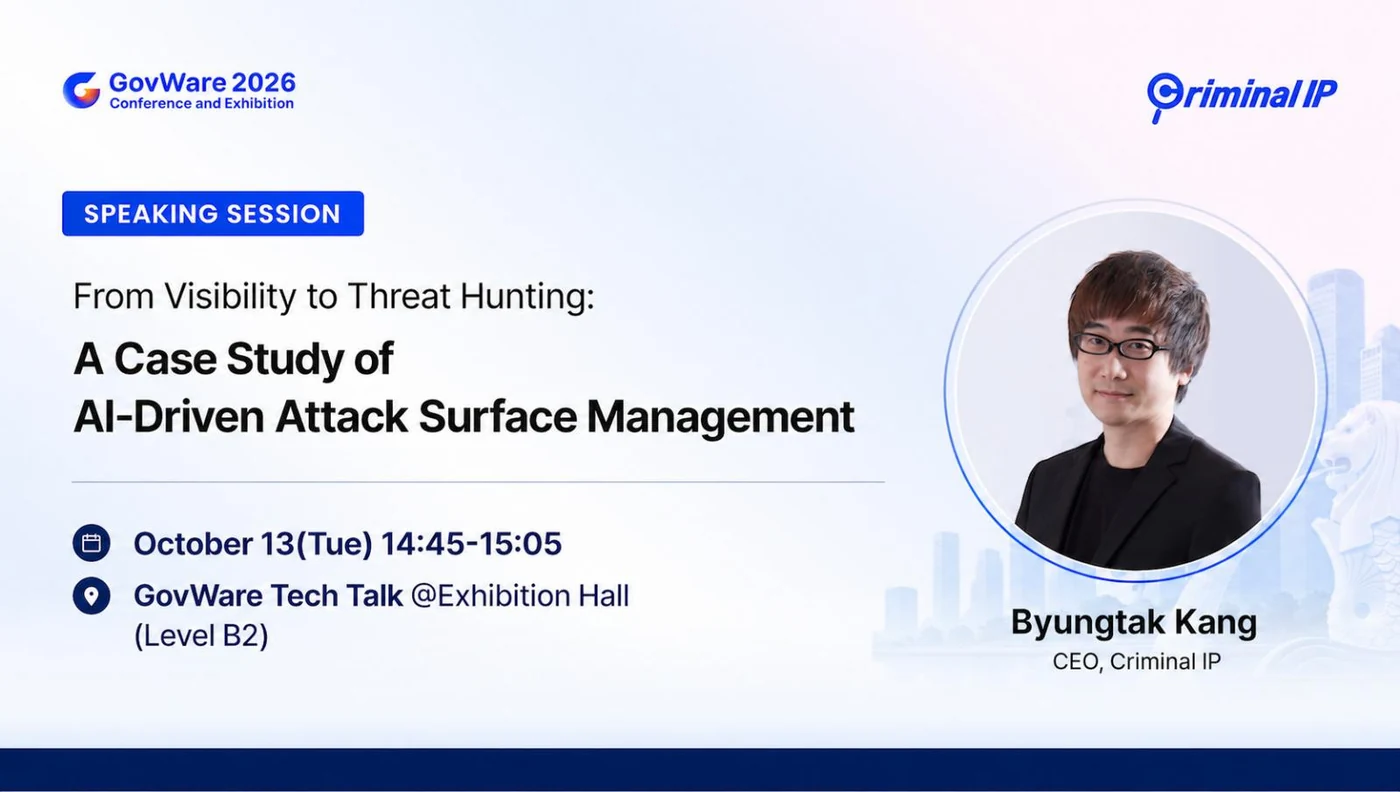
As part of the upcoming conference program at GovWare 2026 in Singapore, AI SPERA CEO Byungtak Kang will present a dedicated session titled “From Visibility to Threat Hunting: A Case Study of AI-Driven Attack Surface Management.”
Drawing heavily from real-world examples, the scheduled presentation will explore how comprehensive threat intelligence and attack surface visibility can support faster investigations and significantly more effective security operations, while examining the vital industry shift from merely discovering exposures to understanding and acting upon them.
Professionals wishing to engage further with the company can review resources or reach out directly by using the [Criminal IP](https://www.criminalip.io/contact-us) portal, or explore broader platform updates by visiting [www.criminalip.io](https://www.criminalip.io/?mtm_campaign=GovWare_2026&mtm_source=BleepingComputer&mtm_medium=press).
Sources
- BleepingComputerCriminal IP Introduces AITEM as the Next Evolution of Attack Surface Management
Continue chronologically
Related stories
Cloudflare Introduces Threat Signals for Free
Cloudflare launches Threat Signals and expands access to its Threat Events Platform, bringing agentic open-source intelligence to every account.
MITRE Releases ATT&CK v20 with AI Abuse and Water Utility Attacks
MITRE has released ATT&CK v20, introducing new techniques for AI prompt injection, MFA bypass, mobile malware, and attacks on water utilities.
Cloudflare Details Agentic Security Operations Harness
Cloudflare Managed Defense introduces an AI agent harness combining Workers, deterministic evidence collection, and global telemetry for threat analysis.
Cloudflare Unveils Adaptive Application Security Framework for AI Era
Cloudflare has introduced an adaptive security framework to combat AI-driven cyber attacks, connecting risk discovery, agent governance, runtime protection, and intelligence.