Targeted Ads Delivered Candiru Spyware in Zero-Click Attacks
A novel zero-click attack technique has utilized targeted online advertisements to deliver Candiru spyware directly to devices at the Al Jazeera Media Network without requiring any user interaction.
 Radwan AbdulhadiEditor and technology writer
Zero-Click Attacks via Targeted Ads
Researchers investigating the campaign referred to this technique as AdFection, highlighting that their report represents the first public technical confirmation of mercenary spyware being delivered through targeted online advertisements. A similar method was previously documented by Amnesty International involving ads that infected targets with Predator spyware without requiring any clicks.
The Discover-Tech Connection and AdFection Mechanics
Unlike previous vectors, AdFection was caught in real attacks and linked directly to the Israeli firm Discover-Tech. According to detailed findings published by Citizen Lab, the company acted as a bridge between mercenary spyware vendors and the wider advertising ecosystem.
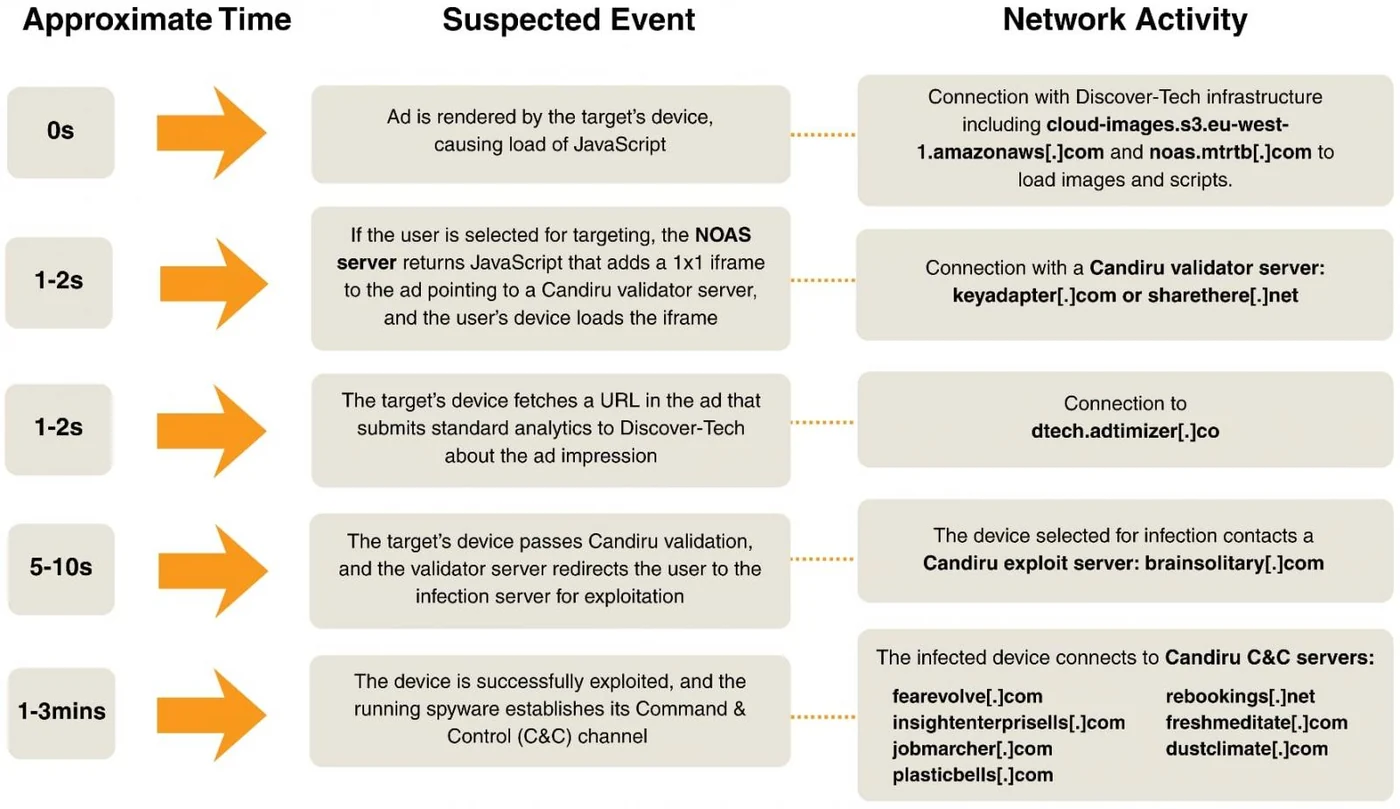
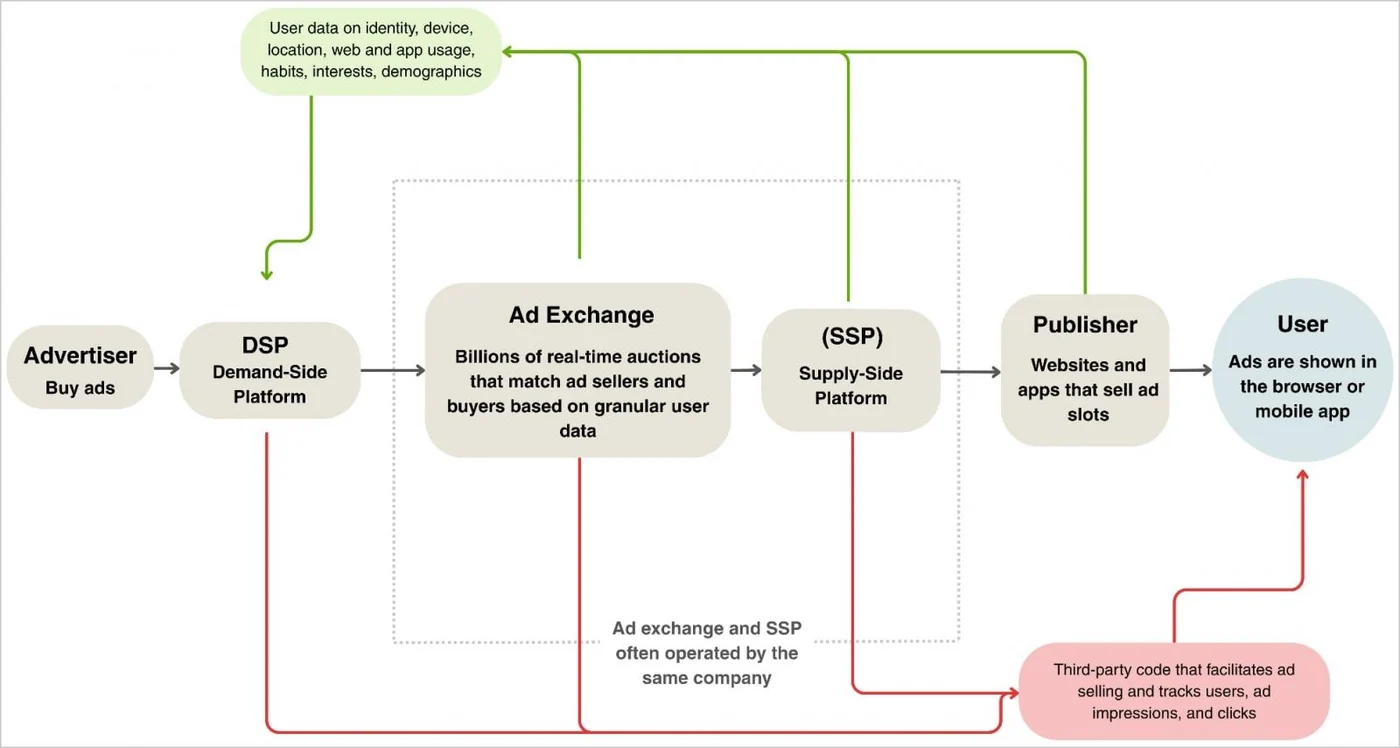
Discover-Tech allegedly permitted its customers to use its Controlium platform to profile, deanonimize, and fingerprint user devices, or target specific devices with malicious code. The company purchased ad placements through mainstream advertising networks and exchanges, embedding JavaScript within ads that contacted a NOAS server whenever the ad was rendered on a user device.
Through parameters such as IP addresses and ad identifiers, the NOAS server determined whether a target was eligible to receive the malicious JavaScript code. Devices that matched target profiles received the code, while other devices rendered the ad normally, helping to maintain the stealth of the operation.
Impact on Al Jazeera and Attribution to Candiru
Al Jazeera provided researchers with evidence of attacks targeting at least 45 devices between 2024 and 2025. Network logs examined during the investigation showed a clear sequence from Discover-Tech infrastructure to Candiru validation servers and eventually to spyware command-and-control servers.
Furthermore, researchers recovered a DLL file from a compromised Windows system and attributed it with high confidence to Candiru. This attribution was based on infrastructure and code overlaps with previously captured samples associated with the Israeli spyware vendor, which has a history of developing surveillance tools like DevilsTongue.
Candiru is an Israeli spyware vendor that officially sells its surveillance products exclusively to governments. Its tools have historically been deployed via zero-day exploits against journalists, activists, and other high-profile individuals.
Scope of the Advertising Operation and Industry Response
While Al Jazeera is one confirmed target of these attacks, research indicates the broader advertising operation placed 3.77 billion bids and won 442 million auctions between March and June 2026. Ads assessed to carry attacker script tags appeared across more than 75,000 Android and iOS applications, as well as over 120,000 websites, though these numbers reflect ad delivery rather than direct infections.
Following notification by researchers, major advertising organizations and technology companies—including Google, IAB Europe, Beeswax, Eskimi, and Vungle—took swift action to remove offending accounts and block access to the involved domains.
Sources
- BleepingComputerZero-click attacks used targeted ads to deliver Candiru spyware
Continue chronologically
Related entity coverage
Related stories
Targeted Ads Delivered Zero-Click Exploits for Spyware
Researchers reveal that mercenary hackers laced targeted ads with zero-click exploits to install sophisticated spyware on devices without user interaction.
Israeli Ad Firm Used for Candiru Spyware Delivery
Citizen Lab uncovers AdFection, an operation where an Israeli ad firm delivered zero-click Candiru spyware via targeted advertisements.
SS7 and Diameter Flaws Expose Mobile Networks
Explore how vulnerabilities in SS7 and Diameter signaling protocols allow attackers to track phone locations, intercept calls, and bypass 2FA.
OpenCode Hack Exposes API Keys in AI Distillation Attacks
The open-source AI coding project OpenCode suffers a security breach exposing API keys to a large-scale AI distillation attack.