
CISA Warns Admins to Immediately Fix Ivanti Flaw
The U.S. Cybersecurity and Infrastructure Security Agency has ordered network defenders and federal agencies to address an active Ivanti Connect Secure zero-day vulnerability.
 Radwan AbdulhadiEditor and technology writer
CISA Issues Urgent Warning Over Ivanti Zero-Day
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has urged security teams to immediately patch an Ivanti Connect Secure (ICS) flaw exploited in zero-day attacks since at least October 1st, according to a report by Sergiu Gatlan. Tracked as CVE-2026-104935, this high-severity authentication bypass vulnerability lets remote threat actors without privileges execute arbitrary commands on targeted ICS systems in low-complexity attacks that do not require user interaction.
Ivanti released updated ICS versions to address the security flaw and warned customers to act immediately because of limited exploitation in the wild. While Ivanti did not share additional information about ongoing attacks targeting the vulnerability, cybersecurity researchers have uncovered broader campaigns utilizing the flaw.
Threat Actors Chain Exploits for Root Access
Cybersecurity firm Volexity reported that an unknown threat actor tracked as UTA0576 has been chaining this security issue with two other flaws in attacks since at least October 3rd. Additional details regarding the attack chain were published when Volexity said that the exploit combined an authentication bypass, remote code execution, and a privilege escalation vulnerability.
Threat intelligence firm Defused also confirmed Volexity's report, noting that it first found evidence of attackers abusing the vulnerability in the wild on October 1st. The post-exploitation actions undertaken by the threat actors notably targeted Active Directory credentials and secrets, including Local Administrator Password Solution passwords and BitLocker recovery keys.
Global Exposure and Federal Directives
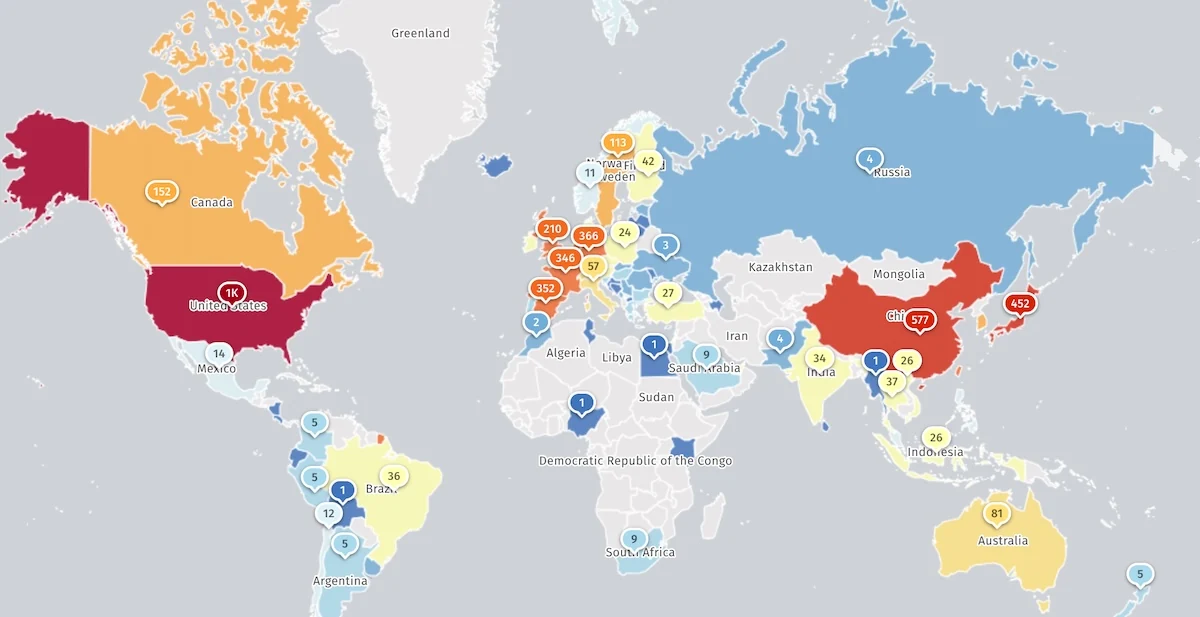
Internet threat watchdog Shadowserver now tracks over 5,600 Internet-exposed hosts with ICS fingerprints. However, available data does not specify how many of these systems are secured against ongoing attacks or how many function as honeypots designed to trap malicious activity.
In response to the active exploitation, CISA added the vulnerability to its list of actively exploited security flaws and ordered federal agencies to secure their networks as mandated by Binding Operational Directive 26-04. The agency also issued a separate advisory urging all network defenders to patch immediately and check for signs of compromise.
Mitigation and Remediation Guidance
Because threat actor commands execute directly in memory, Ivanti's Integrity Checker Tool may not always detect evidence of exploitation. CISA warned that organizations seeking to determine compromise will need to conduct thorough network and memory forensics.
If defenders discover compromised appliances, CISA recommends that administrators create a backup of the appliance configuration before performing a factory reset and upgrading to the latest version. For virtual and cloud systems, administrators should rebuild the virtual instance entirely.
Sources
- BleepingComputerCISA warns admins to immediately fix Ivanti flaw exploited as zero-day
Continue chronologically
Related stories
Ivanti Patches Two More Connect Secure Zero-Days
Ivanti releases security updates for two additional Connect Secure gateway flaws chained in zero-day attacks since October, following a prior bug fix.
Ivanti Patches Two Zero-Days in Connect Secure Attack Chain
Ivanti has issued security updates for two additional Connect Secure zero-days that attackers chained with a previously disclosed VPN vulnerability.
Ivanti Connect Secure Zero-Day Chain Exploited in the Wild
Ivanti warns of a high-severity Connect Secure zero-day chain exploited in the wild, granting attackers unauthenticated root access to fully patched VPN appliances.
CISA Confirms Active Exploitation of Maximum-Severity GitLab Flaw
CISA confirms active exploitation of a maximum-severity GitLab vulnerability tracked as CVE-2026-97229 and urges administrators to apply patches immediately.
