Hackers Exploited PHP Flaws Days Before Patch Release
Newly released research indicates that critical PHP vulnerabilities were actively targeted by bad actors days before official patches and public disclosures were made available.
 Radwan AbdulhadiEditor and technology writer
Early Exploitation Discovered
The internet's mad scramble to patch a pair of critical vulnerabilities in PHP, a widely used web scripting language, arrived too late to stop every attack. According to details released by [Amazon Web Services](https://www.wired.com/tag/aws/), at least one actor started attempting to exploit the bugs—known collectively as PHP2Shell—on October 17, four days before the public revelations.
The Wednesday release of fixes for these critical security issues caused administrators and security staff to race to identify and patch vulnerable websites and apps. Attackers inevitably reverse engineered the fixes to learn how to exploit the flaws, while some governments and other groups proactively took key websites down in anticipation of the release.
Honeypot Activity and Anonymized IPs
[Amazon Web Services](https://www.wired.com/tag/aws/) analysts spotted the October 17 exploitation while reviewing activity on one of their honeypots—intentionally vulnerable web servers designed to help researchers study attack methods and trends. The attempt originated from an IP address linked to a commercial anonymization network, such as a proxy network or [VPN](https://www.wired.com/gallery/best-vpn/).
CJ Moses, AWS's chief information security officer, noted that while the vulnerability was under embargo, targeting a honeypot from an anonymized IP address suggests the activity was conducted by a threat actor. However, it remains unclear how the actor acquired exploit information prior to disclosure.
Broad Exploitation Across the Internet
Proof-of-concept exploits for PHP2Shell began emerging publicly, with some appearing hours before the official public disclosure. In the hours leading up to the announcement, AWS researchers observed multiple exploitation attempts anonymized using various providers with seemingly diverse attack goals, pointing toward multiple different threat actors.
While technical analysis remains ongoing and it is unclear if any of the early attempts succeeded in real-world systems, Moses confirmed that [Amazon Web Services](https://www.wired.com/tag/aws/) notes the bugs are now being broadly exploited in the wild. The PHP Foundation did not immediately respond to requests for comment regarding the unfolding situation.
The Shifting Vulnerability Timeline
Although the exact origin of the October 17 activity remains uncertain, AWS emphasizes that these findings highlight the need for coordinated vulnerability disclosure to evolve and speed up. Global access to modern tools can [accelerate vulnerability analysis](https://www.wired.com/story/kernel-panic-ai-vulnerability-explosion/) and allow [less technically proficient actors](https://www.wired.com/story/ai-guardrails-arent-stopping-criminal-hackers/) to quickly develop new exploits.
Moses explained that the time from patch to working exploit is shrinking for structural reasons. In the past, most exploitation occurred after a public proof of concept was released, with a small number of capable actors building exploits while everyone else waited. That dependency is weakening as AI-assisted analysis makes it cheaper to turn a patch diff or advisory into a working exploit, allowing more actors to act within hours or even minutes of technical disclosure.
Sources
- WIREDHackers Exploited the PHP Vulnerabilities Days Before They Were Patched
Continue chronologically
Related entity coverage
Related stories
Microsoft Reveals Azure Quarterly Revenue in Dollars at $33.2B
For the first time, Microsoft has disclosed Azure's quarterly revenue in actual dollars, reporting $33.2 billion for the July-September quarter.
MoEngage Integrates 400 APIs With AgentCore Gateway
Discover how MoEngage scaled agentic workflows by converting 400 private REST APIs into secure tools using Amazon Bedrock AgentCore Gateway.
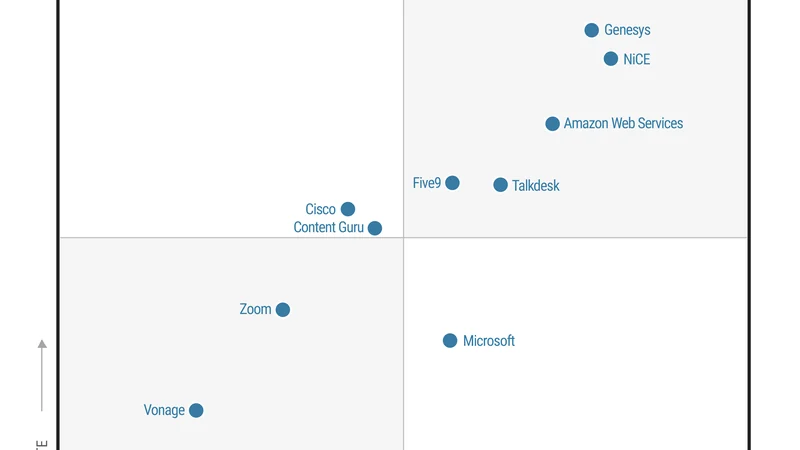
AWS Named Leader in 2026 Gartner CCaaS Magic Quadrant
Amazon Web Services has been recognized as a Leader in the 2026 Gartner Magic Quadrant for Contact Center as a Service for Amazon Connect.
Building Agentic Retrieval on Amazon Bedrock with AWS CDK
Learn how to build enterprise agentic retrieval on a Managed Amazon Bedrock Knowledge Base using the AWS CDK and Amazon Bedrock AgentCore.