Japan's GMO Group Urges Customers to Shut Down PCs Amid Ransomware Threat
Japan's GMO Group has instructed customers to disconnect their computers from the internet and shut down systems as part of an ongoing response to a cyberattack targeting its Onamae Desktop Cloud service.
 Radwan AbdulhadiEditor and technology writer
Onamae Desktop Cloud Breach Background
The security situation centers around a cyberattack on Onamae Desktop Cloud, a popular Virtual Private Server provider in Japan operated by GMO Internet, which is a member of the GMO Internet Group and ranks among the country's largest domain registrars.
Last week, the internet company announced that it detected an intrusion on October 20. This breach could have potentially installed malware on up to 26,739 customer servers. In response to the intrusion, the company shut down the affected servers and reduced service availability before launching a full-scale investigation into the incident.
Credential Exposure and Ransom Demands
While assuring customers that their payment information remained safe and unexposed, the company warned that MetaTrader 4 and MetaTrader 5 (MT4/MT5) credentials alongside trading-account details might have been compromised. GMO urged its users to immediately reset passwords and terminate any active sessions.
Subsequent updates from the company confirmed that data had been stolen during the security breach and that the attacker was demanding a ransom of ¥8 billion, equivalent to approximately $50 million. GMO stated firmly that it would not pay the ransom. Instead, the company announced plans to compensate each affected customer ¥5,000, roughly $30, for the inconvenience caused by the service disruption.
Escalation and Customer Warnings
On October 26, GMO warned that threat actors were planning to leak customer information online and trigger a ransomware payload that may have been planted on customer servers earlier in the breach. The situation escalated further the following day.
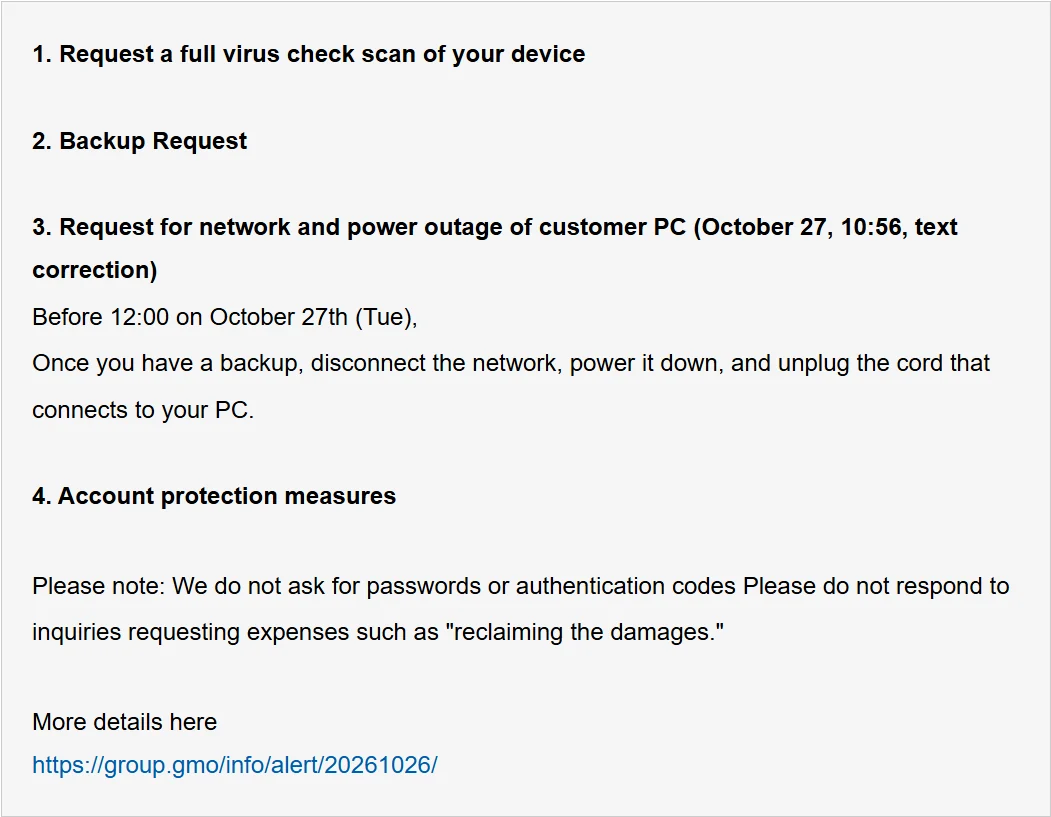
On October 27, the company asked customers to disconnect their PCs from the internet, shut them down, and unplug all cables before noon. This emergency directive was issued while GMO worked alongside Trend Micro to recover from the cyberattack.
Advising users on proper safety protocols, GMO stated: "Once you have a backup, disconnect the network, power it down, and unplug the cord that connects to your PC." The company also noted it was scanning customer systems to check whether any malware remained present, and offered equivalent PC replacements to individuals who suffered direct damage from a ransomware incident.
Data Leaks and Company Response
In a report published later, GMO confirmed that the threat actor had published company and customer data online, prompting internal efforts to verify the authenticity of the leaked files. For customers whose personal or account information was confirmed exposed, the company stated it would consider providing additional financial compensation.
Despite the threats and subsequent data leaks, it appears that the attacker never ultimately acted on their primary threat, as no ransomware was activated on customer machines. Reaffirming its refusal to negotiate with extortionists, the company warned individuals and members of the media not to disseminate the exposed information, announcing that it will pursue legal action against anyone who shares the leaked data.
Sources
- BleepingComputerJapan's GMO urges customers to shut down PCs amid ransomware threat
Continue chronologically
Related stories
Samsung Galaxy S26 Hacked Again at Pwn2Own Ireland
Security researchers successfully targeted the Samsung Galaxy S26 three more times on the second day of Pwn2Own Ireland 2026, exploiting zero-day flaws.
Germany Arrests Alleged Core Qilin Ransomware Member
Germany has arrested a Russian national suspected of being a leading member of the Qilin ransomware group following an extradition from Japan.
Advantest Discloses Data Breach From Ransomware Attack
Japanese chip testing giant Advantest discloses that personal information was stolen during a ransomware attack that occurred in February 2026.
Nikkei Discloses Third Data Breach in a Month
Japanese media giant Nikkei Inc. discloses its third data breach in a month, exposing 1.83 million personal records via a compromised development system.