Suspected ShinyHunters Hacker Rey Detained in Jordan
A key suspect linked to high-profile data theft and extortion attacks has reportedly been taken into custody by Jordanian authorities and is assisting international law enforcement.
 Radwan AbdulhadiEditor and technology writer
Detention and Law Enforcement Cooperation
A suspected member of the ShinyHunters hacking group, operating online under the alias 'Rey', has reportedly been detained in Jordan and is actively cooperating with the FBI. According to a report by a source told Reuters, Jordanian authorities took the suspect into custody, and he is now assisting international law enforcement agencies in locating other members of the extortion group.
Sources familiar with the arrest stated that the individual has been walking investigators through his electronic devices and digital communications. This direct assistance is aimed at identifying and tracking down alleged co-conspirators involved in global data theft campaigns, with law enforcement describing the cooperation as critical to ongoing arrests.
Background on the FBI Crackdown
The reported detention in Jordan unfolds amid a wider FBI crackdown targeting the ShinyHunters operation. The heightened pressure from authorities followed claims by the threat actors that they had breached FBI systems utilizing an alleged zero-day vulnerability before moving laterally into managed cloud environments.
Following the bureau breach, law enforcement actions expanded internationally, including the arrest of a suspect in Europe. In connection with that investigative track, Dutch police arrested a 24-year-old Amsterdam man on September 15 as part of the broader probe into the hacking syndicate's activities.
Impact on ShinyHunters Infrastructure
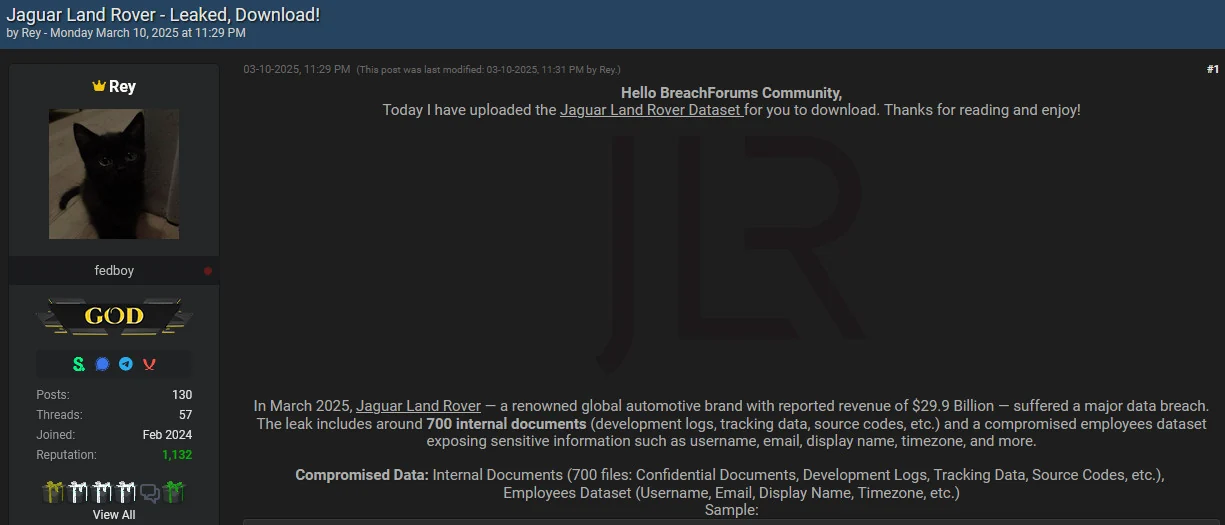
The operational pressure and recent detentions have introduced visible disruptions to the extortion group's digital footprint. On the same day the suspect was reportedly detained, associated affiliates abruptly shut down online messaging accounts, while the main data leak site went offline and key representatives ceased communication with media organizations.
Despite these temporary outages, new leak sites emerged online shortly after, indicating that remaining elements of the extortion operation continue to function. The group has historically targeted numerous prominent corporate environments, employing stolen authentication tokens to harvest customer data across multiple cloud architectures.
Previous Campaigns and Attack History
The threat actor known as Rey has been tied to multiple high-profile data theft incidents over recent years. Investigations and reporting have connected the moniker to campaigns targeting internal enterprise ticketing systems and corporate SaaS deployments, including cloud environments managed by major global technology corporations.
Security analysts and investigative journalists previously linked the online persona to Saif al-Din Khader through infostealer log analysis and direct communications. While early disclosures indicated attempts by the individual to distance himself from criminal collectives and engage with authorities, current developments point toward formal custody and active cooperation with international investigators.
Sources
- BleepingComputerShinyHunters hacker reportedly detained in Jordan, aiding FBI
Continue chronologically
Related stories
FBI Director Claims 605% Increase in Agency AI Usage
FBI Director Kash Patel reports a significant spike in AI adoption, citing increased efficiency in data triage and ongoing collaborations with tech leaders.
US Arrests Tech CEO Over $300M Nvidia Chip Smuggling Scheme
Federal authorities have arrested California tech CEO Greg Lui for allegedly smuggling over $300 million in restricted Nvidia chips to China.
Technical University of Denmark Breach Exposes Data for 200,000
A data breach at the Technical University of Denmark exposes personal information for up to 200,000 current and former users after an IAM compromise.
Frontline Education Data Breach Exposes School District Employees
Frontline Education is notifying school districts of a data breach after a third-party software vulnerability exposed employee information.