Ukrainian Ransomware Affiliate Sentenced to 70 Months in US Prison
Artem Aleksandrovych Stryzhak received a 70-month prison sentence in the United States following his involvement as an affiliate for both the Nefilim and Hive ransomware operations.
 Radwan AbdulhadiEditor and technology writer
Prison Sentence and Extradition Background
A 36-year-old Ukrainian national has been sentenced to 70 months in a United States prison for his participation in Nefilim and Hive ransomware attacks. The defendant, Artem Aleksandrovych Stryzhak, was living in Barcelona before being arrested by authorities in Spain in June 2024. Following his arrest, Stryzhak was extradited to face charges, as detailed by SecurityWeek.
The legal proceedings against Stryzhak progressed over several months following his transfer to US custody. Court documents show that he formally pleaded guilty in December 2025 to charges related to computer fraud conspiracy, culminating in the recent 70-month prison sentence handed down by federal authorities.
Nefilim Ransomware Operations and Affiliate Terms
According to court disclosures, Stryzhak joined the Nefilim ransomware operation as an affiliate in June 2021. During his active period as an affiliate through October 2021, he utilized custom malware to target large corporations and organizations in the United States, Canada, Australia, and other countries. One of his identified targets included an unnamed company operating within the oil and gas transportation sector.
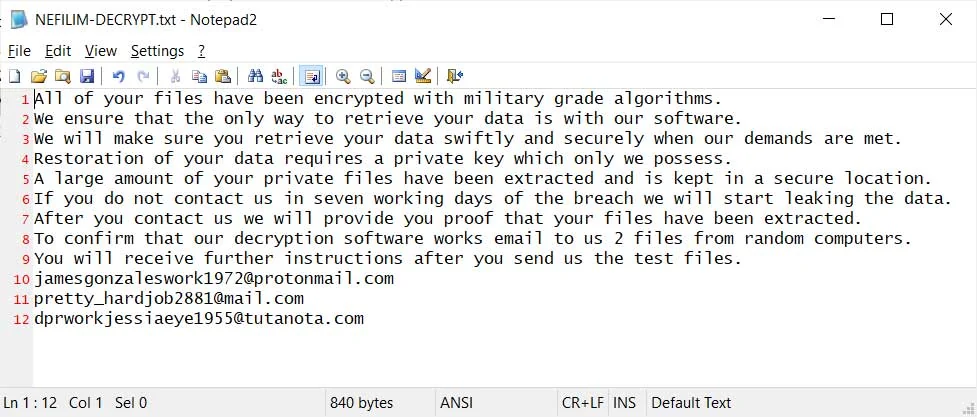
As part of the criminal arrangement, Stryzhak coordinated with Nefilim administrator Volodymyr Tymoshchuk. The terms required Stryzhak to pay the Nefilim administrators 20 percent of all ransom proceeds extorted from victims in exchange for access to the custom ransomware and associated decryption keys. To pressure targeted entities into paying, the group threatened to publish stolen data on dark web 'Corporate Leaks' sites managed by the gang's administrators.
Involvement with the Hive Ransomware Group
In addition to his work with Nefilim, court records indicate that Stryzhak was among the early affiliates to join the Hive ransomware group. Between June 2021 and January 2023, the broader Hive network struck more than 1,500 victim organizations worldwide. Stryzhak personally deployed Hive ransomware against seven specific organizations, which included a dental office, a healthcare provider, and multiple law firms.
In cases where victim organizations elected to pay the demanded ransoms, the cybercriminals provided decryption keys intended to help recover encrypted files. The attacks orchestrated by these ransomware affiliates caused severe disruptions, affecting critical operations and medical care during the COVID-19 pandemic.
Law Enforcement Impact and Ongoing Manhunt
Law enforcement officials emphasized the severe operational and financial damage inflicted by the criminal networks. Brett Leatherman, the FBI's Cyber Branch Operations Director, noted that Stryzhak and his co-conspirators worked with multiple ransomware groups to target businesses and hospitals, causing over $100 million in total losses and disrupting patient care.
While Stryzhak has been successfully prosecuted following his extradition, international law enforcement efforts continue. The US State Department is offering rewards of up to $10 million for information leading to the arrest or conviction of Volodymyr Tymoshchuk, who remains at large, along with up to $1 million for details concerning other leaders of the associated ransomware operations.
Sources
- SecurityWeekUkrainian Hive and Nefilim Ransomware Affiliate Gets 70 Months in US Prison
- BleepingComputerNefilim and Hive ransomware affiliate gets 70 months in prison
Continue chronologically
Related stories
FBI Seizes Domain of Russian Bulletproof Host Virtualine
The FBI has seized the domain of Virtualine, a Russian-speaking bulletproof hosting provider linked to ransomware, infostealers, and illicit services.
CISA Warns SafePay Ransomware Hit 600+ Critical Groups
CISA and international law enforcement report that the SafePay ransomware gang has breached over 600 critical infrastructure organizations globally.
Engineer Sentenced to Prison for Insider Cyber Extortion Plot
A former core infrastructure engineer has been sentenced to 32 months in federal prison for sabotaging his employer's industrial network.
Cybersecurity Executive Arrested in Federal Extortion Case
Canadian cybersecurity executive Edward Dubrovsky has been arrested in Pennsylvania in connection with an alleged extortion case tied to ShinyHunters.